[title] Sentinel
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/Threat Informed Defense/Configuration of Connector/
### Prerequisite
- You have to get the AIShield AI Security Monitoring App for Microsoft Sentinel from azure marketplace to get started with below steps.
### **Detail steps:**
** **Deploy AIShield - AI Security Monitoring for Microsoft Sentinel app to your Microsoft sentinel enabled log analytics workspace. Following component will be deployed with this installation.
1. **Data connector:** Azure Sentinel enables you to use data connectors to configure connections with AIShield Product.
2. **Parser**: Parser are built as user defined functions that transform data in existing table as the normalized schema.
3. **Analytics rules:** Scheduled analytics rules are based on built-in queries written by AIShield team to create security alert/Incidents.
Please follow below steps for AIShield - AI Security Monitoring connector installation:
1. Go to the azure marketplace and search for AIShield - AI Security Monitoring App for Microsoft Sentinel and click on get it now.
::Image[]{src="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/e41DbBUlPZ-53d4A_7G9e_image.png" signedSrc="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/e41DbBUlPZ-53d4A_7G9e_image.png" size="96" width="1600" height="655" position="center" caption="AIShield - AI Security Monitoring App for Microsoft Sentinel" alt="AIShield - AI Security Monitoring for Microsoft Sentinel "}
2\. It will redirect to the solution installation page and click on create button.
::Image[ ]{src="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/25-B4UN3vwbOa5SeQya0C_image.png" signedSrc="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/25-B4UN3vwbOa5SeQya0C_image.png" size="84" width="1449" height="659" position="center" caption}
After clicking on create, it will show you detailed components and details.
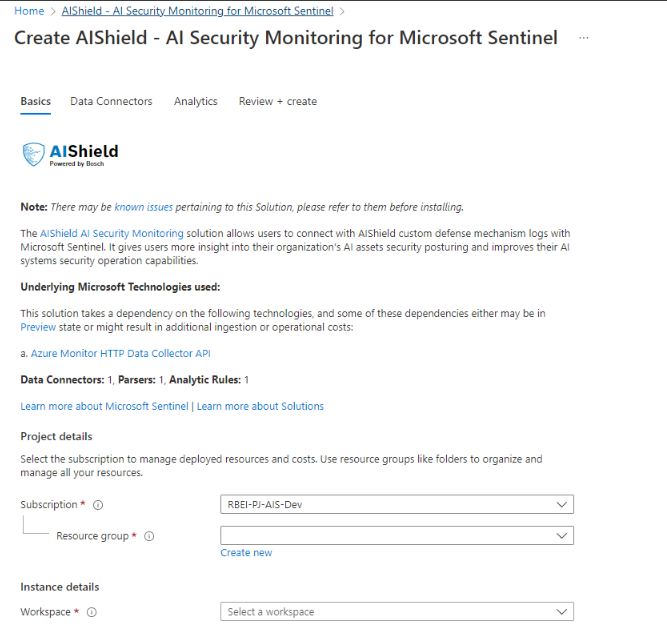
Select the subscription and resource in which Log analytics workspace resides. After that review the details and click on create. It will deploy all the components into the sentinel enabled logs analytics workspace.
You will be able to see deployed component using following steps.
1. **Data Connector : ** Go to the data connector page and search for the AIShield you will be able to see data connector page
2. **Parser : **Log analytics workspace -> go to function -> You will able to see parser
3. **Analytics rule : **Microsoft analytics is where you set up rules to find issues with the AI
After setting up everything,you'll get two important codes from the AIShield data connector page in your Microsoft Sentinel workspace:
1. customer ID (azure\_log\_customer\_id)
2. shared key (azure\_log\_shared\_key)
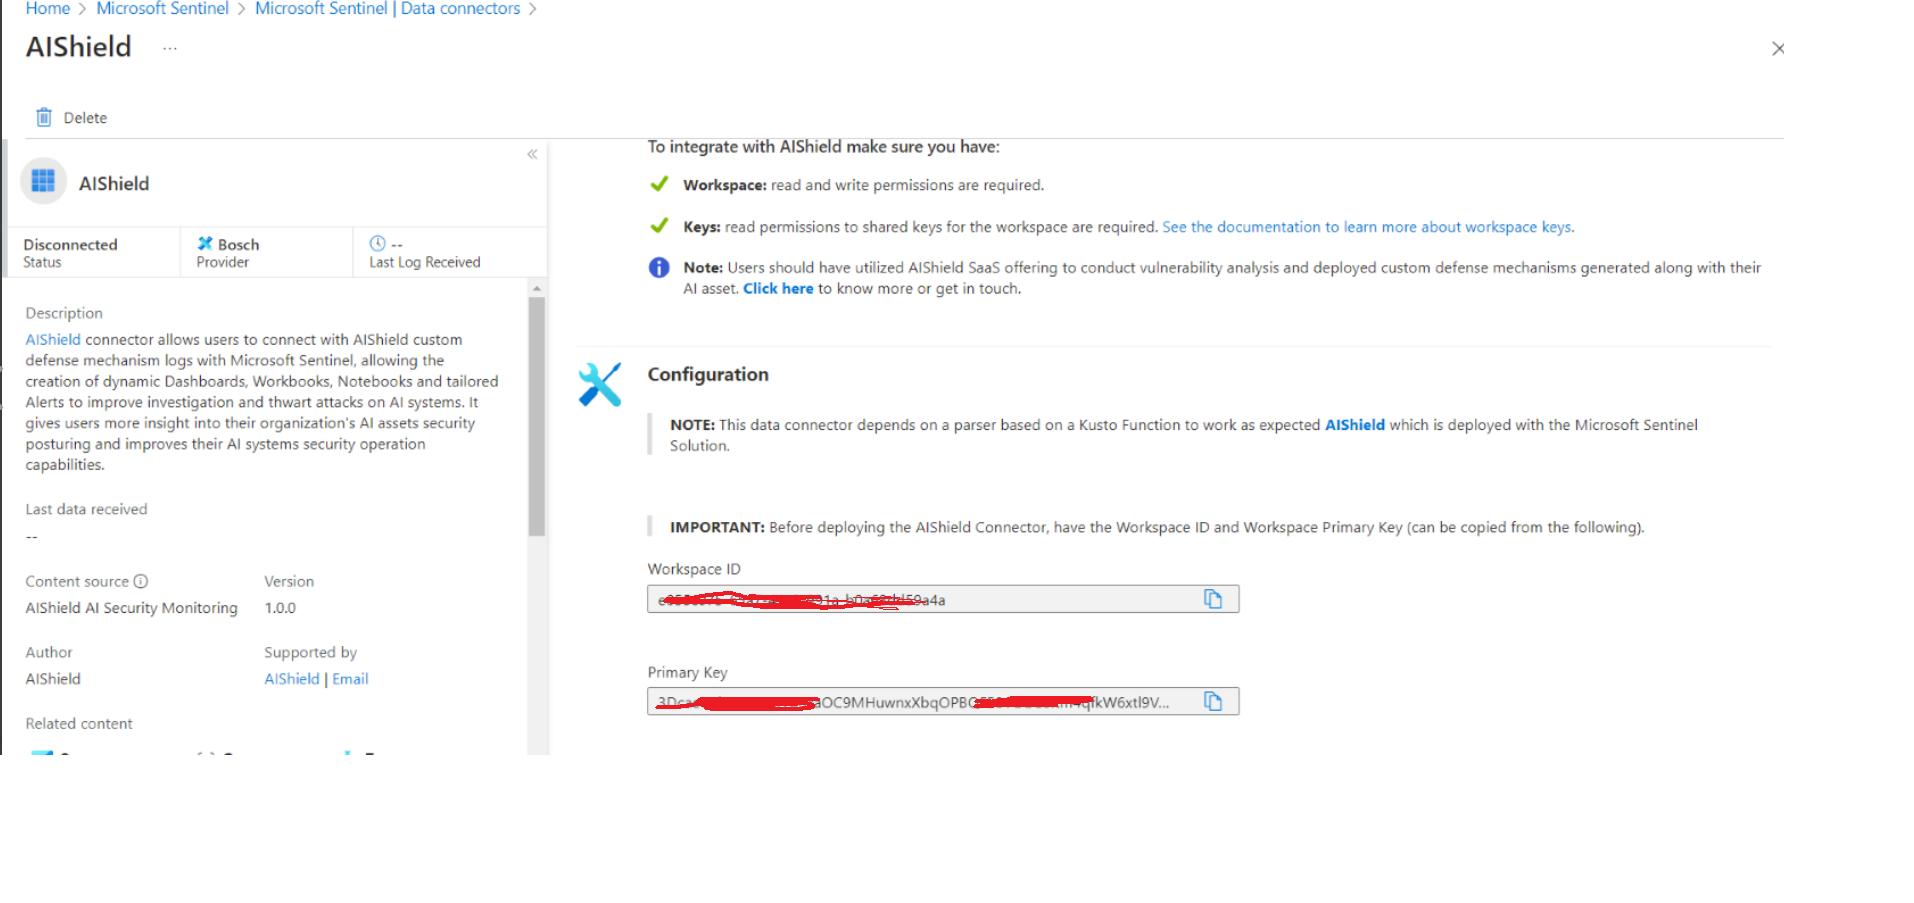
You need to take these codes and put them into the AIShield Threat Informed Defense app.
Please go through the Readme.txt file provided by AIShield Threat Informed Endpoint Defense (EDR) and follow the below defense connector steps for setup.
## Defense connector
You can download the defense artifact after your job runs successfully. The defense artifact will contain the defense model in .h5 and .onnx formats, one Python file, and a readme file describing the steps to follow to use it. Assuming you have already downloaded the artifact, you can follow the steps below to configure the defense with Azure Sentinel and Splunk Connector.
AIShield provided Threat Informed Defense Model zip folder contains the following files.
1\. Defense Model Architecture image
2\. Defense Model Classification Report image
3\. Defense Model Confusion Matrix Image
4\. Defense Model (h5 format)
5\. defense\_model (onxx format)
6\. Predict.py
7\. ReadMe.txt
Following steps describe the procedure to integrate and test AIShield provided Threat Informed Defense Model.
### Step 1: Install Python Packages
```python
pip install numpy
pip install tqdm
pip install tensorflow
pip install cv2
```
### Step 2: Import AISDefenseModel and necessary libraries
```python
from predict import AISDefenseModel
import tensorflow
import cv2
import numpy as np
```
### Step 3: Load the TensorFlow model
defense\_model\_path variable is used to store the file path or location on the local system where a defense model is expected to be found.
```python
defense_model = tensorflow.keras.models.load_model(defense_model_path)
```
### Step 4: Create AISDefenseModel with Connector
```python
model = AISDefenseModel(defense_model, azure_log_customer_id, azure_log_shared_key)
```
**Parameters**:
- `azure_log_customer_id`: Azure Object Id (Workspace Id) of your workspace to log event data.
- `azure_log_shared_key`: Primary Key of the Log Analytics workspace to log event data.
### Step 5: Test AISDefenseModel
Load the necessary data and use AIShield provided attack data for testing the defense model.
```python
attack_data = load_data(attack_data_list)
model.predict(attack_data)
```
Once AIShield provided Threat Informed Endpoint Defense (EDR) app sending logs to Microsoft sentinel you will be able to see logs using parser name or table name\:L
AIShield or AIShield\_CL

If you have any questions or need any help related to this integration. Please get in touch with aishield.contact\@bosch.com
[title] Untitled
[path] API Documentation/AISpectra/
[title] Tabular Classification
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/Analyze your models/Tabular/
The below input parameters are for different attack types. To start working with the APIs view the [Tabular Classification](docId\:v08LzX7yC3id62W3z63yg).
## File upload format
- **Data**: Data should be in a CSV file with a header as all the features (Columns) name and the last column as the target variable.
Downloa sample data
- **Minmax**: Data should be in a CSV file with a header as all the feature (Columns) names and the last column as the target variable. The first row of the CSV file should contain the minimum value for each column (feature), and the second row should contain the max value.
Downloa sample minmax
- **Model**: The model should be saved in either .pkl, .h5 or TensorFlow format. Full architecture is needed when loading the model to the platofrm for assessment either in encrypted or unencrypted. This can be ignored when model is hosted as an API.
Downloa sample model
:::hint{type="warning"}
All files uploaded should be in zipped format. The above files are sample data.
:::
## Common parameters
The below table parameters are common for all attact types.
:::hint{type="warning"}
To see the additional parameter specific to attact type refer to the below sections.
:::
| Parameter | Data type | Descrption | Remark |
| ------------------------------ | --------- | --------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- | -------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| model\_id | String | Model\_id received during model registration. We need to provide this model\_id in query parameter in URL. | you have to do model registration only once for a model and you can perform many analysis. This will help you to track how many api call has been made, how many has successed. |
| **Request Body (Json format)** | | | |
| normalize\_data | String | Model trained on Normalized data. | if model is trained on normalized data, then set this parameter as "yes" else "no". |
| input\_dimensions | String | length of dataset \* features | the parameter should be string in the format "(height, weight, channel)" For example 100,18 |
| number\_of\_classes | String | Number of prediction classes. | the parameter should be string. Example : Banking Marketing
Campaign classification dataset 2 (Range >0 & \<=200) |
| model\_api\_details | String | If use\_model\_api is Yes, then provide API details of hosted model as
encrypted JSON string is mandatory | provide this only if use\_model\_api is "yes". |
| use\_model\_api | String | If use\_model\_api is Yes, then provide API details of hosted model as encrypted JSON
string is mandatory | when this parameter is yes, you don't have to upload model as zip. You can pass api url along with other verification credential in json file. |
| model\_framework | String | Original model is built with scikit-learn framework. (Option:\[scikit learn]) | curretly supported framework are: tensorflow, scikit-learn, keras |
| defense\_bestonly | String | Highly optimized defense model will be returned. | when selected **"yes"**, it will train N number of model and select best model. Ofcourse this will take longer time. If **"no"**, then once defense model accuracy reached above 95% It will stop |
| encryption\_strategy | Int | Choose a encryption strategy for you model. if model is uploaded directly as a zip pick 0, 1 if model is encryted as .pyc and uploaded as a zip. Ignore if use\_model\_api is Yes | select 0: pass tensorflow model as it is, select 1: pass encrypted model. It could be .pyc file |
| is\_category\_columns | String | If any categorical column presents in dataset provide 'yes' otherwise
'no' | |
| categorical\_columns\_info | String | If is\_category\_columns is yes, then provide the column names of the categorical. (Provide these columns name as comma separated) | |
:::ExpandableHeading
## Extraction parameters
| Parameter | Data type | Descrption | Remark |
| --------------------------------- | --------- | ----------------------------------------------------------------------------- | ------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| **Request Body (Json format)** | | | |
| attack\_type | String | You can select the attack type either Blackbox or Greybox. | **Blackbox**: for performing model analysis, no information about model or data will be used. **Greybox**: information about data will be leverage for creation of attack data **Note: **only 2-5 % of data is needed |
| number\_of\_attack\_queries
| String | Number of attack sample to use for analysis. | Generally heigher the number of attack queries , better would be the analysis. Accepted range: (0-400000) |
| vulnerability\_threshold | String | Stolen model accuracy threshold at which defense model should get generated. | Parameter value Range: (0.0 - 1.0). |
:::
::::ExpandableHeading
## Evasion parameters
:::hint{type="info"}
**Note**: use [Tabular Classification](./#common-parameters) only, no extra parameters is needed.
:::
::::
:::ExpandableHeading
## Experimentation with values
To improve the accuracy, you can experiment with the following values for your attack input parameters. In our example we have used an BFSI dataset in our model and the below table reflects the parameters suitable for it. For more information, please refer to the reference implementation.
| Task Pair/Analysis Type | Model under analysis | Type of Attack Strategy | No of queries | Outcome |
| ----------------------- | -------------------- | ------------------------ | -------------- | ------------------------------------- |
| TC - MEA | BFSI | Blackbox | 10000 | Stolen model accuracy between 75%-85% |
| TC - MEA | BFSI | Greybox | 20000 | Stolen model accuracy between 80%-90% |
| TC - EVA | BFSI | N/A | N/A | Evasion Report |
:::
:::hint{type="info"}
To access all sample artifacts, please visit [Artifacts](docId\:iJNEOCXoStabvvrsq11fa).
- For specific artifact details, refer
- Vulnerability Report : [Vulnerability Report](docId\:hL0uT2MWlCBkt8F97fr-W)
- Sample Attacks : [Sample Attacks](docId:4G1mjM5lQjfm8t5WBVwpr)
- Defense Report: [Defense Report](docId\:VtzlTtpja2VSF2j0STLSQ)
- Defense Model: [Defense Model](docId\:xSbxmZXW4vv14-8NmBF8M)
:::
:::hint{type="info"}
**Note**: For Tabular classification, supported attack types are - Extraction
:::
[title] Artifacts
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/
AIShield provides four types of artifacts regarding your model: vulnerability reports, defense reports, attack samples, and defense models.
AIShield provides four types of artifacts for model analysis and protection:
1. [Vulnerability Report](docId\:hL0uT2MWlCBkt8F97fr-W): Provides information about critical vulnerabilities related to model attacks, including severity, associated risks, and mitigation measures.
2. [Sample Attacks](docId:4G1mjM5lQjfm8t5WBVwpr): A set of randomly selected attack samples used during testing to evaluate the model's performance.
3. [Defense Report](docId\:VtzlTtpja2VSF2j0STLSQ): Offers an overview of a defense model's accuracy and efficacy in detecting attacks on the original model.
4. [Defense Model](docId\:xSbxmZXW4vv14-8NmBF8M): Includes files for the defense model, such as Defense\_model.h5, Defense\_model.onnx, Predict.py, and ReadMe.txt.
For reference, sample reports and artifacts are available for review.
[title] Defense deployment
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/Threat Informed Defense/
This guide will help you seamlessly deploy and utilize the defense model to safeguard your valuable assets against adversarial threats.
### **Prerequisites**
Before proceeding, ensure the following prerequisites are met:
- You have completed the [Analyze your models](docId:5yPzn_yVV16Eojib5oT0U) to identify vulnerabilities.
- You have received the **defense model artifact,** which includes the following essential files:
- **app.py **: The core application logic for the defense model.
- **app\_log.py **: A logging module for effective monitoring.
- **config.yaml **: A configuration file for customizing the defense model settings.
- **defense\_model.h5 **: The defense model itself in HDF5 format.
- **defense\_model.onnx **: An alternative format of the defense model in ONNX.
- **deployment.yaml **: If you plan to deploy on Kubernetes, this configuration file is included.
- **docker-compose.yaml **: For Docker container deployment, this file is provided.
- **Dockerfile **: Required for building the Docker image.
- **predict.py **: A script to make predictions using the defense model.
- **Readme.txt **: Comprehensive documentation with instructions.
- **requirements.txt **: A list of Python dependencies required for the defense model.
### Deployment Options
The AIShield Defense Model is designed for flexibility and can be deployed in two ways:
1. **Docker Container Deployment**:
- Ideal for quick and isolated deployments.
- Requires Docker to be installed on your system.
- Utilizes the provided Dockerfile for image creation.
- Execute the Docker container using the appropriate commands.
2. **Kubernetes Deployment**:
- Suitable for scalable and orchestrated deployments.
- Assumes you have access to a Kubernetes cluster.
- Deploy and manage the defense model on your Kubernetes cluster.
### Getting Started
To begin using the defense model and enhancing the security of your AI/ML models, follow these steps based on your chosen deployment option:
### **For Docker Container Deployment**:
**Step1**: Ensure Docker is installed on your system.
**Step2**: Build the Docker image using the provided Dockerfile.
```curl
sudo docker build --progress=plain -t aishield-ic-mea-defense .
```
**Step3**: Run the Docker container to start using the defense model.
```curl
sudo docker run aishield-ic-mea-defense
```
Feel free to **customize the "aishield-ic-mea-defense" Docker container name as needed**, ensuring it aligns with your preferences and environment.
After successfully running defense as docker container, access endpoint as follows :
**\ Sanity Check**
```python
import requests
r = requests.get('http://127.0.0.1:5016//predict') ## change host and port for deployment on non local device
r.json()
```
you can expect response as follow
> \{'message': 'Model Sanity check successful!'}
**\ predict**
```python
import requests
x = data ## this the data you want to query to model
payload = {"data": x}
## change host and port for deployment on non local device
response = requests.post('http://127.0. 0.1:5016//predict', json=payload,
headers={"Content-Type": "application/json"},)
print(response.json())
```
expected response
> \{'prediction': ['low suspicious attack', 'high suspicious attack', 'high suspicious attack']}
### For Kubernetes Deployment:
1. Ensure you have access to a Kubernetes cluster.
2. Deploy the defense model on Kubernetes by applying the
**Apply the deployment to your Kubernetes cluster:**
:::CodeblockTabs
Kubectl
```curl
kubectl apply -f deployment.yaml
```
:::
This will deploy the AIShield containerized defense as specified in the YAML file to your Kubernetes cluster.
### Conclusion
With the AIShield Defense Model at your disposal, you are equipped to fortify your AI/ML models against potential threats and attacks. This tool will significantly enhance the security of your valuable assets.
For any questions or assistance, please feel free to reach out to our support team at [AIShield.Contact@bosch.com]()
[title] WhyLabs
[path] Integration Partners/MLOps/
WhyLabs is a platform that helps organizations manage and monitor their machine learning models. By automating data pipeline management and providing real-time monitoring and insights, WhyLabs makes it easier for teams to build, test, and deploy models with confidence. With WhyLabs, organizations can streamline their MLOps pipeline and ensure the security and compliance of their models.
**Follow the steps below to integrate AI Shield with Whylabs:**
:::hint{type="info"}
To learn more, see the reference implementation on GitHub for WhyLabs.
:::
### Requirements
To integrate AI Shield with WhyLabs, you'll need the following:
1. A Conda or Python environment
2. Docker (install from [https://docs.docker.com/desktop/windows/install/](https://docs.docker.com/desktop/windows/install/))
### Steps
Follow these steps to integrate AI Shield with WhyLabs:
1. Clone the Iris code from GitHub.
2. Sign up for the WhyLabs website and note the API key. Edit the .env file with the respective API key and organization ID. The API key is valid for one year.
3. Create a Conda environment using `conda env create -f environment.yml`. This will create the environment and install all the packages listed in the environment.yml file. However, you can also create the environment manually using `conda create -n whylabs python=3.7.13 numpy==1.21.5` and install the necessary packages based on requirements.
4. Build the Dockerfile without VPN and proxy off using `docker build -f Dockerfile --build-arg PYTHON_VERSION=3.7 -t whylabs-flask.` This will create an image/container named whylabs-flask, which has all the packages present in the requirement.txt file. You need to do this build every time you want to create the container.
5. Run the Docker container using `docker run --rm -p 5000:5000 whylabs-flask`.
6. Access the WhyLogs by hitting the API endpoint. You can do this through Swagger UI or a Python post request.
7. You can see the logs in "[https://hub.whylabsapp.com/models](https://hub.whylabsapp.com/models)".
8. First, create a model ID on the WhyLabs website, and then enter that ID in the .env file.
9. Make changes to `views.py` by adding the product defense prenet and logging changes to WhyLabs (about MNIST).
10. Baseline for MNIST: 0 to 9: original model output. If the prediction is non-integer, generate an alert in WhyLabs.
[title] Integration Partners
[path] /
[title] MLFlow
[path] Integration Partners/MLOps/
MLflow is an open source platform for managing the end-to-end machine learning lifecycl. see MLflow docs to learn more.
This document provides an overview of the use of the AIShield API with MLflow and logs artifact received from the API. In the following sections, you can learn how to install packages, load datasets, train the model, prepare an artifact for an AIShield API call, and perform the AIShield API call.
### Installation
To install packages, run the following command:
`pip install -r requirements.txt`
### Load Dataset
Download the MNIST dataset from TensorFlow, preprocess it, and split the data set into train, test, and validation in a ratio of 54k:6k:10K. Visualize sample data.
### Model Training
Create model architecture and train it on training data. After training, validate on the validation dataset. Model accuracy is expected to be around 99.3%.
### Prepare Artifact for the AIShield API Call
Save a sample of data, its label, and model as a .zip file. The .zip file is needed during the AIShield API call.
### AIShield API Call
Requirements: Get AIShield API endpoint, x-API-key, and ord\_id from the AIShield team.
1. Call the model registration API. This API will return a unique model id and path to upload data, model, and label. It will also return a sample request payload for a model analysis API.
2. Upload the data, model, and label to the given URL.
3. After successful upload, call the model analysis API and pass the payload. In the response, you will get a unique job\_id and monitor link. The monitor link can be used to track the progress of the triggered job.
4. Monitor the progress of the job ID using the get API, and after successful completion, download the artifacts and log them to MLflow as an artifact. The artifacts will contain vulnerability and defense reports, attack samples, defense artifact
5. Load the AIShield provided defense model and pass a sample of original data and attack data to get a prediction from the defense model.
6. To integrate with SIEM solutions such as Microsoft Sentinel and Splunk, please follow the instructions below:
1. For the Microsoft Sentinel connector, provide azure\_log\_customer\_id and azure\_log\_shared\_key while creating the AISDefenseModel object.
2. For Splunk connector, provide splunk\_url and splunk authorization while creating the AISDefenseModel object.
:::hint{type="info"}
To learn more see the reference implementatoin notebook for FLflow
:::
[title] Model Security
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/Dashboard/
The Model Security page provides a comprehensive overview of the security aspects related to your models.
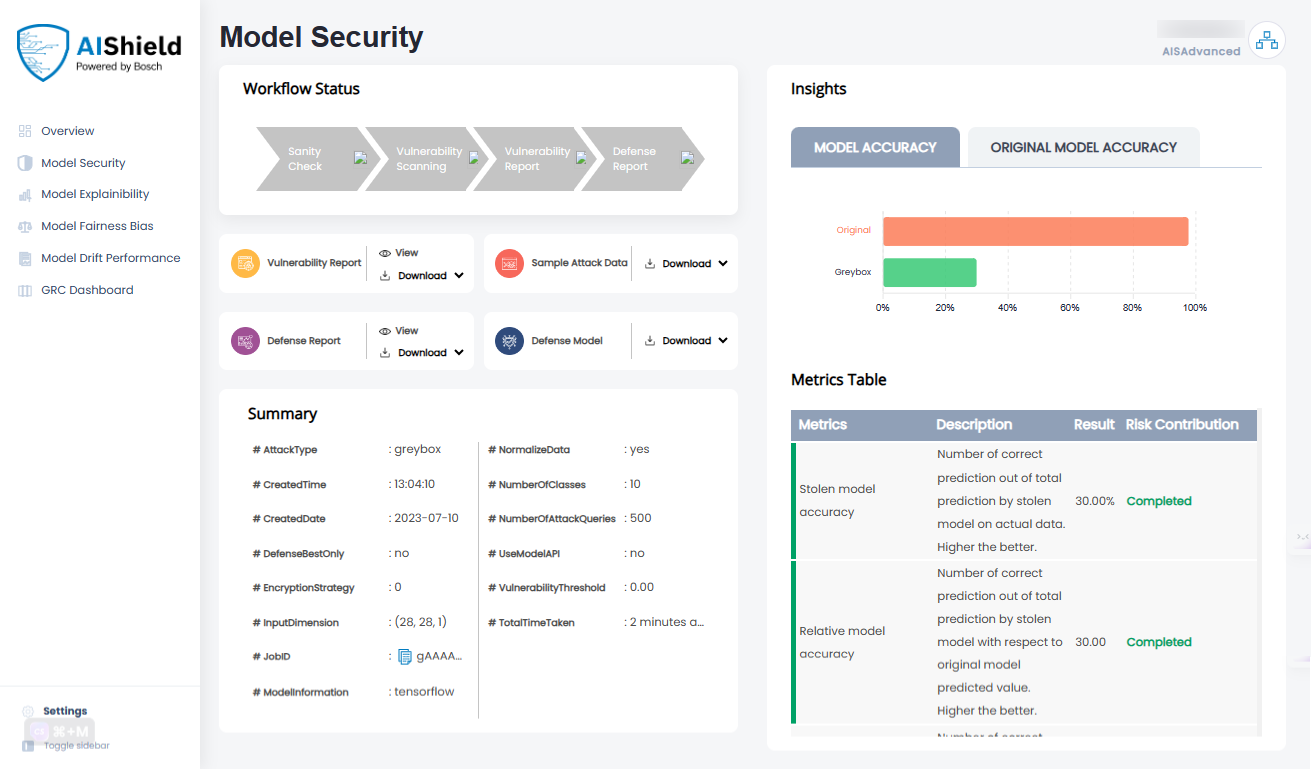
### Job Details
The Job Details page provides comprehensive information and insights about a specific job in the model security workflow. It includes the workflow status, detailed reports, job summary, accuracy insights, and metrics table.
### Workflow Status
The Workflow Status section visually represents the latest status of the job using different colors to indicate its progress or completion.
### Report
The Report section offers downloadable files containing comprehensive information and data related to the job. These files are available in various formats for easy access and analysis.
### Summary
The Summary section provides essential metadata information about the job, giving users a quick overview of its key attributes and characteristics.
### Insights
The Insights section offers valuable accuracy insights for the original model and the attack type (blackbox or greybox). It includes the accuracy percentage and classifies the original model accuracy level as low, medium, or high.
### Metrics Table
The Metrics Table presents a detailed breakdown of various metrics associated with the job. It includes a description of each metric, its corresponding value, and the Risk Contribution based on the task pair to which the job belongs.
By exploring the Job Details page, users can access comprehensive information, reports, and insights related to a specific job in the model security workflow. This allows them to track the progress of the job, analyze its results, and make informed decisions based on the accuracy insights and metrics provided.
[title] Troubleshooting
[path] FAQ & Troubleshooting/
**Troubleshooting Guide: Common API Errors and Solutions**
This troubleshooting guide provides solutions to common errors encountered while using the AIShield API. If you are facing any of the following issues, follow the steps mentioned below to resolve them.
1. **Error: "Org-Id missing"**
- Reason: The API call requires an Org-Id parameter in the header, which uniquely identifies each User or Organization subscribed to the AIShield Product.
- Solution: Make sure to include the Org-Id parameter in the header of your API request. If you haven't subscribed to AIShield Product yet, please do so to obtain a valid Org-Id.
2. **Error: "Subscription plan has expired. Please contact AIShield support"**
- Reason: The subscription plan associated with the provided Org-Id has expired, and you can no longer access the API services.
- Solution: Contact the AIShield Support Team to renew your subscription plan and regain access to the API services.
3. **Error: "Please check, except required parameters no other parameters should be provided for performing model registration"**
- Reason: When performing model registration, you should only include the accepted parameters in the payload. Including any additional parameters will result in this error.
- Solution: Review the documentation to ensure that you are sending only the required parameters during model registration. Remove any extra parameters from the payload to resolve the issue.
4. **Error: "Invalid Org-ID value specified"**
- Reason: The Org-Id value provided in the API call is incorrect or invalid.
- Solution: Double-check the Org-Id value provided to you by the AIShield team. If you believe the Org-Id is correct, but the error persists, contact the AIShield Support Team for assistance.
5. **Error: "Model file missing" or "Data file missing"**
- Reason: When performing model registration, you must upload both the Model and Data files using the provided URLs. Not providing these files will result in this error when attempting to perform model analysis API calls.
- Solution: Ensure that you have uploaded both the Model and Data files to the specified URLs before making model analysis API calls. Uploading the required files will resolve the issues.
6. **Error: "Forbidden"**
- Reason: The API call requires an x-api-key parameter in the header for authentication. The x-api-key parameter is obtained using the get\_aws\_api\_key API.
- Solution: Include the x-api-key parameter in the header of your API request to authenticate your access. If you haven't obtained the x-api-key yet, use the get\_aws\_api\_key API to acquire it.
If you encounter any other issues or need further assistance, please don't hesitate to reach out to the AIShield Support Team. They will be glad to assist you with any API-related problems.
[title] Text Classification
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/Analyze your models/Text/
The below input parameters are for different attack types. To start working with the APIs, see [Text Classification](docId\:EOqluV3UxbC2_KALISdBO).
:::hint{type="warning"}
Text classification is an early access with limited functionality. It is not available in AIShield pypi package. For early access, kindly contact AIShield.Contact\@bosch.com
:::
## File upload format
- **Data**: The processed data, ready to be passed to the model for prediction, should be saved in a folder.
Download sample data
- **Model**: The model should be saved in either .h5 or TensorFlow format with full architecture along with token in .pkl format. Also there need to be a base\_model.py file which should load model and token and confire it to give prediction. All Three file base\_model.py, .h5 saved model and .pkl saved token should be zipped in a folder and uploaded.
Download sample model
## Common parameters
The below table parameters are common for Extraction Attack type.
| Parameter | Data type | Description | Remark |
| ------------------------------ | --------- | ------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------ | ------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| model\_Id | String | Model\_id received during model registration.
We need to provide this model ID in query parameter in URL. | You have to do model registration only once for a model to perform model analysis. This will help you track the no of api call made, and it's success metric. |
| **Request Body (Json format)** | | | |
| model\_api\_details | String | Use model API to train your model instead of uploading the model as a zip file.
Yes | provide this only if use\_model\_api is "yes". |
| Attack\_type | String | You can select the attack type either Blackbox or Greybox. | **Blackbox**: for performing model analysis, no information about model or data will be used. **Greybox**: information about data will be leverage for creation of attack data **Note: **only 2-5 % of data is needed |
| normalize\_data | String | Model trained on Normalized data. | if model is trained on normalized data, then set this parameter as "yes" else "no". |
| input\_dimensions | String | Provide input dimension of the text (100) | the parameter should be string in the format. For example 100. |
| number\_of\_attack\_queries | String | Number of attack queries that model will be
subjected to. e.g. 20000 | generally Heigher the number of attack queries, better would be the analysis. And it would take more time to process. (Range: >0 & \<=400000) |
| model\_framework | String | Original model is built with tensorflow framework. | curretly supported framework are: tensorflow, scikit-learn, keras. (Option:\[tensorflow]) |
| vulnerability\_threshold | String | Number of attack queries that model will be
subjected to. e.g, 0.0 - 1 | Threshold percent of stolen model accuracy
at which defense model should be generated
(Range : 0.0 - 1) |
| defense\_best\_only | String | Choose to train your model until it achieves the best results or above 95% accuracy. | when selected **"yes"**, it will train N number of model and select best model. Ofcourse this will take longer time. If **"no"**, then once defense model accuracy reached above 95% It will stop |
| encryption\_strategy | Int | Choose a encryption strategy for you model. if model is uploaded directly as a
zip pick 0, 1 if model is encryted as .pyc and
uploaded as a zip. Ignore if use\_model\_api is
Yes | select 0: pass tensorflow model as it is, select 1: pass encrypted model. It could be .pyc file |
:::hint{type="info"}
To access all sample artifacts, please visit [Artifacts](docId\:iJNEOCXoStabvvrsq11fa).
- For specific artifact details, refer
- Vulnerability Report : [Vulnerability Report](docId\:hL0uT2MWlCBkt8F97fr-W)
- Sample Attacks : [Sample Attacks](docId:4G1mjM5lQjfm8t5WBVwpr)
- Defense Report: [Defense Report](docId\:VtzlTtpja2VSF2j0STLSQ)
- Defense Model: [Defense Model](docId\:xSbxmZXW4vv14-8NmBF8M)
:::
:::hint{type="info"}
**Note**: For Text classification, supported attack types are - Extraction
:::
[title] Job Status Details
[path] API Documentation/AISpectra/
`Get /api/ais/v1.5/job_status_detailed`
:::ApiMethodV2{data="{"tab":"examples","url":"https://api.aws.boschaishield.com/prod/api/ais/v1.5/job_status_detailed","name":"Job status details","method":"GET","request":{"pathParameters":[{"name":"job_id","kind":"required","type":"string","description":"Enter uniquely created job_id received during model analysis.","children":[]}],"queryParameters":[],"headerParameters":[{"kind":"required","name":"x-api-key","type":"string","children":[],"description":"Enter your API key"},{"kind":"required","name":"Org-id","type":"string","children":[],"description":"Enter your organization key"}],"bodyDataParameters":[],"formDataParameters":[]},"results":{"languages":[{"id":"KC2y4qJqRPaU4tYK2ivhe","code":"// 200 OK: Returns a JSON object containing the job details for every stage of vulnerability analysis & defense generation.\n\n","language":"200","customLabel":""},{"id":"WtBayiHuwETawq1mKFiTV","code":"// 400 Bad request Error: Returns an error message if the application cannot or will not process the request due to something that is perceived to be a client error (for example, malformed request syntax, invalid request message framing, etc.)","language":"400","customLabel":""},{"id":"Ka-pbMspJxU4S2kfhDbRg","language":"403","code":"// 403 Forbidden: Returns an error message if access to the target resource has been denied. (For example- if x-api-key value is incorrect or not given)","customLabel":""},{"id":"d8lH0HKIDeIi7ETZjI3_h","language":"412","code":"// 412 Precondition failed: Returns an error message if access to the target resource has been denied. (For example- if any of the parameter value is incorrect or license has expired)","customLabel":""},{"id":"q44sE4FMKWnu5Gm0JXliK","language":"429","code":"// 429 Too Many Requests: Returns an error message if the user has sent too many requests(example 15-20 requests in 1 seconds) in a given amount of time.","customLabel":""}],"selectedLanguageId":"q44sE4FMKWnu5Gm0JXliK"},"examples":{"languages":[{"id":"QIKk1KG_nGzgceRySfIT0","language":"python","code":"import requests\n\njobID = \" << Enter Job ID >>\"\n\nurl = \"https://api.aws.boschaishield.com/prod/api/ais/v1.5/job_status_detailed?job_id=\"+jobID+\"\"\n\npayload = {}\nheaders = {\n 'x-api-key': '########################################',\n 'Org-Id': '####################################################################################################'\n}\n\nresponse = requests.request(\"GET\", url, headers=headers, data=payload)\n\nprint(response.text)","customLabel":""},{"id":"FMFlJeOGjrKhA6nGbcdR9","language":"curl","code":"jobID=\"<< Enter Job ID>>\";\ncurl --location --request GET 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/job_status_detailed?job_id='${jobID}'' \\\n--header 'Accept: application/json' \\\n--header 'x-api-key: ########################################' \\\n--header 'Org-Id: ####################################################################################################'","customLabel":""},{"id":"OSL7834tXCdl3ioKKfaQF","language":"nodejs","code":"var request = require('request');\n\njobID = '<< Enter Job ID >>'\n\nvar options = {\n 'method': 'GET',\n 'url': 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/job_status_detailed?job_id='+jobID+'',\n 'headers': {\n 'x-api-key': '########################################',\n 'Org-Id': '####################################################################################################'\n }\n};\nrequest(options, function (error, response) {\n if (error) throw new Error(error);\n console.log(response.body);\n});\n","customLabel":""},{"id":"HBk4tnO1UYud_8IJN06Ii","language":"javascript","code":"var myHeaders = new Headers();\nmyHeaders.append(\"x-api-key\", \"########################################\");\nmyHeaders.append(\"Org-Id\", \"####################################################################################################\");\n\nvar requestOptions = {\n method: 'GET',\n headers: myHeaders,\n redirect: 'follow'\n};\n\njobID=\"<>\"\n\nfetch(\"https://api.aws.boschaishield.com/prod/api/ais/v1.5/job_status_detailed?job_id=\"+ jobID+\"\", requestOptions)\n .then(response => response.text())\n .then(result => console.log(result))\n .catch(error => console.log('error', error));","customLabel":""}],"selectedLanguageId":"HBk4tnO1UYud_8IJN06Ii"},"description":"Job status detail api help you track progress of your active job id.","currentNewParameter":{"label":"Path Parameter","value":"pathParameters"}}"}
:::
:::hint{type="info"}
`job_id` - Enter the job id you have recevied during the model analysis to get the progress of the given job id.
:::
:::hint{type="info"}
For using Nodejs sample code, install npm package request
Given ample code for python is tested for Python version 3.7
Given Sample code for nodejs and javascript is tested for Node V20LTS
:::
[title] Job Metadata
[path] API Documentation/AISpectra/
`Get api/ais/v1.5/job_detail`
:::ApiMethodV2{data="{"tab":"examples","url":"https://api.aws.boschaishield.com/prod/api/ais/v1.5/job_detail","name":"Job metadata","method":"GET","request":{"pathParameters":[{"name":"job_id","kind":"required","type":"string","description":"Enter uniquely created job_id received during model analysis.","children":[]}],"queryParameters":[],"headerParameters":[{"kind":"required","name":"x-api-key","type":"string","children":[],"description":"Enter your API key"},{"kind":"required","name":"Org-Id","type":"string","children":[],"description":"Enter your organization key"}],"bodyDataParameters":[],"formDataParameters":[]},"results":{"languages":[{"id":"KC2y4qJqRPaU4tYK2ivhe","code":"// 200 OK: Returns a JSON object containing the job details for every stage of vulnerability analysis & defense generation.","language":"200","customLabel":""},{"id":"WtBayiHuwETawq1mKFiTV","code":"// 400 Bad request Error: Returns an error message if the application cannot or will not process the request due to something that is perceived to be a client error (for example, malformed request syntax, invalid request message framing, etc.)","language":"400","customLabel":""},{"id":"y3j22YKtOjDz_rUvvP0Se","language":"403","code":"// 403 Forbidden: Returns an error message if access to the target resource has been denied. (For example- if x-api-key value is incorrect or not given)","customLabel":""},{"id":"LzcZTbzdXv2tI7qFFrgk4","language":"412","code":"// 412 Precondition failed: Returns an error message if access to the target resource has been denied. (For example- if any of the parameter value is incorrect or license has expired)","customLabel":""},{"id":"AE4qrPxXn2sc-4WsmvZ4l","language":"429","code":"// 429 Too Many Requests: Returns an error message if the user has sent too many requests(example 15-20 requests in 1 seconds) in a given amount of time.","customLabel":""}],"selectedLanguageId":"AE4qrPxXn2sc-4WsmvZ4l"},"examples":{"languages":[{"id":"_KBSEbK47RC8ESSWkpHSw","language":"python","code":"import requests\n\njobID = \"<< Enter Job ID >>\"\nurl = \"https://api.aws.boschaishield.com/prod/api/ais/v1.5/job_detail?job_id=\"+jobID+\"\"\n\npayload = {}\nheaders = {\n 'x-api-key': '########################################',\n 'Org-Id': '####################################################################################################'\n}\n\nresponse = requests.request(\"GET\", url, headers=headers, data=payload)\n\nprint(response.text)","customLabel":""},{"id":"taXcr4Mbz18AKGldJE0ce","language":"curl","code":"jobID=\"<< Enter Job ID>>\"\ncurl --location --request GET 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/job_detail?job_id='${jobID}'' \\\n--header 'Accept: application/json' \\\n--header 'x-api-key: ########################################' \\\n--header 'Org-Id: ####################################################################################################'\n","customLabel":""},{"id":"ty5lakNdu2dRINQjy2Zjx","language":"nodejs","code":"var request = require('request');\n\njobID = '<< Enter Job ID >>'\nvar options = {\n 'method': 'GET',\n 'url': 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/job_detail?job_id='+jobID+'',\n 'headers': {\n 'x-api-key': '########################################',\n 'Org-Id': '####################################################################################################'\n }\n};\nrequest(options, function (error, response) {\n if (error) throw new Error(error);\n console.log(response.body);\n});\n","customLabel":""},{"id":"-IrX_lvPAol0wYbdGrpqf","language":"javascript","code":"var myHeaders = new Headers();\nmyHeaders.append(\"x-api-key\", \"########################################\");\nmyHeaders.append(\"Org-Id\", \"####################################################################################################\");\n\nvar requestOptions = {\n method: 'GET',\n headers: myHeaders,\n redirect: 'follow'\n};\n\njobID=\"<>\"\n\nfetch(\"https://api.aws.boschaishield.com/prod/api/ais/v1.5/job_detail?job_id=\"+ jobID+\"\", requestOptions)\n .then(response => response.text())\n .then(result => console.log(result))\n .catch(error => console.log('error', error));","customLabel":""}],"selectedLanguageId":"_KBSEbK47RC8ESSWkpHSw"},"description":"The Job Status API allows you to fetch metadata for a given job ID.","currentNewParameter":{"label":"Path Parameter","value":"pathParameters"}}"}
:::
:::hint{type="info"}
`job_id` To get the Job meta data, enter the job id you recevied during model analysis.
For example, response for image classification job meta data contains e.g., attack type, encryption strategy, Input dimensions, model information, data normalization, number of attack queries, vulnerability threshold, etc.
:::
:::hint{type="info"}
For using Nodejs sample code, install npm package request
Given ample code for python is tested for Python version 3.7
Given Sample code for nodejs and javascript is tested for Node V20LTS
:::
[title] Tabular Classification
[path] API Documentation/AISpectra/Automated RedTeaming for AI/ML/ Model Analysis/Tabular/
The below parameters are for various Tabular classification attack types. To know more about the different attack input parameters see [Tabular Classification](docId\:mVtLcTNKaSHPx9MzjvB62).
:::hint{type="info"}
The values presented below are examples taken from the model used in the reference implementation. It is important to customize these values to achieve the best performance for your particular model.
:::
:::CodeblockTabs
Extraction
```json
{
"attack_type": "blackbox",
"categorical_columns_info": "job,marital,education,default,housing,loan,contact,poutcome",
"defense_bestonly": "no",
"encryption_strategy": "0",
"input_dimensions": "100,18",
"is_category_columns": "yes",
"model_api_details": "na",
"model_framework": "scikit-learn",
"normalize_data": "yes",
"number_of_attack_queries": "10000",
"number_of_classes": "2",
"use_model_api": "no",
"vulnerability_threshold": "0.00"
}
```
Evasion
```json
{
"categorical_columns_info": "job,marital,education,default,housing,loan,contact,poutcome",
"defense_bestonly": "no",
"encryption_strategy": "1",
"input_dimensions": "41188,18",
"is_category_columns": "yes",
"model_api_details": "na",
"model_framework": "scikit-learn",
"normalize_data": "yes",
"number_of_classes": "2",
"use_model_api": "no"
}
```
:::
:::ApiMethodV2{data="{"tab":"examples","url":"https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse","name":"Model anaylsis","method":"POST","request":{"pathParameters":[{"name":"model id","kind":"required","type":"string","description":"Enter you model id","children":[]}],"queryParameters":[],"headerParameters":[{"kind":"required","name":"Org_id","type":"string","children":[],"description":"Enter your organization id"},{"kind":"required","name":"x-api-key","type":"string","children":[],"description":"Enter your API key"}],"bodyDataParameters":[],"formDataParameters":[]},"results":{"languages":[{"id":"DL4HDcclTH6dUtOu-opbD","code":"// 200 OK: Returns a JSON object containing unique model ID and urls to upload required files.","language":"200","customLabel":""},{"id":"FHRZSmfHKporaKUQs5nWK","language":"401","code":"// 401 Unauthorized: Returns an error message if the provided API key or Org-ID is invalid or expired.","customLabel":""},{"id":"IPX3tlCeTWToOzeMY0zQI","language":"400","code":"// 400 Bad request Error: Returns an error message if the application cannot or will not process the request due to something that is perceived to be a client error (for example, malformed request syntax, invalid request message framing, etc.)","customLabel":""},{"id":"X-4riS1xpTVjjNQhgoYxk","language":"412","code":"// 412 precondition failed: Returns an error message if access to the target resource has been denied. (For example- if any of the parameter value is incorrect or license has expired)","customLabel":""}],"selectedLanguageId":"X-4riS1xpTVjjNQhgoYxk"},"examples":{"languages":[{"id":"OQ-j7-jC68HXVP4dP5SLI","language":"python","code":"import requests\n\nmodelID=\"<< Enter Model ID >>\"\nurl = \"https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/\"+modelID+\"\"\n\n# please select proper payload for your usecase for extraction, evasion or poisoning.\npayload={\n # <>\n}\nheaders = {\n 'Accept': 'application/json',\n 'x-api-key': '########################################',\n 'Org-Id': '####################################################################################################'\n}\n\nresponse = requests.request(\"POST\", url, headers=headers, data=payload)\n\nprint(response.text)","customLabel":""},{"id":"2J4Hww7YlSzM8iA5-Oe4P","language":"curl","code":"modelID=\"<< Enter Model ID >>\"\ncurl --location 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/${modelID}' \\\n--header 'x-api-key: ########################################' \\\n--header 'Org-Id: ####################################################################################################' \\\n--header 'Content-Type: application/json' \\\n--data '{\n <>\n}'","customLabel":""},{"id":"kLRzKT-ZqhTfS8EOm28jy","language":"nodejs","code":"var request = require('request');\n\nmodelID = '<>'\nvar options = {\n 'method': 'POST',\n 'url': 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/'+modelID+'',\n 'headers': {\n 'x-api-key': '########################################',\n 'Org-Id': '####################################################################################################',\n 'Content-Type': 'application/json'\n },\n body: JSON.stringify({\n // <>\n })\n\n};\nrequest(options, function (error, response) {\n if (error) throw new Error(error);\n console.log(response.body);\n});\n","customLabel":""},{"id":"xEhJjL_EhgrpaSijzXvYJ","language":"javascript","code":"var myHeaders = new Headers();\nmyHeaders.append(\"x-api-key\", \"########################################\");\nmyHeaders.append(\"Org-Id\", \"####################################################################################################\");\nmyHeaders.append(\"Content-Type\", \"application/json\");\n\nvar raw = JSON.stringify({\n // << Enter Payload Details based on Task pair >>\n});\n\nvar modelID = \"<< Enter Model ID >>\"\n\nvar requestOptions = {\n method: 'POST',\n headers: myHeaders,\n body: raw,\n redirect: 'follow'\n};\n\nfetch(\"https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/\"+modelID+\"\", requestOptions)\n .then(response => response.text())\n .then(result => console.log(result))\n .catch(error => console.log('error', error));","customLabel":""}],"selectedLanguageId":"xEhJjL_EhgrpaSijzXvYJ"},"description":"","currentNewParameter":{"label":"Path Parameter","value":"pathParameters"}}"}
:::
:::hint{type="info"}
Note: In the response, copy job\_id. This value is required to trigger the GET APIs. See [\ Job Metadata](docId\:S-mZ7r0HNzicDQy6Q-6Hq).
The "job\_id" is used to retrieve model analysis metadata and check the processing status of the request. It is also used for generating reports for the analyzed model. Copy the dashboard link from the response and open it in a new tab. This allows users to monitor the job progress and download reports.
:::
:::hint{type="info"}
For using Nodejs sample code, install npm package request
Given ample code for python is tested for Python version 3.7
Given Sample code for nodejs and javascript is tested for Node V20LTS
:::
[title] Amazon Security Lake
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/Threat Informed Defense/Configuration of Connector/
# 1. Introduction
Amazon Security Lake is a fully-managed security data lake service that helps you analyze security data, so you can get a more complete understanding of your security posture across the entire organization.
AIShield is an AI-security product designed to protect AI-powered devices in the face of emerging security threats such as Model Extraction, Evasion, Data Poisoning, and Model Inference attacks. AIShield provides automated hacker-level vulnerability analysis and endpoint protection to harden the systems against emerging AI-security threats. AIShield provided Threat Informed Endpoint Defense (EDR) that integrates with Amazon Security Lake as custom source to deliver enhanced real-time monitoring capabilities to security teams for their AI assets, giving them insights into AI security incidents.
AIShield Threat Informed Endpoint Defense (EDR) supports OCSF formatted security finding events storing in S3, as a custom source of Amazon Security Lake.
# 2. Configure Amazon Security Lake
**Pre-requisite for AIShield**
Users will have to leverage AIShield product to scan their AI model for vulnerabilities and generate Threat Informed Endpoint Defense (EDR) capable of integrating with Security Lake. To complete this step, please get in touch with AIShield.Contact\@bosch.com
**Pre-requisite for Amazon Security Lake.**
You must have Amazon Security Lake enabled.
## 2.1. Create a custom source for AIShield
Please follow [the official documentation](https://docs.aws.amazon.com/security-lake/latest/userguide/custom-sources.html) to register AIShield as a custom source.
The OCSF Event class to use is Security Finding and name custom source as AIShield.
To create the source:
1\. From the Amazon Security Lake console, select Custom sources.
2\. Select Create custom source. The Create custom data source page opens.

3\. Enter AIShield as the Data source name.
4\. Enter Security Findings as the OCSF event class.
5\. For AWS account with permission to write data, enter the AWS account ID and External ID(*Org\_ID)* of the custom source that will write logs and events to the data lake. Upon subscribing to the AIShield product through AWS Marketplace or by reaching out to our sales contact, following the registration, you can expect to receive a welcome email containing your Organization ID.
6\. In the Service Access section, create and use a new service role or use an existing service role for the Glue crawler. AWS Glue is used to crawl the data AIShield Threat Informed Endpoint Defense (EDR) pushes to the Security Lake. As a result, it needs permission to read it. Learn more about AWS Glue crawler.
7\. Select Create. An AWS Service Role name is created. The role has permission to push files into the Security Lake bucket, under the proper prefix.
8\. On the page that opens, copy the Bucket name under the Location section. You’ll need the bucket\_name, aws\_region, prefix, roleARN, externalID when configuring the integration in AIShield provided Threat Informed Endpoint Defense(EDR).

## 2.2. Connect AIShield Threat Informed Endpoint Defense(EDR) to Amazon Security Lake.
AIShield supports two deployment strategies. You can download the defense artifact after your job runs successfully. The defense artifact will contain the defense model in .h5 and .onnx formats, one Python file, and a readme file describing the steps to follow to use it. Assuming you have already downloaded the artifact, you can follow the steps below to configure the defense with amazon security lake.
AIShield provided Threat Informed Defense Model zip folder contains the following files.
1\. Defense Model Architecture image
2\. Defense Model Classification Report image
3\. Defense Model Confusion Matrix Image
4\. Defense Model (h5 format)
5\. defense\_model (onxx format)
6\. Predict.py
7\. ReadMe.txt
Following steps describe the procedure to integrate and test AIShield provided Threat Informed Defense Model(EDR).
**Note **: Ensure that your AWS credentials are properly configured (e.g., in your AWS CLI configuration or environment variables) since you need initial credentials to assume the role.
### Step 1: Install Python Packages
```python
pip install numpy
pip install tqdm
pip install tensorflow
pip install cv2
```
### Step 2: Import AISDefenseModel and necessary libraries
```python
from predict import AISDefenseModel
import tensorflow
import cv2
import numpy as np
```
### Step 3: Load the TensorFlow model
defense\_model\_path variable is used to store the file path or location on the local system where a defense model is expected to be found.
```python
defense_model = tensorflow.keras.models.load_model(defense_model_path)
```
### Step 4: Create AISDefenseModel with Connector
```python
model = AISDefenseModel(defense_model, aws_bucket_name, prefix, aws_role_arn,aws_region_name,external_id)
```
**Parameters:**
- `aws_bucket_name`:The name of the Amazon S3 bucket in which Security Lake stores your custom source data.
- `prefix`: Prefix for the custom source in your S3 bucket. Amazon Security Lake stores all S3 objects for a given source under this prefix, and the prefix is unique to the given source. e.g ext/AIShield
- `aws_role_arn`:The ARN of the role created by Amazon Security Lake at the Custom Source registration
- `aws_region_name`: AWS Region to which the data is written.
- `external_id`: Enter the ID that you specified when creating your Amazon Security Lake custom source.
- `roleARN`: ARN of your Amazon Security Lake to log event data.
### Step 5: Test AISDefenseModel
Load the necessary data and use AIShield provided attack data for testing the defense model.
```python
attack_data = load_data(attack_data_list)
model.predict(attack_data)
```
Once AIShield provided Threat Informed Endpoint Defense (EDR) app sending logs to Amazon Security Lake S3 bucket and you will be able to see.
## 2.3. Validation
After configuring Amazon Security Lake, data will be synced to your s3 bucket. Check the bucket and make sure new files are written under the prefix.
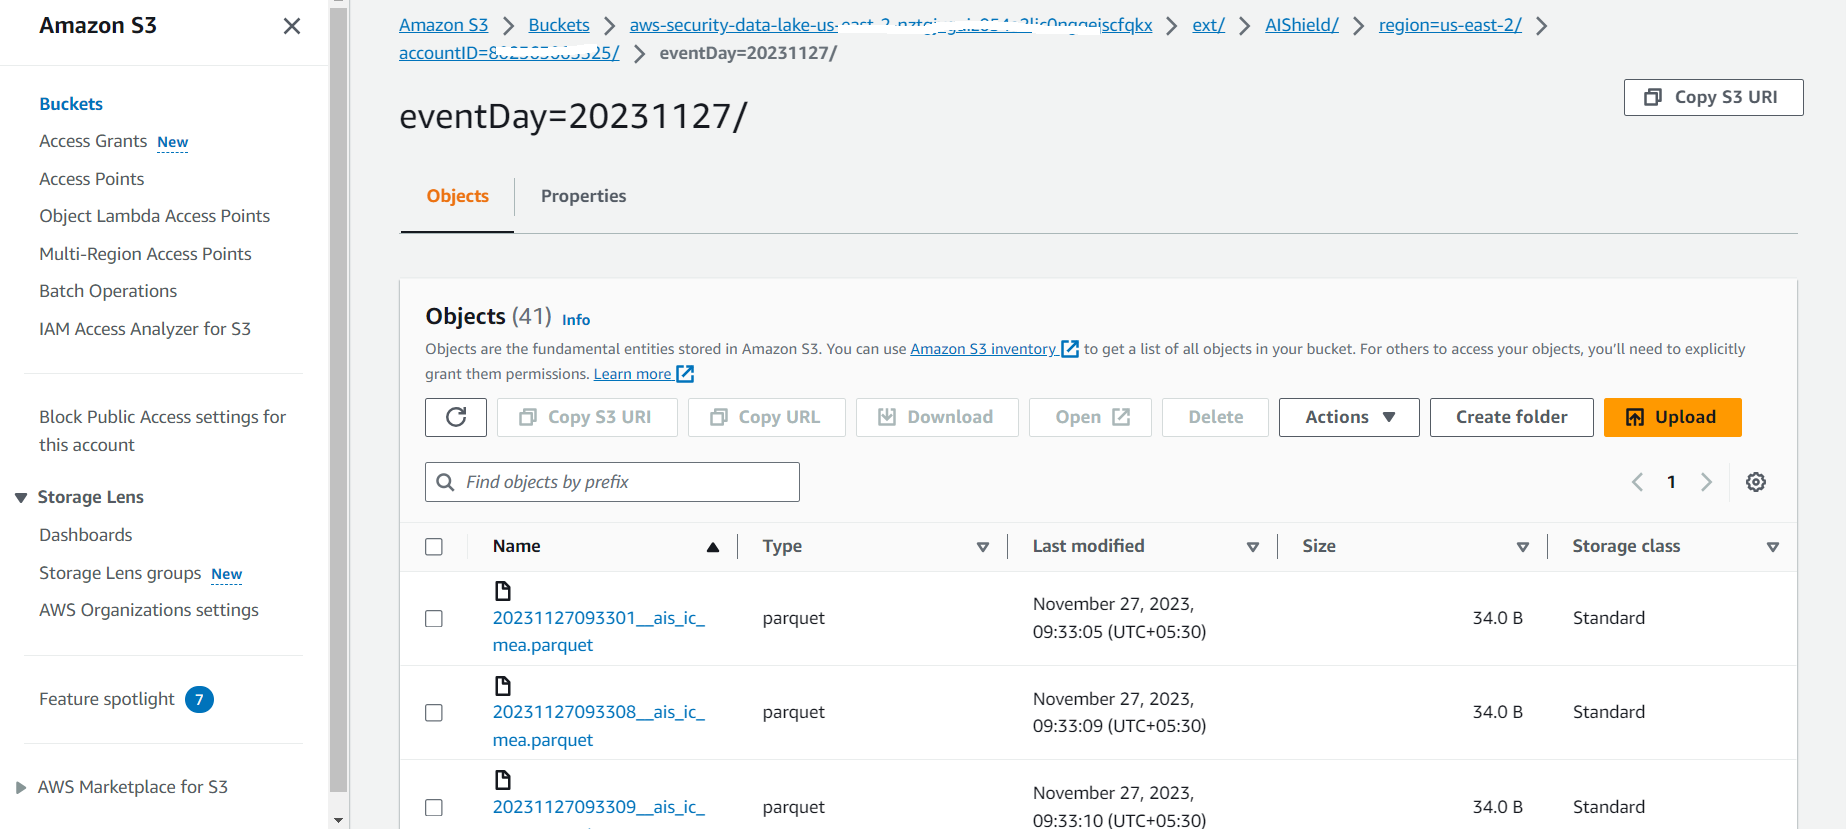
Contact AIShield support at AIShield.Contact\@bosch.com. if you have an issue validating or troubleshooting.
# 3. OCSF Information
The below table represents how the Detection properties are mapped from AIShield Threat Informed Endpoint Defense(EDR) format into the OCSF Security Finding Class.Read more here: [Open Cybersecurity Schema Framework](https://schema.ocsf.io/classes/security_finding)
| **OCSF Key** | **OCSF Value Type** | **AIShield Trigger API Value** |
| -------------------------------- | ------------------- | ------------------------------------------------- |
| activity\_id \* | Integer | New: 1, Ongoing: 2 |
| activity\_name | String | “Generate” |
| category\_uid \* | Integer | 2 |
| class\_name | String | “Security Finding” |
| class\_uid \* | Integer | 2001 |
| message | String | Detection.title |
| state\_id \* | Integer | 1 - New finding |
| type\_uid \* | Integer | Security Finding: Create |
| time \* | Timestamp | The normalized event occurrence time. |
| confidence\_score | Integer | The confidence score as reported by the AIShield. |
| risk\_level | String | The risk level idefined by the AIShield. |
| finding.uid \* | String | Detection.id |
| finding.title \* | String | Detection.title |
| finding.desc \* | String | Detection.description |
| metadata.labels \* | String | "AI Security","Image Classification" |
| metadata.product.lang \* | String | “en” |
| metadata.product.name \* | String | "AIShield" |
| metadata.product.version \* | String | System.version |
| metadata.product.vendor\_name \* | String | "AIShield AI Security Monitoring" |
| metadata.version \* | String | “1.0.0” |
| metadata.profiles \* | String | security\_finding |
| observables | List of Objects | \["IP Address","Hostname","Process Name"] |
| severity | String | Detection.riskScore |
| severity\_id \* | Integer | Detection.riskScore |
| | | |
```none
{
"activity_id": 1,
"activity_name": "Generate",
"category_uid": 2,
m "class_name": "AI Security Finding for Model Attack.",
"class_uid": 2001,
"message": "Image Classification AI Model Extraction Attack Identified",
"confidence_score":0.0,
"risk_level":"low suspicious attack",
"metadata": {
"labels": [
"AI Security",
"Image Classification",
],
"product": {
"lang": "en",
"name": "AIShield",
"vendor_name": "AIShield",
"version": "5.4"
},
"profiles": [
"security_finding"
],
"version": "0.39.0"
},
"finding": {
"title": "AIShield - Image classification model extraction
vulnerability detection",
"uid": "2",
"desc":"This query detects Image classification model extraction
vulnerability alert from AIShield. Please check the source
for more information and investigate further."
},
"observables": [
{
"name": "IP Address",
"type": "IP Address",
"type_id": 2,
"value": "IPAddr"
},
{
"name": "Hostname",
"type": "Email",
"type_id": 1,
"value": "hostname"
},
{
"name": "Process Name",
"type": "Email",
"type_id": 9,
"value": "image_classification_extraction_defense_engine"
}
],
"severity": "low",
"severity_id": 2,
"time": currenttime,
"type_uid": 200101,
"state_id": 1
}
```
# 4. Support
For help using the AIShield platform or the AIShield Threat Informed Endpoint Defense (EDR) App integration with Amazon Security Lake, please contact the AIShield support.
You can also send an email to AIShield.contact\@in.bosch.com with questions about this.
[title] Audio Speech Recognition
[path] API Documentation/AISpectra/Automated RedTeaming for AI/ML/ Model Analysis/Audio/
The below parameters are for various Audio speech recognition attack types. To know more about the different attack input parameters see [Automatic Speech Recognition](docId\:jzmdhfXEhv4mJlKb6GUsi)
:::CodeblockTabs
Evasion
```json
{
"use_model_api": "yes"
"model_api_details": "XXXXXXXXXXXXXXXXXXXXXXXXXX"
"model_framework": "onnx"
}
```
:::
:::ApiMethodV2{data="{"tab":"examples","url":"https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse","name":"Model anaylsis","method":"POST","request":{"pathParameters":[{"name":"model_id","kind":"optional","type":"string","description":"","children":[]}],"queryParameters":[],"headerParameters":[{"kind":"required","name":"x-api-key","type":"string","children":[],"description":"Enter your API key"},{"kind":"required","name":"Org_id","type":"string","children":[],"description":"Enter your organization id"}],"bodyDataParameters":[],"formDataParameters":[]},"results":{"languages":[{"id":"DL4HDcclTH6dUtOu-opbD","code":"// 200 OK: Returns a JSON object containing unique model ID and urls to upload required files.","language":"200","customLabel":""},{"id":"z5dS_OPIMHsxFEwrtKnkw","language":"401","code":"// 401 Unauthorized: Returns an error message if the provided API key or Org-ID is invalid or expired.","customLabel":""},{"id":"xJHL9zR5wAZ30f4gu2BUz","language":"400","code":"// 400 Bad request Error: Returns an error message if the application cannot or will not process the request due to something that is perceived to be a client error (for example, malformed request syntax, invalid request message framing, etc.)","customLabel":""},{"id":"eXy7xHvpQ-HT16gZp2CNA","language":"412","code":"// 412 precondition failed: Returns an error message if access to the target resource has been denied. (For example- if any of the parameter value is incorrect or license has expired)","customLabel":""}],"selectedLanguageId":"eXy7xHvpQ-HT16gZp2CNA"},"examples":{"languages":[{"id":"_mGBjlMU9k01Z6CEkara5","language":"python","code":"import requests\n\nmodelID=\"<< Enter Model ID >>\"\nurl = \"https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/\"+modelID+\"\"\n\n# please select proper payload for your usecase for extraction, evasion or poisoning.\npayload={\n # <>\n}\nheaders = {\n 'Accept': 'application/json',\n 'x-api-key': '########################################',\n 'Org-Id': '####################################################################################################'\n}\n\nresponse = requests.request(\"POST\", url, headers=headers, data=payload)\n\nprint(response.text)","customLabel":""},{"id":"EZTVIARgk4Cgsi2z3kaoP","language":"curl","code":"modelID=\"<< Enter Model ID >>\"\ncurl --location 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/${modelID}' \\\n--header 'x-api-key: ########################################' \\\n--header 'org_id: ####################################################################################################' \\\n--header 'Content-Type: application/json' \\\n--data '{\n <>\n}'","customLabel":""},{"id":"kc6RvtVQgBj0xpcZD7Nak","language":"nodejs","code":"var request = require('request');\n\nmodelID = '<>'\nvar options = {\n 'method': 'POST',\n 'url': 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/'+modelID+'',\n 'headers': {\n 'x-api-key': '########################################',\n 'org_id': '####################################################################################################',\n 'Content-Type': 'application/json'\n },\n body: JSON.stringify({\n // <>\n })\n\n};\nrequest(options, function (error, response) {\n if (error) throw new Error(error);\n console.log(response.body);\n});\n","customLabel":""},{"id":"Nx00RqrLXpofFTyDCguK0","language":"javascript","code":"var myHeaders = new Headers();\nmyHeaders.append(\"x-api-key\", \"########################################\");\nmyHeaders.append(\"org_id\", \"####################################################################################################\");\nmyHeaders.append(\"Content-Type\", \"application/json\");\n\nvar raw = JSON.stringify({\n // << Enter Payload Details based on Task pair >>\n});\n\nvar modelID = \"<< Enter Model ID >>\"\n\nvar requestOptions = {\n method: 'POST',\n headers: myHeaders,\n body: raw,\n redirect: 'follow'\n};\n\nfetch(\"https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/\"+modelID+\"\", requestOptions)\n .then(response => response.text())\n .then(result => console.log(result))\n .catch(error => console.log('error', error));","customLabel":""}],"selectedLanguageId":"_mGBjlMU9k01Z6CEkara5"},"description":"","currentNewParameter":{"label":"Path Parameter","value":"pathParameters"}}"}
:::
:::hint{type="info"}
te: In the response, copy job\_id. This value is required to trigger the GET APIs. See [\ Job Metadata](docId\:S-mZ7r0HNzicDQy6Q-6Hq).
The "job\_id" is used to retrieve model analysis metadata and check the processing status of the request. It is also used for generating reports for the analyzed model. Copy the dashboard link from the response and open it in a new tab. This allows users to monitor the job progress and download reports.
:::
**
[title] Quickstart tutorials
[path] /
[title] Supply Chain Attacks
[path] API Documentation/AISpectra/Model Scanner/
The Below parameters are for supply chain attacks. To know more about different input parameters and how to use API see [AI/ML Supply Chain](docId\:Xso05kOq-um_Byw47J0UB)
:::ApiMethodV2{data="{"tab":"examples","url":"https://api.aws.boschaishield.com/prod/api/ais/v1.5/supplychain","name":"Supply Chain Attacks","method":"POST","request":{"pathParameters":[],"queryParameters":[],"headerParameters":[{"kind":"required","name":"x-api-key","type":"string","children":[],"description":"Enter your API key"},{"kind":"required","name":"Org-Id","type":"string","description":"Enter your organization id","":"Org-Id"}],"bodyDataParameters":[{"name":"repo_type","kind":"required","type":"String","description":"The type of repository to scan (e.g., github, gitlab, bitbucket, huggingface, s3_bucket, azure_blob, gcp_storage).","":"The type of repository to scan (e.g., github, gitlab, bitbucket, huggingface, s3_bucket, azure_blob, gcp_storage)."},{"name":"repo_url","kind":"optional","type":"string","description":"URL of the repository to be scanned.","":"URL of the repository to be scanned."},{"name":"branch_name","kind":"optional","type":"string","description":"Name of the branch in the repository to be scanned (e.g., main, dev).","":"Name of the branch in the repository to be scanned (e.g., main, dev)."},{"name":"depth","kind":"optional","type":"Integer","description":"Number of recent commits to scan from the specified branch (e.g., depth: 10 scans the latest 10 commits).","":"optional"},{"name":"username","kind":"optional","type":"string","description":"Optional username used for authenticating access to private repositories when required (e.g., GitHub, GitLab, Bitbucket, huggingface).","":"Optional username used for authenticating access to private repositories when required (e.g., GitHub, GitLab, Bitbucket, huggingface)."},{"name":"pat","kind":"optional","type":"string","description":"Personal Access Token used for authenticating access to private repositories.","":"Personal Access Token used for authenticating access to private repositories."},{"name":"model_id","kind":"optional","type":"string","description":"Required if repo_type is file; identifier returned by the model ID generation API, used to locate the uploaded file for scanning.","":"Required if repo_type is file; identifier returned by the model ID generation API, used to locate the uploaded file for scanning."},{"name":"aws_access_key_id","kind":"optional","type":"string","description":"AWS access key ID used to authenticate and access S3 buckets when repo_type is s3_bucket.","":"AWS access key ID used to authenticate and access S3 buckets when repo_type is s3_bucket."},{"name":"aws_secret_access_key","kind":"optional","type":"string","description":"AWS secret access key paired with aws_access_key_id for authenticating access to S3 resources.","":"AWS secret access key paired with aws_access_key_id for authenticating access to S3 resources."},{"name":"region","kind":"optional","type":"string","description":"The AWS region where the S3 bucket is hosted (e.g., us-east-1, ap-south-1).","":"The AWS region where the S3 bucket is hosted (e.g., us-east-1, ap-south-1)."},{"name":"bucket_name","kind":"optional","type":"string","description":"Required if repo_type is s3_bucket or gcp_storage; specifies the name of the cloud storage bucket to be scanned. \nDefault : If no bucket name is provided, the bucket's under the provided credentials are auto-discovered and fully scanned. ","":"Required if repo_type is s3_bucket or gcp_storage; specifies the name of the cloud storage bucket to be scanned. \nDefault : If no bucket name is provided, the bucket's under the provided credentials are auto-discovered and fully scanned. "},{"name":"azure_connection_string","kind":"optional","type":"string","description":"Connection string used to authenticate and access Azure Blob Storage when repo_type is azure_blob.","":"Connection string used to authenticate and access Azure Blob Storage when repo_type is azure_blob."},{"name":"container_name","kind":"optional","type":"string","description":"Name of the Azure Blob Storage container to be scanned; required when repo_type is azure_blob.\nDefault : If no container name is provided, the container's under the provided credentials are auto-discovered and fully scanned. \n","":"Name of the Azure Blob Storage container to be scanned; required when repo_type is azure_blob.\nDefault : If no container name is provided, the container's under the provided credentials are auto-discovered and fully scanned. \n"},{"name":"service_account_json_file","kind":"optional","type":"object","description":"File containing the JSON key for a GCP service account; required for authentication when repo_type is gcp_storage.","":"File containing the JSON key for a GCP service account; required for authentication when repo_type is gcp_storage."}],"formDataParameters":[]},"results":{"languages":[{"id":"DL4HDcclTH6dUtOu-opbD","code":"// 200 OK: Returns a JSON object containing unique model ID and urls to upload required files.","language":"200","customLabel":""},{"id":"z5dS_OPIMHsxFEwrtKnkw","language":"401","code":"// 401 Unauthorized: Returns an error message if the provided API key or Org-ID is invalid or expired.","customLabel":""},{"id":"xJHL9zR5wAZ30f4gu2BUz","language":"400","code":"// 400 Bad request Error: Returns an error message if the application cannot or will not process the request due to something that is perceived to be a client error (for example, malformed request syntax, invalid request message framing, etc.)","customLabel":""},{"id":"eXy7xHvpQ-HT16gZp2CNA","language":"412","code":"// 412 precondition failed: Returns an error message if access to the target resource has been denied. (For example- if any of the parameter value is incorrect or license has expired)","customLabel":""}],"selectedLanguageId":"eXy7xHvpQ-HT16gZp2CNA"},"examples":{"languages":[{"id":"4nW1WnBd6npSuktVhukCc","language":"curl","code":"curl --location 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/supplychain' \\\n--header 'x-api-key: string' \\\n--header 'Org_id: string' \\\n--data {\"repo_type\":\"String\",\"repo_url\":\"String\",\"branch_name\":\"String\",\"depth\":\"Integer\",\"model_id\":\"String\",\"aws_access_key_id\":\"String\",\"aws_secret_access_key\":\"String\",\"region\":\"String\",\"bucket_name\":\"String\"}","customLabel":""},{"id":"mV0Gq6Fc0VTaO9OWg4fqq","language":"python","code":"import requests\n\nurl = \"https://api.aws.boschaishield.com/prod/api/ais/v1.5/supplychain\"\n\npayload = {\"repo_type\":\"String\",\"repo_url\":\"String\",\"branch_name\":\"String\",\"depth\":\"Integer\",\"model_id\":\"String\",\"aws_access_key_id\":\"String\",\"aws_secret_access_key\":\"String\",\"region\":\"String\",\"bucket_name\":\"String\"}\nheaders = {\n 'x-api-key': 'string',\n 'Org_id': 'string'\n}\n\nresponse = requests.request(\"POST\", url, headers=headers, data=payload)\n\nprint(response.text)\n","customLabel":""}],"selectedLanguageId":"mV0Gq6Fc0VTaO9OWg4fqq"},"description":"This api perform static assessment of files present in repos, local or s3 bucket for possible vulnerability","currentNewParameter":{"label":"Body Parameter","value":"bodyDataParameters"},"hasTryItOut":false}"}
:::
[title] Splunk
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/Threat Informed Defense/Configuration of Connector/
### Prerequisite
- You have to get the AIShield AI Security Monitoring App from Splunk marketplace to get started with below steps.
## **Features**
This app contains helpful security alerts and dashboards.
**SavedSearch**: Savedsearch creates high or medium severity alerts in Splunk Enterprise Security based on the AI model extraction attack probability.
**Dashboard**: The user can see model breach attack data over time and high and medium severity alert counts over time.
**Pre-requisite :**
Users will have to leverage AIShield product to scan their AI model for vulnerabilities and generate Threat Informed Endpoint Defense capable of integrating with Splunk Enterprise,Splunk Cloud and Splunk Enterprise Secuirty. To complete this step, please get in touch with AIShield.Contact\@bosch.com
## **Installation Instructions**
Please refer installation instructions links for Splunk Cloud and Splunk Enterprise to install AIShield AI Security Monitoring App for Splunk.

Once the application has been installed please follow the steps below to configure the application.
Create an Splunk HEC token for the app
Pre-requisite : Follow the instruction to create an custom index.
1. Select AIShield AI Security Monitoring App for Splunk from the App dropdown in the Splunk console.
2. Navigate to Settings > Data Input.
3. Add a new HTTP Event Collector token with a name of your choice.
4. Ensure indexer acknowledgement is not enabled.
5. Click Next and set the source type to \_\_json. Note : sourcetype value will be overwrite in HEC payload as "AIShield"
6. Add the \ index
7. Set the Default Index to \.
8. Click Review and then Submit.
**Note:** If you choose any other index, use the same while creating HEC token and updating the macro in the app. Follow the steps to set the macro to whatever index you have saved the data to as part of the HEC definition.
1\. Navigate to Settings --> Advanced Search
2\. Click on Search macro --> default\_index macro
3\. Update index value 'aishield\_index' to whatever index you have saved. : index="\"
4\. Click on save button
## Configure and connect AIShield provided Threat Informed Endpoint Defense with Splunk
1. Update the splunk endpoint url and token key in the AIShield provided Threat Informed Endpoint Defense.\[Please follow the above mentioned step to create the Splunk HEC token setup]
2. Update the url = "\>:8088/services/collector'>" and headers\["Authorization"] = "Splunk \"
3. The data will start showing after configuring both splunk\_hec and splunk endpoint url in the AIShield provided Threat Informed Endpoint Defense. You can view the logs with the following Splunk search:'default\_index'
After successful integration, AIShield provided Threat Informed Endpoint Defense will send logs to Splunk Enterprise or Splunk Cloud, Navigate to Activity --> Triggered alerts to see alerts.
- The splunk endpoint will respond with either a success or an error message. Follow steps in the
## Defense connector
You can download the defense artifact after your job runs successfully. The defense artifact will contain the defense model in .h5 and .onnx formats, one Python file, and a readme file describing the steps to follow to use it. Assuming you have already downloaded the artifact, you can follow the steps below to configure the defense with Azure Sentinel and Splunk Connector.
AIShield provided Threat Informed Defense Model zip folder contains the following files.
1\. Defense Model Architecture image
2\. Defense Model Classification Report image
3\. Defense Model Confusion Matrix Image
4\. Defense Model (h5 format)
5\. defense\_model (onxx format)
6\. Predict.py
7\. ReadMe.txt
Following steps describe the procedure to integrate and test AIShield provided Threat Informed Defense Model.
### Step 1: Install Python Packages
```python
pip install numpy
pip install tqdm
pip install tensorflow
pip install cv2
```
### Step 2: Import AISDefenseModel
```python
from predict import AISDefenseModel
import tensorflow
import cv2
import numpy as np
```
### Step 3: Load the TensorFlow model
defense\_model\_path variable is used to store the file path or location on the local system where a defense model is expected to be found.
```python
defense_model = tensorflow.keras.models.load_model(defense_model_path)
```
### Step 4: Create AISDefenseModel with Connector
```python
model = AISDefenseModel(defense_model, splunk_url, splunkauthorization)
```
**Parameters**:
- `splunk_url`: IP address or hostname of the Splunk server.
- `splunkauthorization`: Authorization key to connect to Splunk.
### Step 5: Test AISDefenseModel
Load the necessary data and use AIShield provided attack data for testing the defense model.
```python
attack_data = load_data(attack_data_list)
model.predict(attack_data)
```
Once AIShield provided Threat Informed Endpoint Defense (EDR) app sending logs to Splunk you will be able to see.
## Troubleshooting
No data displayed?
1\) While sending logs from AIShield provided Threat Informed Endpoint Defense, please make ensure that sourcetype is set with a name of 'AIShield'.
## Support
For any issues with this app, please send an email to [AIShield.Contact@bosch.com](mailto\:AIShield.Contact@bosch.com).
[title] Text Recommendation
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/Analyze your models/Text/
The below input parameters are for different attack types. To start working with the APIs, see [Text Recommendation (Alpha-release)](docId\:pF0-V4Ug62-akwbXCLkoZ)
:::hint{type="warning"}
Text Recommendation is an early access with limited functionality. It is not available in AIShield pypi package. For early access, kindly contact AIShield.Contact\@bosch.com
:::
### File upload format
- **Data**: The processed data, ready to be passed to the model for prediction, should be saved in a folder.
Download sample data
- **Model**: The model should be saved in either .h5 or TensorFlow format.
Download sample model
## Common parameters
The below table parameters are common for Extraction Attack type.
| Parameter | Data type | Description | Remark |
| ------------------------------ | --------- | ------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------ | ------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| model\_Id | String | Model\_id received during model registration.
We need to provide this model ID in query parameter in URL. | You have to do model registration only once for a model to perform model analysis. This will help you track the no of api call made, and it's success metric. |
| **Request Body (Json format)** | | | |
| model\_api\_details | String | If use\_model\_api is Yes, then provide API
details of hosted model as encrypted JSON
string is mandatory | provide this only if use\_model\_api is "yes". |
| use\_model\_api | String | Use model API to train your model instead of uploading the model as a zip file. | when this parameter is yes, you don't have to upload model as zip. You can pass api url along with other verification credential in json file. |
| model\_framework | String | Original model is built with tensorflow framework. | curretly supported framework are: tensorflow, scikit-learn, keras. (Option:\[tensorflow]) |
| title | string | movie title for the recommendation | movie title for which the recommendation is requested from model |
| encryption\_strategy | Int | Choose a encryption strategy for you model. if model is uploaded directly as a
zip pick 0, 1 if model is encryted as .pyc and
uploaded as a zip. Ignore if use\_model\_api is
Yes | select 0: pass tensorflow model as it is, select 1: pass encrypted model. It could be .pyc file |
:::hint{type="info"}
To access all sample artifacts, please visit [Artifacts](docId\:iJNEOCXoStabvvrsq11fa).
- For specific artifact details, refer
- Vulnerability Report : [Vulnerability Report](docId\:hL0uT2MWlCBkt8F97fr-W)
:::
:::hint{type="info"}
**Note**: For Text recommendation, supported attack types are - Extraction
:::
[title] Untitled
[path] /
[title] SIEM
[path] Integration Partners/
Security Information and Event Management (SIEM) is a critical component for securing machine learning (ML) systems. SIEM solutions provide intelligent security analytics and threat intelligence across the enterprise, allowing organizations to monitor and secure their ML models in real-time. By integrating SIEM solutions like Microsoft Sentinel or Splunk with AIShield, developers and data scientists can detect and respond to potential threats to their ML models quickly and effectively. These connectors offer detailed instructions on how to set up and configure AIShield with SIEM solutions, ensuring that your models remain secure and compliant.
::::LinkArray
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/PmsjKPPy_TrWLvcMOJ5Bc_splunk.jpg"}
[Splunk](docId\:Rtm85Xx_4fyLv_rwlK8Om)
:::
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/JxZJRzfbaryZHtXe3Jmjc_ehr-based-4.png"}
[Sentinel](docId:65GxnhPBgD-U4s2Q-JACe)
:::
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/FQ2yEm-Xeu1yyyNKShErs_amazonsecuritylake.webp"}
[Amazon Security Lake](docId\:gZGIkid5s8jfON07x7xWs)
:::
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/KPqkoWdQ7K1OlHoHfN7sV_ibmqradar.webp"}
[IBM QRadar](docId\:rgEo9c0CrQ0dxWIH6AQd4)
:::
::::
[title] Overview
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/Dashboard/
## Organization Overview
The Organization Overview page provides a comprehensive overview of the organization's security posture, risk reduction, time and cost savings, model vulnerability, and consumption status. It also offers insights into the enterprise-level model status, consolidated risk posture, security vulnerability, and attack distribution through a heatmap.
### Risk
The Risk section displays key risk-related metrics, including the reduction in risk compared to the previous month, the number of vulnerable models identified, and the number of defenses generated.
### Hours
The Hours section quantifies the time and cost savings achieved by the organization through efficient model security practices.
### Enterprise
The Enterprise section provides an overview of the organization's model landscape, highlighting the number of models requiring attention (indicated by a high vulnerability score), the total number of registered models, and the models currently under testing.
### Consumption
The Consumption section tracks the organization's resource consumption, indicating the extent to which allocated limits have been utilized based on the selected plan.
### Consolidated Risk Posture
The Consolidated Risk Posture presents a visual representation of the risk levels across all analyzed models for the selected month, including a percentage breakdown relative to the previous month of the current year.
### Security Vulnerability
The Security Vulnerability section offers insights into high-risk models by attack type, providing a percentage breakdown based on categories and the selected month.
### Heatmap
The Heatmap illustrates the distribution of attack types across different risk levels, showcasing the percentage share of each attack type relative to the total number of models.
By leveraging the information and insights provided in the Organization Overview, organizations can gain a comprehensive understanding of their security posture, make informed decisions, and prioritize remediation efforts to strengthen their overall model security.
[title] Image Classification
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/Analyze your models/Image/
The below input parameters are for different attack types. To start working with the APIs view the [Image Classification](docId:7pfTV3D26cUJsz6vMQloO).
## File upload format
- **Data**: The processed data, ready to be passed to the model for prediction, should be saved in a folder.
Download sample data
- **Label**: A CSV file should be created with two columns: "image" and "label." The first column should contain the image name, and the second column should contain the label. The label should be in integer format. Check sample label file attached.
Download sample label
- **Model**: The model should be saved in either .h5 or TensorFlow format with full architecture. Full architecture is needed when loading the model to the platofrm for assessment either in encrypted or unencrypted. This can be ignored when model is hosted as an API.
Download sample model
:::hint{type="warning"}
**Note**:
1. All files uploaded should be in zipped format. The above files are sample data for the MNIST use case.
2. ** Prerequisite: **Only 2-5 % of data is needed. The data should be representative and balanced across all classes.
1. **Model Extraction**: requires \~(450-900) samples or \~(50-100) samples per class.
2. **Model Evasion**: requires \~(810-1620) samples or \~(90-180) samples per class.
3. For poisoning, check poisoning section to get sample data, label and models.
:::
## Common parameters
The below table parameters are common for all attact types such as Extraction, Evasion, and Poisoning.
:::hint{type="info"}
To see the additional parameter specific for each attact type, such as Extraction and Evasion, refer to the below sections.
:::
| Parameter | Data type | Description | Remark |
| ------------------------------ | --------- | -------------------------------------------------------------------------------------------------------------- | ------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| model\_Id | String | Model\_id received during model registration.
We need to provide this model ID in query parameter in URL. | You have to do model registration only once for a model to perform model analysis. This will help you track the no of api call made, and it's success metric. |
| **Request Body (Json format)** | | | |
| normalize\_data | String | Model trained on Normalized data. | if model is trained on normalized data, then set this parameter as "yes" else "no". |
| input\_dimensions | String | Provide input dimension of the image | the parameter should be string in the format "(height, weight, channel)" For example 28\*28\*1 for MNIST |
| number\_of\_classes | String | Number of prediction classes. | the parameter should be string. Example MNIST : 10 (Range >0 & \<=200) |
| model\_framework | String | Original model is built with tensorflow framework. | curretly supported framework are: tensorflow, scikit-learn, keras. (Option:\[tensorflow]) |
:::ExpandableHeading
## Extraction parameters
| Parameter | Data type | Description | Remark |
| ------------------------------ | --------- | ------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------ | ------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| **Request Body (Json format)** | | | |
| attack\_type | String | You can select the attack type either Blackbox or Greybox. | **Blackbox**: for performing model analysis, no information about model or data will be used. **Greybox**: information about data will be leverage for creation of attack data **Note: **only 2-5 % of data is needed |
| number\_of\_attack\_queries | String | Number of attack queries that model will be
subjected to. | generally Heigher the number of attack queries, better would be the analysis. And it would take more time to process. (Range: >0 & \<=400000) |
| vulnerability\_threshold | String | Threshold percent of stolen model accuracy
at which defense model should be generated. | Threshold percent of stolen model accuracy
at which defense model should be generated
(Range : 0.0 - 1) |
| model\_api\_details | String | If use\_model\_api is Yes, then provide API
details of hosted model as encrypted JSON
string is mandatory | provide this only if use\_model\_api is "yes". |
| use\_model\_api | String | Use model API to train your model instead of uploading the model as a zip file. | when this parameter is yes, you don't have to upload model as zip. You can pass api url along with other verification credential in json file. |
| defense\_bestonly
| String | Choose to train your model until it achieves the best results or above 95% accuracy. | when selected **"yes"**, it will train N number of model and select best model. Ofcourse this will take longer time. If **"no"**, then once defense model accuracy reached above 95% It will stop |
| encryption\_strategy | Int | Choose a encryption strategy for you model. if model is uploaded directly as a
zip pick 0, 1 if model is encryted as .pyc and
uploaded as a zip. Ignore if use\_model\_api is
Yes | select 0: pass tensorflow model as it is, select 1: pass encrypted model. It could be .pyc file |
:::
:::ExpandableHeading
## Evasion Parameters
| Parameter | Data type | Description | Remark |
| ------------------------------ | --------- | --------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- | -------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| **Request Body (Json format)** | | | |
| model\_api\_details | String | If use\_model\_api is Yes, then provide API details of hosted model as encrypted JSON string is mandatory | provide this only if use\_model\_api is "yes". |
| use\_model\_api | String | Use model API to train your model instead of uploading the model as a zip. | when this parameter is yes, you don't have to upload model as zip. You can pass api url along with other verification credential in json file. |
| defense\_bestonly | String | Choose to train your model until it achieves the best results or above 95% accuracy. | when selected **"yes"**, it will train N number of model and select best model. Ofcourse this will take longer time. If **"no"**, then once defense model accuracy reached above 95% It will stop |
| encryption\_strategy | Int | Choose a encryption strategy for you model. if model is uploaded directly as a zip pick 0, 1 if model is encryted as .pyc and uploaded as a zip. Ignore if use\_model\_api is Yes | select 0: pass tensorflow model as it is, select 1: pass encrypted model. It could be .pyc file |
:::
:::ExpandableHeading
## Drift
- **Reference data** : The reference images or the clean images should be saved in a folder.
Download sample reference data
- **Reference label** : A CSV file should be created with two columns: "image" and "label." The first column should contain the image name, and the second column should contain the label. The label should be in integer format. Check sample label file attached.
Download sample reference label
- **Test data** : Dataset under test that might contain drifted images.
Download sample test data
- **Test label** : A csv file containing corresponding labels to the universal data, two
columns: ‘image’ and ‘label’. The ‘image’ column contains the image name including the extension, and the second column should contain the label. The label should be in integer format.
Download sample test label
:::
:::ExpandableHeading
## Outlier
- Date : Data in a ZIP format needs to be checked for the presence of outliers.
Download sample data
:::
:::ExpandableHeading
## Poisoning
- Data Poisoning
- **Universal Dataset** : Data containing potential poisoning data that needs to
be tested.
- Download sample universal dataset
- **Universal Label** : A csv file containing corresponding labels to the
universal data, two columns: ‘image’ and ‘label’. The ‘image’ column contains the imagename including the extension, and the second column should contain the label. The label should be in integer format.
- Download sample universal label
- **Data** : The processed data, ready to be passed to the model for prediction, should be saved in a folder.
- Download sample data
- **Label** : A CSV file should be created with two columns: "image" and "label." The first column should contain the image name, and the second column should contain the label. The label should be in integer format. Check sample label file attached.
- Download sample label
- **Model** : The model should be saved in either .h5 or TensorFlow format with full architecture. Full architecture is needed when loading the model to the platform for assessment.
- Download sample model
:::
:::ExpandableHeading
## Experimentation with values
To improve the accuracy, you can experiment with the following values for your attack input parameters. In our example we have used an MNIST dataset in our model and the below table reflects the parameters suitable for it. For more information, please refer to the reference implementation.
| Task Pair/Analysis Type | Type of Attack Strategy | No of queries | Outcome |
| ----------------------- | ------------------------ | -------------- | ------------------------------------- |
| Extraction | Blackbox | 60000 | Stolen model accuracy between 85%-90% |
| Extraction | Greybox | 20000 | Stolen model accuracy above 90% |
| Evasion | N/A | N/A | Evasion report |
| Poisoning | N/A | N/A | Model is poisoned or not. |
:::
:::hint{type="info"}
To access all sample artifacts, please visit [Artifacts](docId\:iJNEOCXoStabvvrsq11fa).
- For specific artifact details, refer
- Vulnerability Report : [Vulnerability Report](docId\:hL0uT2MWlCBkt8F97fr-W)
- Sample Attacks : [Sample Attacks](docId:4G1mjM5lQjfm8t5WBVwpr)
- Defense Report: [Defense Report](docId\:VtzlTtpja2VSF2j0STLSQ)
- Defense Model: [Defense Model](docId\:xSbxmZXW4vv14-8NmBF8M)
:::
:::hint{type="info"}
**Note**: For Image classification, supported attack types are - Extraction, Evasion and Poisoning, Drift and Outlier.
:::
[title] Getting started
[path] Platform guide/
You can get started with AIShield after subscribing to the AIShield product via AWS Marketplace or contacting our sales contact, after registration, you will receive a **welcome email** with your **Organization ID** which is required to setup AIShield for vulnerability analysis and reports and the link to access the UI .In free trial, you can make up to 7 vulnerability assessment calls to trigger scan and threat informed defense generation in the trial version.
Follow the below steps to get started with AIShield:
### User Interface
1. You can leverage the user interface to trigger a Static assessment (Supplychain analysis) by following the steps in this video tutorial . To trigger an Dynamic assessment (Evasion, Extraction, Poisoning) kindly follow steps in this video tutorial .
### Programmatic - API and SDK(PyPi)
1. [Installation](docId:2alZY96ErlECln6zijiZT) - Pypi and API installation guide for AIShield.
2. Welcome email - You will find credential details and information on how to generate x-api-key.
:::hint{type="info"}
We recommend using the model and data file we provided for the trial version. The trial version allows you to perform analysis on Image (Extraction, Evasion, Poisoning) Tabular (Extraction, Evasion) Time series (Forecasting). For more information see [Analyze your models](docId:5yPzn_yVV16Eojib5oT0U)
:::
You can check see [Limitations](docId:1rJoVQQ9SoqfnAiCTHNII) & [FAQ & Troubleshooting](docId\:go-zYw4AIUaKjXvxzE4Fh) for further details regarding compatibility.
[title] Image
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/Analyze your models/
::::LinkArray
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/tkBqH3j6mEzHvlGcJoCcP_ehr-based-6.png"}
[Image Classification](docId:6DEIiMJnkL5D0cdWSTCKb)
These parameters enable analysis of different attack types to evaluate your Image classification model.
:::
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/R_QOyIQ_kbEwlIR-6WhJO_image-segementation.jpeg"}
[Image Segmentation](docId\:BixNeMI0eUuJfUMau7eBx)
Automatically labeling images based on content for recognition and categorization in computer vision and AI applications.
:::
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/W7k3gvE7tafBGz21ImUgs_object-detection.png"}
[Object Detection](docId\:U3g1Wca-WL4Wed67BySah)
**Object detection** is a computer vision technique used to identify and locate objects within an image or video. It involves both classification (identifying what the object is) and localization (identifying where the object is in the image)
:::
::::
[title] Object Detection
[path] API Documentation/AISpectra/Automated RedTeaming for AI/ML/ Model Analysis/Image/
The below parameters are for various Object Detection attacks. To know more about the different attack input parameters see [Object Detection](docId\:U3g1Wca-WL4Wed67BySah)
:::hint{type="info"}
The values presented below are examples taken from the YOLO model used in the reference implementation. It is important to customize these values to achieve the best performance for your particular model.
:::
# Json Payload
:::CodeblockTabs
Evasion
```json
{
"normalize_data": "yes",
"model_framework": "onnx",
"defense_bestonly": "no",
"model_api_details": "na",
"use_model_api": "no",
}
```
:::
:::ApiMethodV2{data="{"tab":"examples","url":"https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse","name":"Model anaylsis","method":"POST","request":{"pathParameters":[{"name":"model_id","kind":"optional","type":"string","description":"","children":[]}],"queryParameters":[],"headerParameters":[{"kind":"required","name":"x-api-key","type":"string","children":[],"description":"Enter your API key"},{"kind":"required","name":"Org_id","type":"string","children":[],"description":"Enter your organization id"}],"bodyDataParameters":[],"formDataParameters":[]},"results":{"languages":[{"id":"DL4HDcclTH6dUtOu-opbD","code":"// 200 OK: Returns a JSON object containing unique model ID and urls to upload required files.","language":"200","customLabel":""},{"id":"z5dS_OPIMHsxFEwrtKnkw","language":"401","code":"// 401 Unauthorized: Returns an error message if the provided API key or Org-ID is invalid or expired.","customLabel":""},{"id":"xJHL9zR5wAZ30f4gu2BUz","language":"400","code":"// 400 Bad request Error: Returns an error message if the application cannot or will not process the request due to something that is perceived to be a client error (for example, malformed request syntax, invalid request message framing, etc.)","customLabel":""},{"id":"eXy7xHvpQ-HT16gZp2CNA","language":"412","code":"// 412 precondition failed: Returns an error message if access to the target resource has been denied. (For example- if any of the parameter value is incorrect or license has expired)","customLabel":""}],"selectedLanguageId":"eXy7xHvpQ-HT16gZp2CNA"},"examples":{"languages":[{"id":"_mGBjlMU9k01Z6CEkara5","language":"python","code":"import requests\n\nmodelID=\"<< Enter Model ID >>\"\nurl = \"https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/\"+modelID+\"\"\n\n# please select proper payload for your usecase for extraction, evasion or poisoning.\npayload={\n # <>\n}\nheaders = {\n 'Accept': 'application/json',\n 'x-api-key': '########################################',\n 'Org-Id': '####################################################################################################'\n}\n\nresponse = requests.request(\"POST\", url, headers=headers, data=payload)\n\nprint(response.text)","customLabel":""},{"id":"EZTVIARgk4Cgsi2z3kaoP","language":"curl","code":"modelID=\"<< Enter Model ID >>\"\ncurl --location 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/${modelID}' \\\n--header 'x-api-key: ########################################' \\\n--header 'Org-Id: ####################################################################################################' \\\n--header 'Content-Type: application/json' \\\n--data '{\n <>\n}'","customLabel":""},{"id":"kc6RvtVQgBj0xpcZD7Nak","language":"nodejs","code":"var request = require('request');\n\nmodelID = '<>'\nvar options = {\n 'method': 'POST',\n 'url': 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/'+modelID+'',\n 'headers': {\n 'x-api-key': '########################################',\n 'Org-Id': '####################################################################################################',\n 'Content-Type': 'application/json'\n },\n body: JSON.stringify({\n // <>\n })\n\n};\nrequest(options, function (error, response) {\n if (error) throw new Error(error);\n console.log(response.body);\n});\n","customLabel":""},{"id":"Nx00RqrLXpofFTyDCguK0","language":"javascript","code":"var myHeaders = new Headers();\nmyHeaders.append(\"x-api-key\", \"########################################\");\nmyHeaders.append(\"Org-Id\", \"####################################################################################################\");\nmyHeaders.append(\"Content-Type\", \"application/json\");\n\nvar raw = JSON.stringify({\n // << Enter Payload Details based on Task pair >>\n});\n\nvar modelID = \"<< Enter Model ID >>\"\n\nvar requestOptions = {\n method: 'POST',\n headers: myHeaders,\n body: raw,\n redirect: 'follow'\n};\n\nfetch(\"https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/\"+modelID+\"\", requestOptions)\n .then(response => response.text())\n .then(result => console.log(result))\n .catch(error => console.log('error', error));","customLabel":""}],"selectedLanguageId":"_mGBjlMU9k01Z6CEkara5"},"description":"","currentNewParameter":{"label":"Path Parameter","value":"pathParameters"}}"}
:::
:::hint{type="success"}
**Note**: In the response, job\_id and dashboard link will be available. Save these which would be used to track progress and download artifacts.
- For using Nodejs sample code, install npm package request
- Given sample code for python is tested for Python version 3.7
- Given Sample code for nodejs and javascript is tested for Node V20LTS
:::
[title] Untitled
[path] Platform guide/AISpectra/
[title] Integrate AIShield in 5 mins
[path] QuickStart tutorials/
# TL;DR
In under 30 minutes, follow the easy step-by-step process (including code snippets) presented in this guide to effortlessly integrate AIShield’s vulnerability analysis and defense generation features into your MLOps workflow. Experience these three key benefits by implementing AIShield:
- Benefit 1: Ensure the security, robustness, and resistance to adversarial attacks of your AI models by integrating AIShield in your MLOps pipeline.
- Benefit 2: Receive detailed vulnerability analysis and defense reports to identify and address potential weaknesses in your AI models.
- Benefit 3: Deploy secure, high-quality machine learning models with confidence, protecting your applications and users from adversarial attacks.
Act now to protect your organization’s AI models: Sign up for a FREE trial of AIShield API (AWS, non-AWS) today, and seize the opportunity to bolster security of AI model.
You can also check out Reference implementations here,
As AI developers, we strive to create robust and secure machine learning models. One essential aspect of this process is integrating security checks and vulnerability analysis within your MLOps pipeline. AIShield, an AI security platform, offers a powerful solution to analyze, detect, and mitigate potential vulnerabilities in your AI models. In this blog post, we will guide you through integrating AIShield in your MLOps pipeline to ensure your models are secure before deployment.
# Overview of AIShield:
AIShield is a comprehensive AI security platform designed to analyze machine learning models for potential vulnerabilities, generate defenses, and provide detailed reports for developers. By integrating AIShield in your MLOps pipeline, you can ensure your models are secure, robust, and resistant to adversarial attacks.
# Prerequisites:
To follow this guide, you should have a basic understanding of MLOps and experience with Python and machine learning libraries such as TensorFlow or PyTorch. You will also need an AIShield subscription to access the API.
## Train Your Model:
Before integrating AIShield, train your machine learning model using your preferred framework (e.g., TensorFlow or PyTorch).
For the remaining of the explanation, we assume that you have used MNIST dataset and trained a simple CNN model in tensorflow. Let’s have fun
# Steps to Integrate AIShield in Your MLOps Pipeline:
Below are the key steps for integrating AIShield into your MLOps pipeline, along with code snippets to guide you through the process.
1. **Install AIShield Package**
: Install the AIShield package using pip:
```python
pip install aishield
```
2. **Import AIShield Library**: In your Python script, import the AIShield library:
```python
import aishield as ais
```
3. **Prepare Your Model, Data, and Label Artifacts**: Create zip folders for your model, data, and label artifacts. This is required for uploading these artifacts to the AIShield API.
```python
"""
Description: Zip data
"""
from shutil import make_archive
import os
zip_path = "/path/to/zip/folder"
data_path = "/path/to/data/folder"
label_path = "/path/to/label/folder"
model_path = "/path/to/model/folder"
"""
Description: File paths
"""
make_archive(base_name=os.path.join(zip_path, "data"), root_dir=data_path, zip_format="zip")
make_archive(base_name=os.path.join(zip_path, "label"), root_dir=label_path, zip_format="zip")
make_archive(base_name=os.path.join(zip_path, "model"), root_dir=model_path, zip_format="zip")
```
4. ** AIShield API key**: follow the instruction provided in the email to generate API key / x\_api\_key. if you are using pypi package then , x-api-key generation is taken care from pypi side using given org\_id.
5. **Initialize AIShield API Client and Register the Model**: Create an AIShield API client instance, register your model, and upload the input artifacts (data, label, and model zip files).
```python
"""
Description: Initialize the AIShield API
"""
client = ais.AIShieldApi(api_url=url, org_id=org_id)
"""
Description: Define the task and analysis type
"""
task_type = ais.get_type("task", "image_classification")
analysis_type = ais.get_type("analysis", "extraction")
"""
Description: Perform model registration and upload the input artifacts
"""
status, job_details = client.register_model(task_type=task_type, analysis_type=analysis_type)
model_id = job_details.model_id
data_path = os.path.join(zip_path, 'data.zip')
label_path = os.path.join(zip_path, 'label.zip')
model_path = os.path.join(zip_path, 'model.zip')
upload_status = client.upload_input_artifacts(
job_details=job_details,
data_path=data_path,
label_path=label_path,
model_path=model_path,
)
print('Upload status: {}'.format(', '.join(upload_status)))
```
6. **Configure Vulnerability Analysis**: Define the vulnerability analysis configuration, such as input dimensions, number of classes, attack type, number of attack queries, and encryption strategy.
```python
"""
Description: Specify the appropriate configs required for vulnerability analysis
"""
input_shape = (28, 28, 1) # Example input shape for MNIST dataset
num_classes = 10 # Example number of classes for MNIST dataset
vuln_config = ais.VulnConfig(task_type=task_type,
analysis_type=analysis_type,
defense_generate=True)
vuln_config.input_dimensions = input_shape # input dimension for mnist digit classification
vuln_config.number_of_classes = = num_classes # number of classes for mnist digit classification
vuln_config.attack_type = = "greybox" # greybox or blackbox depending upon the availability of information about Model, Data and Parameters
vuln_config.attack_queries = 60000 # Number of attack queries to be generated for testing model vulnerability
vuln_config.encryption_strategy = 0 # value 0 (or) 1, if model is unencrypted or encrypted(pyc) respectively
```
7. **Perform Vulnerability Analysis**: Run the vulnerability analysis using the AIShield API client. Monitor the progress through the provided URL and fetch the job status using the Job ID.
```python
"""
Description: Specify the appropriate configs required for vulnerability analysis
"""
input_shape = (28, 28, 1) # Example input shape for MNIST dataset
num_classes = 10 # Example number of classes for MNIST dataset
vuln_config = ais.VulnConfig(task_type=task_type,
analysis_type=analysis_type,
defense_generate=True)
vuln_config.input_dimensions = input_shape # input dimension for mnist digit classification
vuln_config.number_of_classes = = num_classes # number of classes for mnist digit classification
vuln_config.attack_type = = "greybox" # greybox or blackbox depending upon the availability of information about Model, Data and Parameters
vuln_config.attack_queries = 60000 # Number of attack queries to be generated for testing model vulnerability
vuln_config.encryption_strategy = 0 # value 0 (or) 1, if model is unencrypted or encrypted(pyc) respectively
```
8. **Save and Download Reports and Artifacts**: Download the vulnerability report, defense reports, defense artifacts (e.g., the model), and attack samples. Save these files in a specified output folder for further review and analysis.
```python
"""
Description: Creating a directory to save the defense artifacts
"""
OUTPUT_PATH = os.path.join(os.getcwd(), "Output_Artifacts")
os.makedirs(OUTPUT_PATH, exist_ok=True)
if job_status.state == ais.get_type("job_state", "finished"):
# Download Vulnerability Report
output_conf = ais.OutputConf(report_type=ais.get_type("report", "vulnerability"),
file_format=ais.get_type("file_format", "pdf"),
save_folder_path=OUTPUT_PATH)
vulnerability_report = client.save_job_report(job_id=job_id, output_config=output_conf)
# Download Defense Report
output_conf = ais.OutputConf(report_type=ais.get_type("report", "defense"),
file_format=ais.get_type("file_format", "pdf"),
save_folder_path=OUTPUT_PATH)
defense_report = client.save_job_report(job_id=job_id, output_config=output_conf)
# Download Defense Model
output_conf = ais.OutputConf(report_type=ais.get_type("report", "defense_artifact"),
file_format=ais.get_type("file_format", "zip"),
save_folder_path=OUTPUT_PATH)
defense_artifact = client.save_job_report(job_id=job_id, output_config=output_conf)
# Download Attack Samples
output_conf = ais.OutputConf(report_type=ais.get_type("report", "attack_samples"),
save_folder_path=OUTPUT_PATH)
attack_samples = client.save_job_report(job_id=job_id, output_config=output_conf)
```
# Post using AIShield
## Analyzing and Implementing Improvements
Review the vulnerability and defense reports generated by AIShield. You can do either downloading the reports or using the dashboard to view the the model details. This helps you identify potential weaknesses and implement necessary improvements to enhance your model’s security by either hardening the model using supplied attack vectors or integrating the defense model provided.
**Deploy Your Secure Model**
Once you have addressed the vulnerabilities and enhanced your model, integrate the secure model back into your MLOps pipeline for deployment. This ensures that you are deploying a robust and secure machine learning model for real-world applications.
# Conclusion:
Integrating AIShield in your MLOps pipeline is an essential step for AI developers to ensure the security and robustness of their machine learning models. By following the steps outlined in this guide, you can seamlessly incorporate AIShield’s vulnerability analysis and defense generation capabilities into your MLOps workflow. This enables you to deploy secure, high-quality models with confidence, protecting your applications and users from potential adversarial attacks.
Act now to protect your organization’s AI models: Sign up for a FREE trial of AIShield API (AWS, non-AWS) today, and seize the opportunity to bolster security of AI model. You can also check out Reference implementations here.
[title] Untitled
[path] QuickStart tutorials/
[title] Untitled
[path] API Documentation/
[title] API Documentation
[path] /
[title] Untitled
[path] Platform guide/AISpectra/
[title] FAQ
[path] FAQ & Troubleshooting/
Welcome to our FAQ page about AI security and the AIShield platform! We've put together this page to answer some common questions you might have about securing your AI systems and how AIShield can help. We hope this page will give you a better understanding of AI security and how you can keep your systems safe. Let's get started!
### What is AI Security?
AI security refers to the domain of securing AI systems. One can also refer to cybersecurity for AI applications and models/algorithms. AI Security focuses on identifying, detecting, preventing, remediating, investigating, and responding to malicious attacks on AI Systems. The field is concerned with AI model vulnerabilities, studying attacker capabilities, consequences of attacks, and building algorithms that can resist security challenges.
### Why do organizations need to secure AI assets?
With the advancement in technology, there have been increasing AI algorithm failures. The complexity and number of such losses have been growing every day. Looking at some of the facts and the current industry scenario indicates the need for AI Security, and correct measures must be in place before a significant model failure.
- According to Microsoft, 89% of organizations do not have the right tools to secure their AI.
- Gartner found that 60% of AI providers will include a means to mitigate possible harm to their AI assets by 2024.
- IBM quotes that there is an 80% cost difference between cyberattack scenarios where secure AI was developed versus not deployed.
### What are various AI/ML adversarial attacks that AIShield protects against?
- Model Extraction: The act of stealing and extracting a proprietary model.
- Model Evasion: The act of making a model do the wrong thing, making it intentionally biased.
- Model/Data Poisoning: The act of making a model learn wrong things by injecting malicious samples.
- Model Inference: The act of making the model reveal its logic and data.
- Sponge attacks: A unique adversarial technique disrupting machine-learning systems with malicious inputs.
### What type of data can I use with AIShield?
AIShield can work with Image, Tabular, Timeseries, and Text data types.
### Do I own my data when using AIShield?
Absolutely. In fact, AIShield only needs a very small starting data (\<5% of original data), so AIShield can do a sanity check to know that we are able to successfully generate model output. Only in grey box strategies, AIShield will use the starting data to generate more targeted attack vectors.
### What integrations does AIShield support?
AIShield can be integrated seamlessly in any MLOps pipeline. There are multiple reference implementations available to show integrations to AWS Sagemaker, Azure ML, Google Vertex, ClearML, Snyk, Azure Sentinel, Splunk, and Databricks.
### Where is the AIShield defense model deployed?
The threat informed defense model can be deployed wherever the customer AI workload is either on Cloud or Embedded. Defense is delivered to the customer with the instruction on how to use.
### What is the difference in series and parallel deployment?
We have defense strategies that can self-harden the model and stop the malicious inputs. These might have some drop in model accuracy due to small false positive rates. Other strategies allow defense to be placed in series or parallel where it can block the input when in series or raise detection alerts when placed in parallel. In such scenarios, the system can take a call on remediation actions.
### What are the attack telemetry and what do they do?
Attack telemetry data is sent to enterprise SIEM/SOAR solutions like Azure Sentinel and Splunk from the connector built into the threat informed defense model. The attack telemetry contains necessary details like the severity of the attack instance, which model is under attack (image classification, tabular), what attack type (extraction, evasion, etc.), asset details, IP, etc.
[title] Configuration of Connector
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/Threat Informed Defense/
::::LinkArray
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/N7eIQ5zyp__17HXBXyWst_splunk.jpg"}
[Splunk](docId\:Rtm85Xx_4fyLv_rwlK8Om)
Powerful data analytics and monitoring platform for real-time insights.
:::
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/ZKbihU288AJSybe122eEz_qpq14ycztky63qgvfe1snehr-based-4.png"}
[Sentinel](docId:65GxnhPBgD-U4s2Q-JACe)
Advanced security platform for threat detection and response in real-time.
:::
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/LzpYyjnR1PgR0dt2nyqDp_capture3.PNG"}
[Amazon Security Lake](docId\:gZGIkid5s8jfON07x7xWs)
Powerful data analytics and monitoring platform for real-time insights.
:::
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/iWpvF_-HQffZh2UcRfu4N_logo1.jpg"}
[IBM QRadar](docId\:rgEo9c0CrQ0dxWIH6AQd4)
:::
::::
[title] Untitled
[path] API Documentation/
[title] Welcome to AIShield
[path] Introduction to AIShield/
AIShield is a new age security solution that protects AI models, such as image classification, time series, and tabular classification, from malicious attacks like theft and poisoning.
It analyzes vulnerabilities in AI models and generates customized defense. It is also designed to work with cloud-based microservices that can be easily automated, making it possible for organizations to scale quickly.
AIShield is essential for developers and stakeholders who want to keep their AI models secure. To learn more about AIShield, see [AIShield overview](docId\:fUFVfE76ReAYULMA_eSrw).
## Get started!
::::LinkArray
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/AAYwW2z7zRXiTF49EDWQd_login-page-1.jpg"}
[Getting started](docId\:roDh959jtwmQSbiTzRMIM)
Register for AIShield, Generate subscription key, follow installation process to get step up!
:::
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/7uY_RYozvKgNNUhlzY1xp_dashboardfeedback-changes.png"}
[Analyze your models](docId:5yPzn_yVV16Eojib5oT0U)
View supported model, perform vulnerability analysis on models, configure inputs, and generate reports.
:::
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/mYxl1Y--nitFz4Xex7PYr_stephen-dawson-qwtcej5clys-unsplash.jpg"}
[Threat Informed Defense](docId\:bXprg0VZOflG2S7meKREj)
Configuration of connectors like Splunk & Sentinel and deployment stratgies such as parallel & series deployment.
:::
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/eTOIMH1Z5HIjp8xj2Hg_6_aishield-1.png"}
[Integration Partners](docId\:jaWAQgPBflEn9L9AZhjsq)
AIShield is partnered with various AI platforms such as Amazon SageMaker, ClearML, and more!
:::
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/xsDVHt2EwqOIzGN4qA-HF_pexels-pixabay-270348.jpg"}
[FAQ & Troubleshooting](docId:1h32cJBTN2Oacbbz17gYi)
Get help and support for frequently ask questions and errors to quickly get started!
:::
::::
[title] Attack types
[path] Introduction to AIShield/AIShield overview/
AI systems have become increasingly popular in recent years due to their ability to quickly and accurately process large amounts of data. However, along with their benefits, they also face various types of attacks. Some of the most common types of attacks include model extraction attacks, Evasion, etc.
Developers must be aware of potential attacks and take measures to protect their AI systems, like implementing security protocols and monitoring for suspicious activity. This is where AIShield helps keep your models secure.
| Attack types | Description | Example |
| ----------------------------- | --------------------------------------------------------------------------------------------------------------------------------------------- | ---------------------------------------------------------------------- |
| **Model Extraction Attacks** | Attacker gains information about the model internals through analysis of input, output, and other external information. | Pedestrian detection |
| **Evasion Attacks** | Attacker induces an incorrect output from the model by making a very small change to the digital representation of the targeted input | Misclassification of input, malicious output execution |
| **Poisoning Attacks** | Attacker corrupts the data used to train the model by adding malicious data or changing data. | Compromising AI inference's correctness, inaccurate and poor decisions |
| **Inference Attacks** | Infer sensitive data from ML model outputs by querying and analyzing responses, enabling reconstruction of sensitive or training data. | Face reconstruction from outputs. |
| **Sponge attack** | It increases an ML model's energy consumption during inference, causing delays and potential harm, such as collisions in autonomous vehicles. | increase latency and delay operations in tasks. |
[title] Installation
[path] Platform guide/Getting started/
You can seamlessly integrate AIShield Vulnerability Assessment and Defense capabilities into your AI development workflows. With AIShield, you can generate assessment reports, sample attack vectors, and a threat-informed defense model with telemetry connection to SIEM/SOAR, such as Splunk and Microsoft Sentinel.
There are two ways to get started with AIShield:
1.) Installing using pypi package
2.) Directly using AIShield APIs
**Requirements**
Requires Python>=3.6, and pip >= 19.0
## Installation using pypi package
```python
$ pip install aishield
```
Enum for parameters:
- **analysis **:
- extraction
- evasion
- poisoning
- **task**:
- image\_classification
- image\_segmentation
- timeseries\_forecasting
- nlp
- tabular\_classification
- text\_recommendation
- object\_detection
- **report\_type**:
- vulnerability
- defense
- defense\_artifact
- attack\_samples
## Directly use AIShield APIs
```python
"""
Description: AIShield API URL and subscription key
"""
baseurl = "https://api.aws.boschaishield.com/prod"
url = baseurl + "/api/ais/v1.5"
headers={'Cache-Control': 'no-cache',
'x-api-key': "XXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXX", # follow instruction to generate API key and fill it here
'Org-Id' : "XXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXX" # fill in Org_Id provided in welcome email
}
```
Here are the installation steps for AIShield using its direct APIs:
1. You will get the **Org-ID** from the welcome email sent to you registered mail id.
2. You will also receive instruction and URL in welcome email, which you can use to generate API key (x-api-key).
3. Assign the `baseurl` concatenated with `"/api/ais/v1.5"` to the `url` variable.
4. Create a headers dictionary with the following key-value pairs:
- `'Cache-Control': 'no-cache'`
- `'x-api-key':` *insert your subscription key / API key here*
- `'Org-Id' :` *insert your Org-ID here*
5. You can now make requests to the AIShield API using the `url` and `headers` variables.
:::hint{type="info"}
After installation, you can have to register you model using [\ Model Registration](docId\:Qknp3vmRQaWJeZAeoChlH) API. To learn more, please refer this Reference implementation and view section 5.
:::
## Details
Check out the Quick Start Example here.
More references implementations, tutorials, samples, and documentation of AIShield can be found on our [Github Repository](https://github.com/bosch-aisecurity-aishield/Reference-Implementations).
**Pre-requisites:**
- AIShield API should be white-listed, or proxy settings must be appropriately configured for the AIShield API to be called.
- Valid AIShield API subscription plan and authentication keys. For details regarding subscription please visit, [Subscription Page](https://aws.amazon.com/marketplace/pp/prodview-ppbwtiryaohti) or reach out to sales at [AIShield.Contact@bosch.com]()
[title] Times Series Forecasting
[path] API Documentation/AISpectra/Automated RedTeaming for AI/ML/ Model Analysis/Time Series/
The below parameters are for various time series forecasting attack types. To know more about the different attack input parameters see [Time Series Forecasting](docId\:KDsa2HzsaXO0WcQIcDDc4).
:::hint{type="info"}
The values presented below are examples taken from the reference implementation. It is important to customize these values to achieve the best performance for your particular model.
:::
:::CodeblockTabs
Extraction
```json
{
"attack_type": "blackbox",
"defense_bestonly": "no",
"encryption_strategy": "0",
"input_dimensions": "100,6",
"model_api_details": "na",
"model_framework": "tensorflow",
"number_of_attack_queries": "10000",
"use_model_api": "no",
"vulnerability_threshold": "0"
}
```
:::
:::ApiMethodV2{data="{"tab":"examples","url":"https://api.aws.boschaishield.com/aishieldqa/prod/api/ais/v1.5/model_analyse","name":"Model anaylsis","method":"POST","request":{"pathParameters":[{"name":"model_id","kind":"required","type":"string","description":"","children":[]}],"queryParameters":[],"headerParameters":[{"kind":"required","name":"Org_id","type":"string","children":[],"description":"Enter your organization id"},{"kind":"required","name":"x-api-key","type":"string","children":[],"description":"Enter your API key"}],"bodyDataParameters":[],"formDataParameters":[]},"results":{"languages":[{"id":"DL4HDcclTH6dUtOu-opbD","code":"// 200 OK: Returns a JSON object containing unique model ID and urls to upload required files.","language":"200","customLabel":""},{"id":"3xaUVxaKWoReRICs9ePCq","language":"401","code":"// 401 Unauthorized: Returns an error message if the provided API key or Org-ID is invalid or expired.","customLabel":""},{"id":"IA3pkB4J3S-N_A54KmNk7","language":"400","code":"// 400 Bad request Error: Returns an error message if the application cannot or will not process the request due to something that is perceived to be a client error (for example, malformed request syntax, invalid request message framing, etc.)","customLabel":""},{"id":"e5a2eEF9OG9qJE0SsScGG","language":"412","code":"// 412 precondition failed: Returns an error message if access to the target resource has been denied. (For example- if any of the parameter value is incorrect or license has expired)","customLabel":""}],"selectedLanguageId":"e5a2eEF9OG9qJE0SsScGG"},"examples":{"languages":[{"id":"8MaUw5mcjRQxNhbkVqit-","language":"python","code":"import requests\n\nmodelID=\"<< Enter Model ID >>\"\nurl = \"https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/\"+modelID+\"\"\n\n# please select proper payload for your usecase for extraction, evasion or poisoning.\npayload={\n # <>\n}\nheaders = {\n 'Accept': 'application/json',\n 'x-api-key': '########################################',\n 'Org-Id': '####################################################################################################'\n}\n\nresponse = requests.request(\"POST\", url, headers=headers, data=payload)\n\nprint(response.text)","customLabel":""},{"id":"ivbSPphh1pvcfQfhM-rUz","language":"curl","code":"modelID=\"<< Enter Model ID >>\"\ncurl --location 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/${modelID}' \\\n--header 'x-api-key: ########################################' \\\n--header 'Org-Id: ####################################################################################################' \\\n--header 'Content-Type: application/json' \\\n--data '{\n <>\n}'","customLabel":""},{"id":"qbLPKbjE5vTcsGClILvBz","language":"nodejs","code":"var request = require('request');\n\nmodelID = '<>'\nvar options = {\n 'method': 'POST',\n 'url': 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/'+modelID+'',\n 'headers': {\n 'x-api-key': '########################################',\n 'Org-Id': '####################################################################################################',\n 'Content-Type': 'application/json'\n },\n body: JSON.stringify({\n // <>\n })\n\n};\nrequest(options, function (error, response) {\n if (error) throw new Error(error);\n console.log(response.body);\n});\n","customLabel":""},{"id":"fN1SReSSDFeJsHA7kmZt4","language":"javascript","code":"var myHeaders = new Headers();\nmyHeaders.append(\"x-api-key\", \"########################################\");\nmyHeaders.append(\"Org-Id\", \"####################################################################################################\");\nmyHeaders.append(\"Content-Type\", \"application/json\");\n\nvar raw = JSON.stringify({\n // << Enter Payload Details based on Task pair >>\n});\n\nvar modelID = \"<< Enter Model ID >>\"\n\nvar requestOptions = {\n method: 'POST',\n headers: myHeaders,\n body: raw,\n redirect: 'follow'\n};\n\nfetch(\"https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/\"+modelID+\"\", requestOptions)\n .then(response => response.text())\n .then(result => console.log(result))\n .catch(error => console.log('error', error));","customLabel":""}],"selectedLanguageId":"8MaUw5mcjRQxNhbkVqit-"},"description":"","currentNewParameter":{"label":"Path Parameter","value":"pathParameters"}}"}
:::
:::hint{type="info"}
Note: In the response, copy job\_id. This value is required to trigger the GET APIs. See [\ Job Metadata](docId\:S-mZ7r0HNzicDQy6Q-6Hq).
The "job\_id" is used to retrieve model analysis metadata and check the processing status of the request. It is also used for generating reports for the analyzed model. Copy the dashboard link from the response and open it in a new tab. This allows users to monitor the job progress and download reports.
:::
:::hint{type="info"}
For using Nodejs sample code, install npm package request
Given ample code for python is tested for Python version 3.7
Given Sample code for nodejs and javascript is tested for Node V20LTS
:::
[title] Model Registration
[path] API Documentation/AISpectra/Automated RedTeaming for AI/ML/
`POST /api/ais/v1.5/model_registration/upload`
:::ApiMethodV2{data="{"tab":"examples","url":"https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_registration/upload","name":"Model registration","method":"POST","request":{"pathParameters":[],"queryParameters":[],"headerParameters":[{"kind":"required","name":"x-api-key","type":"String","children":[],"description":"Enter your API key"},{"kind":"required","name":"Org-Id","type":"String","children":[],"description":"Enter your organization id"}],"bodyDataParameters":[{"name":"task_type","kind":"required","type":"string","description":"Enter the name of the task type","children":[]},{"name":"analysis_type","kind":"required","type":"string","description":"Enter the name of the analysis type","children":[]}],"formDataParameters":[]},"results":{"languages":[{"id":"hSUK1xBPtzdznmhzmPprP","code":"// Returns a JSON object containing a unique model ID and URLs to upload required files.","language":"200","customLabel":""},{"id":"HKv5X2EmhgwF7TNx8I0hi","code":"// Returns an error message if the provided API key or Org-ID is invalid or expired.","language":"401","customLabel":""},{"id":"aTEZrqZETJE4hWhVwXWYU","code":"// Returns an error message if the application cannot or will not process the request due to something that is perceived to be a client error (for example, malformed request syntax, invalid request message framing, etc.).","language":"400","customLabel":""},{"id":"y0GaITZN0HBUWyh0nGXjF","code":"// Returns an error message if access to the target resource has been denied (for example, if any of the parameter value is incorrect or license has expired).","language":"412","customLabel":""}],"selectedLanguageId":"hSUK1xBPtzdznmhzmPprP"},"examples":{"languages":[{"id":"OJTL2RNWtcse8ozCLYmCD","language":"python","code":"import requests\nimport json\n\nurl = \"https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_registration/upload\"\n\n# please select proper payload for your usecase from request body. \npayload = {\n 'task_type':\"<>\",\n \"analysis_type\": \"<>\"\n}\nheaders = {\n 'Accept': 'application/json',\n 'x-api-key': '########################################',\n 'Org-Id': '####################################################################################################'\n}\n\nresponse = requests.request(\"POST\", url, headers=headers, json=payload)\n\nprint(response.text)","customLabel":""},{"id":"Hh1J4ESuNjXCkLBQCGgh0","language":"curl","code":"curl --location 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_registration/upload' \\\n--header 'x-api-key: ########################################' \\\n--header 'Org-Id: ####################################################################################################' \\\n--header 'Content-Type: application/json' \\\n--data '{\n \"task_type\": \"<>\",\n \"analysis_type\": \"<>\"\n}'","customLabel":""},{"id":"yiYfhmky0U-ZzEhP_0tI1","language":"nodejs","code":"var request = require('request');\nvar options = {\n 'method': 'POST',\n 'url': 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_registration/upload',\n 'headers': {\n 'x-api-key': '########################################',\n 'Org-Id': '####################################################################################################',\n 'Content-Type': 'application/json'\n },\n body: JSON.stringify({\n 'task_type': '<< Enter Task Type >>',\n 'analysis_type': '<< Enter Analysis Type>>'\n })\n\n};\nrequest(options, function (error, response) {\n if (error) throw new Error(error);\n console.log(response.body);\n});\n","customLabel":""},{"id":"F8wphHI2uSCctKBFMO9nd","language":"javascript","code":"var myHeaders = new Headers();\nmyHeaders.append(\"Org-id\", \"####################################################################################################\");\nmyHeaders.append(\"x-api-key\", \"########################################\");\nmyHeaders.append(\"Content-Type\", \"application/json\");\n\nvar raw = JSON.stringify({\n \"task_type\": \"<>\",\n \"analysis_type\": \"<>\"\n});\n\nvar requestOptions = {\n method: 'POST',\n headers: myHeaders,\n body: raw,\n redirect: 'follow'\n};\n\nfetch(\"https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_registration/upload\", requestOptions)\n .then(response => response.text())\n .then(result => console.log(result))\n .catch(error => console.log('error', error));","customLabel":""}],"selectedLanguageId":"F8wphHI2uSCctKBFMO9nd"},"description":"The model registration API is used to register AI/ML models. It returns a unique model ID and URLs to upload the required files. We have listed the required sample files. These are the the model, data, and label files and you are required to upload them. The purpose of this API is to provide vulnerability analysis and generate customized endpoint defense to keep models secure.","currentNewParameter":{"label":"Body Parameter","value":"bodyDataParameters"}}"}
:::
### Request Body
:::CodeblockTabs
IC -MEA
```json
{
"task_type":"image_classification",
"analysis_type": "extraction"
}
```
IC - EVA
```json
{
"task_type":"image_classification",
"analysis_type": "evasion"
}
```
IC - POS
```json
{
"task_type":"image_classification",
"analysis_type": "data-poisoning"
}
```
IS - MEA
```json
{
"task_type":"image_segmentation",
"analysis_type": "extraction"
}
```
TC - MEA
```json
{
"task_type":"tabular_classification",
"analysis_type": "extraction"
}
```
TC - EVA
```json
{
"task_type":"tabular_classification",
"analysis_type": "evasion"
}
```
TSF - MEA
```json
{
"task_type":"timeseries_forecasting",
"analysis_type": "extraction"
}
```
NLP - MEA
```json
{
"task_type":"nlp_classification",
"analysis_type": "extraction"
}
```
TS - MEA
```json
{
"task_type":"timeseries_forecasting",
"analysis_type": "extraction"
}
```
OD-EVA
```python
{
"task_type":"object_detection",
"analysis_type": "evasion"
}
```
:::
The request body is a JSON object with the following fields:
:::hint{type="info"}
- `task_type`: The name of the task type. Possible values are `IC` (Image Classification, `IS` (Image Segmentation), `TC` (Tabular Classification), `TSF` (Time Series Forecasting), `Text` (NLP classification).
- `analysis_type`: The name of the analysis type. Possible values are `MEA` (Model Extraction Attack), `EVA` (Model Evasion Attack), and `data-poisoning` or `poisoning` for (data poisoning) and `model-poisoning` for (model poisoning).
:::
### Model Upload Option
`POST /ais/v1.5/model_registration/upload`
After receiving the unique model ID and URLs from the vulnerability analysis API, users can upload the required data and track the progress further.
Note: **All files uploaded to the specified URL should be in zipped format.** This only needs to be done once for any model and multiple analyses can be performed. Check [Image Classification](docId:6DEIiMJnkL5D0cdWSTCKb), [Image Segmentation](docId\:ZGifJwp4yRvB4Uog5-Qvh) [Tabular Classification](docId\:mVtLcTNKaSHPx9MzjvB62), [Time Series Forecasting](docId\:KDsa2HzsaXO0WcQIcDDc4) & [Text Recommendation (Alpha-release)](docId\:pF0-V4Ug62-akwbXCLkoZ), [Object Detection](docId\:U3g1Wca-WL4Wed67BySah) to know the file upload format.
:::hint{type="info"}
Note: The model, data, and label must be uploaded to the given link within ten minutes. For Image Classification Poisoning addition, two clean models are required.
The `model_id` must be saved by the user for future use.
:::
:::hint{type="info"}
For using Nodejs sample code, install npm package request
Given ample code for python is tested for Python version 3.7
Given Sample code for nodejs and javascript is tested for Node V20LTS
:::
[title] AI/ML Supply Chain
[path] Platform guide/AISpectra/Model Scanner/
## Overview
AI supply chain attacks occur when attackers modify or replace machine learning libraries, models, or associated data used by systems. Such vulnerabilities can lead to unauthorized system access or behavior manipulation.
To start working with the APIs, visit the [Supply Chain Attacks Guide](https://docs.boschaishield.com/api-docs/lesspostgreater-supply-chain-attacks).
***
## Key Features
### Report Generation
- Produces detailed reports classifying risks as **Low**, **Medium**, **High**, or **Critical**.
### Repository Integration
- Seamlessly integrates with GitHub, Huggingface, and AWS S3 for automated scanning of repositories and detecting vulnerabilities.
### Model Format Support
Supported frameworks and file formats include:
| Framework | File Format | Deserialization Risks | Backdoor Risks | Runtime Risks |
| ----------------------------- | --------------- | --------------------- | -------------- | ------------- |
| TensorFlow | .pb | ✅ | ✅ | |
| Tensorflow | .h5 | ✅ | ✅ | ✅ |
| TensorFlow/PyTorch Checkpoint | .ckpt | ✅ | | |
| Keras | .keras | ✅ | ✅ | |
| Keras | .h5 | ✅ | ✅ | |
| PyTorch | .pt, .pth, .bin | ✅ | | |
| ONNX | .onnx | | | ✅ |
| Scikit-Learn | .pkl | ✅ | | |
| GGUF | .gguf | | | ✅ |
| SafeTensor | .safetensor | ✅ | | |
| Misc | .zip | ✅ | | |
### Additional File Formats
| Framework | File Format | Detections |
| ---------------- | ----------- | -------------------------------------------------------- |
| Jupyter Notebook | .ipynb | Hardcoded secrets,Passwords PII, Tokens(API, Web, other) |
| Python | .py | Hardcoded secrets,Passwords PII, Tokens(API, Web, other) |
### AI Software Bill of Materials (SBOM)
| File Format | Detections |
| ---------------------------------- | ------------------------------- |
| Requirements File (Autodiscovered) | Libraries, Unsafe Library Flags |
| Jupyter Notebook (Autodiscovered) | Libraries, Unsafe Library Flags |
***
## Risk Analysis
### 1. Deserialization Risks
Occurs when unverified data is used to rebuild objects. Attackers may exploit these to introduce malicious code, compromising system integrity.
- **Activation:** Serialization attacks exploit the process of saving and loading machine learning models, specifically targeting vulnerabilities in the serialization and deserialization mechanisms. These attacks often involve malicious payloads embedded within serialized model files.
- **Purpose: **The primary goal of serialization attacks is to gain unauthorized access, execute arbitrary code, or manipulate the system in unintended ways. Attackers leverage the trust developers place in model files and frameworks, embedding harmful code that executes during deserialization to compromise environments, exfiltrate sensitive data, or alter system functionality.
- **Detection: **Serialization attack detection involves examining serialized files for suspicious code patterns and loading models in isolated environments, such as sandboxes, to monitor for unexpected behaviors or executions during deserialization.
### 2. Backdoor Risks
Hidden pathways allow attackers to manipulate model behavior through specific triggers. These covert exploits remain undetected during normal operations.
- **Activation:** Backdoor threats involve hidden pathways or triggers embedded in the model’s architecture that activate only when a specific input or condition is provided.
- **Purpose:** Backdoors are designed to manipulate model outputs for specific scenarios, enabling attackers to produce targeted malicious outputs without disrupting normal operations.
- **Detection:** Backdoor risks are harder to detect as they appear dormant in normal use but can be identified by analyzing model architecture for unusual pathways or using specialized tools like Netron for visual inspection and security scanners to detect presence of unusual code.
### 3. Runtime Risks
Activated during model inference or task execution, runtime risks involve malicious code execution, leading to unauthorized access or manipulation.
- **Activation:** These risks involve malicious code that executes during the model’s inference or runtime. The threat typically resides in the model files, and the malicious code is triggered as the model processes input data.
- **Purpose:** The aim is to compromise the system at runtime, such as gaining unauthorized access, stealing data, or altering the model’s behavior dynamically.
- **Detection:** Runtime risks often exploit code execution features in formats like TensorFlow’s SavedModel or Keras’ custom objects.
***
## Benefits
1. **Real-Time Scanning**: Quickly identifies vulnerabilities in AI/ML models and notebooks.
2. **Comprehensive Framework Support**: Compatible with diverse model frameworks.
3. **Dynamic Risk Identification**: Adapts to evolving security threats.
4. **Thorough Assessments**: Provides a full spectrum of vulnerability analysis.
5. **Standards Compliance**: Aligns with OWASP, MITRE, and CWE standards.
6. **Scalability**: Automated workflows ensure efficient scaling.
7. **Seamless Integration**: Effortless compatibility with popular AI/ML platforms.
8. **Detailed Reports**: Helps prioritize vulnerabilities and allocate resources.
9. **Competitive Advantage**: Showcases commitment to security, appealing to stakeholders and clients.
***
## Parameters
| Parameter | Data Type | Description | Remarks |
| ---------------------------------- | --------- | -------------------------------------------------------------------------------------------------------------------------------------- | ----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| `repo_type` | String | The type of repository to scan | (e.g., github,
gitlab, bitbucket,
huggingface,
s3\_bucket,
azure\_blob,
gcp\_storage
). |
| `repo_url` | String | URL of the repository to be scanned. | Formats accepted -
Hugginface - [https://huggingface.co/\<\>/\<\>](https://huggingface.co/\<\>/\<\>)
Github - [https://github.com/\<\>/\<\>](https://github.com/\<\>/\<\>) |
| `branch_name` | String | Name of the branch in the repository to be scanned | (e.g., main , dev). |
| `depth` | Integer | Number of recent commits to scan from the specified branch | e.g., depth: 10
scans the latest 10 commits. |
| `username`
| String | Username used for authenticating access to private repositories when required. | (e.g., GitHub, GitLab, Bitbucket, huggingface) |
| `pat` | String | Personal Access Token used for authenticating access to private repositories | (e.g., GitHub, GitLab, Bitbucket, huggingface)
The Personal Access Token must have sufficient permissions to read repository contents, metadata, and history—typically including
repo (for GitHub),
api (for GitLab), or equivalent scopes for other platforms. |
| `model_id` | String | Required if repo\_type is file; identifier returned by the model ID generation API, used to locate the uploaded file for scanning. | Obtainable during [\ Generate Model ID](docId\:ZQwTFEscleVi_vAP5AntH) |
| `aws_access_key_id` | String | AWS access key ID used to authenticate and access S3 buckets when **repo\_type is **
**s3\_bucket**. | It pairs with the **aws\_secret\_access\_key **to ensure secure access and authorization. |
| `aws_secret_access_key` | String | AWS secret access key paired with aws\_access\_key\_id
for authenticating access to S3 resources. | It works with the **aws\_access\_key\_id **to securely validate access permissions. |
| `region` | String | The AWS region where the S3 bucket is hosted | e.g., us-east-1,
ap-south-1
|
| `bucket_name` | String | Required if repo\_type
is s3\_bucket or
gcp\_storage ; specifies the name of the cloud storage bucket to be scanned | if not provided, all accessible buckets will be auto-detected and scanned (requires list and read permissions) |
| `azure_connection_string`
| String | Connection string used to authenticate and access Azure Blob Storage when
**repo\_type is azure\_blob**. | must have permissions to list containers and read blobs (e.g., via Storage Blob Data Reader or Contributor
roles). |
| `container_name`
| String | Name of the Azure Blob Storage container to be scanned; required when
**repo\_type is azure\_blob**.
| if not provided, all accessible containers will be auto-detected and scanned (requires list and read permissions). |
| `service_account_json_file`
| File | File containing the JSON key for a GCP service account; required for authentication when
**repo\_type is gcp\_storage**.
| must have permissions like
storage.buckets.list, storage.viewer, storage.objectViewer
for proper scanning access. |
***
## Sample Artifact
- Refer to the [Vulnerability Report](https://aisdocs.blob.core.windows.net/reference/Reports/supply-chain/VulnerabilityReport.pdf) for detailed insights.
***
## Appendix
### Glossary
- **Deserialization Risks**: Vulnerabilities arising during object reconstruction from untrusted data or files.
- **Backdoor Risks**: Undetected pathways that allow behavior manipulation.
- **Runtime Risks**: Threats triggered during inference or file execution.
For further queries, contact [Support]().
[title] Object Detection
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/Analyze your models/Image/
**Object detection** is a computer vision technique used to identify and locate objects within an image or video. It involves both classification (identifying what the object is) and localization (identifying where the object is in the image)
The below input parameters are for different attack types. To start working with the APIs view the [Object Detection](docId:8DgizRgxbOplGXgNGDRzu).
:::hint{type="warning"}
Object Detection is an early access with limited functionality. It is not available in AIShield pypi package. For early access, kindly contact AIShield.Contact\@bosch.com
:::
## File upload format
- **Data**: The processed data, ready to be passed to the model for prediction, should be saved in a folder.
Download sample data
- **Label**: A list of XML files that have the same names as the images in the dataset folder
Download sample label
- **Model**: The YOLO model should be saved in ONNX format and then zipped.
Download sample model
:::hint{type="warning"}
**Note**:
1. All files uploaded should be in zipped format. The above files are sample data for the Pascal VOC use case.
2. ** Prerequisite: **Only 2-5 % of data is needed.
:::
## Common parameters
The below table parameters are common for all attact types such as Extraction, Evasion, and Poisoning.
:::hint{type="info"}
To see the additional parameter specific for each attact type, such as Extraction and Evasion, refer to the below sections.
:::
| Parameter | Data type | Description | Remark |
| ------------------------------ | --------- | -------------------------------------------------------------------------------------------------------------- | ------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| model\_Id | String | Model\_id received during model registration.
We need to provide this model ID in query parameter in URL. | You have to do model registration only once for a model to perform model analysis. This will help you track the no of api call made, and it's success metric. |
| **Request Body (Json format)** | | | |
| normalize\_data | String | Model trained on Normalized data. | If model is trained on normalized data, then set this parameter as "yes" else "no". |
| model\_api\_details | String | If use\_model\_api is Yes, then provide API details of hosted model as encrypted JSON string is mandatory | Provide this only if use\_model\_api is "yes". |
| use\_model\_api | String | Use model API to train your model instead of uploading the model as a zip. | Use model API to train your model instead of uploading the model as a zip. |
| defense\_bestonly | String | Choose to train your model until it achieves the best results or above 95% accuracy. | When selected **"yes"**, it will train N number of model and select best model. Ofcourse this will take longer time. If **"no"**, then once defense model accuracy reached above 95% It will stop |
| model\_framework | string | Original model is built framework. | curretly supported framework are: onnx |
:::hint{type="info"}
To access all sample artifacts, please visit [Artifacts](docId\:iJNEOCXoStabvvrsq11fa).
- For specific artifact details, refer
- Vulnerability Report : [Vulnerability Report](docId\:hL0uT2MWlCBkt8F97fr-W)
- Sample Attacks : [Sample Attacks](docId:4G1mjM5lQjfm8t5WBVwpr)
- Defense Report: [Defense Report](docId\:VtzlTtpja2VSF2j0STLSQ)
- Defense Model: [Defense Model](docId\:xSbxmZXW4vv14-8NmBF8M)
:::
:::hint{type="info"}
**Note**: For Object Detection, supported attack types are - Evasion
:::
[title] MLOps
[path] Integration Partners/
AI Shield can integrate seamlessly with platforms such as WhyLabs and Databricks to enhance your MLOps pipeline. By implementing AI Shield into your MLOps pipeline, you can monitor model performance and safeguard against real-time attacks, ensuring that your models remain secure and compliant. This way, you can accelerate your machine learning initiatives and realize the full potential of your data.
Below is a list of ML pipelines and partner tools with which we integrate:
::::LinkArray
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/-XIXc93Z88Hu6KQ3a2mkC_model-monitoring-with-the-whylabs-ai-observability-platform-whylabs.png"}
[WhyLabs](docId\:mo1FcwwldVWb_OtJj-6Z5)
:::
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/8G4V6PSaeQfz2c5cUb5MN_mlflow-a-platform-for-the-machine-learning-lifecycle-mlflow.png"}
[MLFlow](docId\:NHHZUcrCA2dtpdrBeho5C)
:::
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/NoG408G9CRoNWsWikIQQ4_clearml-the-continuous-machine-learning-company.png"}
[Clear ML](docId\:C-TY4mKQBGbJ0oQUS-4vG)
:::
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/kFjJ8BBXJORyMsyxEiEW3_azureml.jpg"}
[Azure ML](docId\:kMXiLifvjecL2bcLCpNUb)
:::
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/UjquXufOAfV4ygoTrMN_a_data-lakehouse-architecture-and-ai-company-databricks.png"}
[Databricks](docId\:gKvAW7ENeEtQzrZT1CTo_)
:::
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/9nmj1F4T-bIaLCyOcjPXO_sagemaker.jfif"}
[Sagemaker](docId\:TBWGNshgMzTt095dm-zdT)
:::
::::
[title] Defense Report
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/Artifacts/
The report provides an overview of a defense model's accuracy and efficacy in detecting attacks on the original model. It emphasizes the significance of the defense model in preventing malicious attacks and their adverse consequences.
**1. Introduction**
This section provides a brief introduction to the report and sets the context for discussing the defense model's accuracy and efficacy.
**2. Performance**
This section focuses on evaluating the performance of the defense model by considering the inference time and providing a simulation report.
**2.1 Inference Time of Models**
This subsection explains the concept of inference time and its importance in deploying machine learning models in production environments. It highlights factors influencing inference time and states the specific inference time observed in the scenario.
**2.2 Simulation Report**
In this subsection, a table is presented that demonstrates the efficacy of the defense model in differentiating between original and attack data. The table includes information on the input size and the percentage of attack data detected. It clarifies the meaning of false positives and true positives in the context of the table.
**3. Defense Model Efficacy**
This section delves into the evaluation of the defense model's efficacy, focusing on accuracy and F1 score.
**3.1 Defense Model Accuracy**
Here, the concept of defense model accuracy is defined as a measure of the model's ability to correctly predict elements of the dataset as original or attack.
**3.2 Defense Model F1 Score**
This subsection explains the calculation of the defense model's F1 score, which combines precision and recall to evaluate its performance.
**4. Appendix**
The appendix section offers additional information on the methodology, defense model architecture, and relevant details such as the confusion matrix and classification reports of the model.
**4.1 Model Architecture**
A visual representation of the defense model architecture is presented in this subsection, providing a clear understanding of its structure.
**4.2 Confusion Matrix**
It describes how the matrix displays actual and predicted class labels and provides insights into the number of samples for each label combination.
**4.3 Classification Report**
The purpose of the classification report is explained, highlighting its utility in assessing model performance for each class and making informed decisions.
To see sample defense report for respective attack types, refer the below table.
| Input type | Defense report |
| ----------------------- | --------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| Image classification | Extraction, Evasion |
| Image segmentation | Extraction |
| Object Detection | Evasion |
| Tabular classification | Extraction, Evasion |
| Time series forecasting | Extraction Machine Learning, Extraction Deep Learning |
[title] Parallel Deployment
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/Threat Informed Defense/Deployment strategies/
In the parallel defense deployment, both the Threat-Informed Defense Model and the Original Model operate simultaneously. When a user sends a request, it passes through the API gateway and load balancer before reaching the Pre-processor.
In the Pre-processor, the data is processed before being sent to the Original Model. However, the processed data is also forwarded to the Defense Model. The Defense Model sends a control signal to the post-processor, which also receives the prediction value from the Original Model. Additionally, the Defense Model sends telemetry data to the SIEM tool through a connector.
This parallel deployment and control at the Post-processor stage ensures that there is no impact on the accuracy of the model.

[title] Image Segmentation
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/Analyze your models/Image/
The below input parameters are for different attack types. To start working with the APIs, see [\ Model Analysis](docId\:RPrtAbi5J-w_pPq9D-w1R).
### File upload format
- **Data**: The processed data, ready to be passed to the model for prediction, should be saved in a folder.
Download sample data
- **Label**: A CSV file should be created with two columns: "image" and "label." The first column should contain the image name, and the second column should contain the label. The label should be in integer format. Check sample label file attached.
Downloab sample label
- **Model**: The model should be saved in either .h5 or TensorFlow format with full architecture. Full architecture is needed when loading the model to the platofrm for assessment either in encrypted or unencrypted. This can be ignored when model is hosted as an API.
Download sample model
## Common parameters
The below table parameters are common for Extraction Attack type.
| Parameter | Data type | Description | Remark |
| ------------------------------ | --------- | -------------------------------------------------------------------------------------------------------------- | ------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| model\_Id | String | Model\_id received during model registration.
We need to provide this model ID in query parameter in URL. | You have to do model registration only once for a model to perform model analysis. This will help you track the no of api call made, and it's success metric. |
| **Request Body (Json format)** | | | |
| normalize\_data | String | Model trained on Normalized data. | if model is trained on normalized data, then set this parameter as "yes" else "no". |
| input\_dimensions | String | Provide input dimension of the image | the parameter should be string in the format "(height, weight, channel)" For example 28\*28\*1 |
| number\_of\_classes | String | Number of prediction classes. | the parameter should be string. Example : 10 (Range >0 & \<=200) |
| model\_framework | String | Original model is built with tensorflow framework. | curretly supported framework are: tensorflow, scikit-learn, keras. (Option:\[tensorflow]) |
:::ExpandableHeading
## Extraction parameters
| Parameter | Data type | Description | Remark |
| ------------------------------ | --------- | ------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------ | ------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| **Request Body (Json format)** | | | |
| attack\_type | String | You can select the attack type either Blackbox or Greybox. | **Blackbox**: for performing model analysis, no information about model or data will be used. **Greybox**: information about data will be leverage for creation of attack data **Note: **only 2-5 % of data is needed |
| number\_of\_attack\_queries | String | Number of attack queries that model will be
subjected to. | generally Heigher the number of attack queries, better would be the analysis. And it would take more time to process. (Range: >0 & \<=400000) |
| vulnerability\_threshold | String | Threshold percent of stolen model accuracy
at which defense model should be generated. | Threshold percent of stolen model accuracy
at which defense model should be generated
(Range : 0.0 - 1) |
| model\_api\_details | String | If use\_model\_api is Yes, then provide API
details of hosted model as encrypted JSON
string is mandatory | provide this only if use\_model\_api is "yes". |
| use\_model\_api | String | Use model API to train your model instead of uploading the model as a zip file. | when this parameter is yes, you don't have to upload model as zip. You can pass api url along with other verification credential in json file. |
| defense\_bestonly
| String | Choose to train your model until it achieves the best results or above 95% accuracy. | when selected **"yes"**, it will train N number of model and select best model. Ofcourse this will take longer time. If **"no"**, then once defense model accuracy reached above 95% It will stop |
| encryption\_strategy | Int | Choose a encryption strategy for you model. if model is uploaded directly as a
zip pick 0, 1 if model is encryted as .pyc and
uploaded as a zip. Ignore if use\_model\_api is
Yes | select 0: pass tensorflow model as it is, select 1: pass encrypted model. It could be .pyc file |
:::
:::hint{type="info"}
To access all sample artifacts, please visit [Artifacts](docId\:iJNEOCXoStabvvrsq11fa).
- For specific artifact details, refer
- Vulnerability Report : [Vulnerability Report](docId\:hL0uT2MWlCBkt8F97fr-W)
- Sample Attacks : [Sample Attacks](docId:4G1mjM5lQjfm8t5WBVwpr)
- Defense Report: [Defense Report](docId\:VtzlTtpja2VSF2j0STLSQ)
- Defense Model: [Defense Model](docId\:xSbxmZXW4vv14-8NmBF8M)
:::
:::hint{type="info"}
**Note**: For Image segmentation, supported attack types are - Extraction
:::
[title] Retrieve Artifacts
[path] API Documentation/AISpectra/
\ Retrieve the report and assets as part of the assessment `/api/ais/v1.5/get_report`
Report generation API helps generate defense ,vulnerability reports and attack samples. (vulnerability report, defense artifacts,attack\_samples). For generating reports, there are three parameters:
:::ApiMethodV2{data="{"tab":"examples","url":"https://api.aws.boschaishield.com/prod/api/ais/v1.5/get_report","name":"Retrieve reports","method":"GET","request":{"pathParameters":[],"queryParameters":[],"headerParameters":[{"kind":"required","name":"x-api-key","type":"string","children":[],"description":"Enter your API key"},{"kind":"required","name":"Org-id","type":"string","children":[],"description":"Enter your organization id"}],"bodyDataParameters":[{"name":"job_id","kind":"required","type":"string","description":"Enter uniquely created job_id received during model analysis.","children":[]},{"name":"report_type","kind":"required","type":"string","description":"You can generate different reports (vulnerability, defense and attack_samples)","children":[]},{"name":"file_format","kind":"required","type":"Number","description":"0 - 4 values can be used to generate the report. 0 = all, 2 = pdf, 3 = json","children":[]}],"formDataParameters":[]},"results":{"languages":[{"id":"TzI4VA5g2T21Ms5IVnv4i","code":"// Returns a JSON object containing the job details for every stage of vulnerability analysis & defense generation","language":"200","customLabel":""},{"id":"kBovGngwgeZFTQzu6B3A-","code":"// Returns an error message if the application cannot or will not process the request due to something that is perceived to be a client error (for example, malformed request syntax, invalid request message framing, etc.)","language":"400","customLabel":""},{"id":"vgao3JWyZIdVj8T0h3pJq","code":"// Returns an error message if access to the target resource has been denied.(For example- if x-api-key value is incorrect or not given)","language":"403","customLabel":""},{"id":"_TopuJFmieGM14B7qesQY","code":"// Returns an error message if access to the target resource has been denied. (For example- if any of the parameter value is incorrect or license has expired)","language":"412","customLabel":""},{"id":"PHZjxhqTuAOMecvlfiiFI","code":"// Returns an error message if the user has sent too many requests(example 15-20 requests in 1 seconds) in a given amount of time.","language":"429","customLabel":""}],"selectedLanguageId":"kBovGngwgeZFTQzu6B3A-"},"examples":{"languages":[{"id":"lPX5Xcm0T-jBs1f5Ym11S","language":"python","code":"import requests\n\njobID=\"<< Enter Job ID >>\"\nreportType=\"<< Enter Report Type >>\"\nfileFormat=\" << Enter File Format >>\"\n\nurl = \"https://api.aws.boschaishield.com/prod/api/ais/v1.5/get_report?job_id=\"+jobID+\"&report_type=\"+reportType+\"&file_format=\"+fileFormat+\"\"\n\npayload = {}\nheaders = {\n 'Accept': 'application/json',\n 'x-api-key': '########################################',\n 'Org-Id': '####################################################################################################'\n}\n\nresponse = requests.request(\"GET\", url, headers=headers, data=payload)\n\nprint(response.text)","customLabel":""},{"id":"IbCOymI1mJkWYG0jWCGG5","language":"curl","code":"jobID=\"<< Enter Job ID>>\";\nreportType=\"<< Enter Report Type>>\";\ncurl --location 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/get_report?job_id='${jobID}'&report_type='${reportType}'&file_format=2' \\\n--header 'Accept: application/json' \\\n--header 'x-api-key: ########################################' \\\n--header 'Org-Id: ####################################################################################################'","customLabel":""},{"id":"yRviph54DLvhhf6vg2zuO","language":"nodejs","code":"var request = require('request');\n\njobID = '<< Enter Job ID >>'\nreportType = '<>'\nfileFormat='<< Enter File Format >>'\nvar options = {\n 'method': 'GET',\n 'url': 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/get_report?job_id='+jobID+'&report_type='+reportType+'&file_format='+fileFormat+'',\n 'headers': {\n 'x-api-key': '########################################',\n 'Org-Id': '####################################################################################################'\n }\n};\nrequest(options, function (error, response) {\n if (error) throw new Error(error);\n console.log(response.body);\n});\n","customLabel":""},{"id":"vRIGveo83V9hRV9k__LDC","language":"javascript","code":"var myHeaders = new Headers();\nmyHeaders.append(\"x-api-key\", \"########################################\");\nmyHeaders.append(\"Org-Id\", \"####################################################################################################\");\n\nvar requestOptions = {\n method: 'GET',\n headers: myHeaders,\n redirect: 'follow'\n};\n\njobID=\"<>\"\nreportType=\"<< Enter Report Type >>\"\nfileFormat=\"<< Enter File Format >>\"\n\nfetch(\"https://api.aws.boschaishield.com/prod/api/ais/v1.5/get_report?job_id=\"+jobID+\"&report_type=\"+reportType+\"&file_format=\"+fileFormat+\"\", requestOptions)\n .then(response => response.text())\n .then(result => console.log(result))\n .catch(error => console.log('error', error));","customLabel":""}],"selectedLanguageId":"lPX5Xcm0T-jBs1f5Ym11S"},"description":"","currentNewParameter":{"label":"Query Parameter","value":"queryParameters"}}"}
:::
:::hint{type="info"}
- job\_id: Uniquely created `job_id `received during model analysis
- report\_type: parameter to define type of report to download. e.g vulnerability, defense and attack\_samples)
- file\_format: value between 0-4, 0 = all,2 = pdf, 3 = json
:::
:::hint{type="info"}
For using Nodejs sample code, install npm package request
Given ample code for python is tested for Python version 3.7
Given Sample code for nodejs and javascript is tested for Node V20LTS
:::
[title] Text Classification
[path] API Documentation/AISpectra/Automated RedTeaming for AI/ML/ Model Analysis/Text/
The below parameters are for text classification attack types. To know more about the different attack input parameters see [Text Classification](docId\:SmR1eb77SAocrYZljw07J)
:::hint{type="info"}
The values presented below are examples used in the reference implementation. It is important to customize these values to achieve the best performance for your particular model.
:::
:::CodeblockTabs
Extraction
```json
{
"use_model_api": "no",
"model_api_details": "no",
"number_of_classes": "2",
"attack_type": "blackbox",
"input_dimensions": "100",
"number_of_attack_queries": "20000",
"model_framework": "tensorflow",
"vulnerability_threshold": "0",
"defense_best_only": "no",
"encryption_strategy": = "1"
}
```
:::
:::ApiMethodV2{data="{"tab":"examples","url":"https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse","name":"Model anaylsis","method":"POST","request":{"pathParameters":[{"name":"model id","kind":"required","type":"string","description":"Enter your model","children":[]}],"queryParameters":[],"headerParameters":[{"kind":"required","name":"Org_id","type":"string","children":[],"description":"Enter your organization id"},{"kind":"required","name":"x-api-key","type":"string","children":[],"description":"Enter your API key"}],"bodyDataParameters":[],"formDataParameters":[]},"results":{"languages":[{"id":"DL4HDcclTH6dUtOu-opbD","code":"// 200 OK: Returns a JSON object containing unique model ID and urls to upload required files.","language":"200","customLabel":""},{"id":"z5dS_OPIMHsxFEwrtKnkw","language":"401","code":"// 401 Unauthorized: Returns an error message if the provided API key or Org-ID is invalid or expired.","customLabel":""},{"id":"xJHL9zR5wAZ30f4gu2BUz","language":"400","code":"// 400 Bad request Error: Returns an error message if the application cannot or will not process the request due to something that is perceived to be a client error (for example, malformed request syntax, invalid request message framing, etc.)","customLabel":""},{"id":"eXy7xHvpQ-HT16gZp2CNA","language":"412","code":"// 412 precondition failed: Returns an error message if access to the target resource has been denied. (For example- if any of the parameter value is incorrect or license has expired)","customLabel":""}],"selectedLanguageId":"eXy7xHvpQ-HT16gZp2CNA"},"examples":{"languages":[{"id":"uvpR8QRnC1HHhN9QUoXG7","language":"python","code":"import requests\n\nmodelID=\"<< Enter Model ID >>\"\nurl = \"https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/\"+modelID+\"\"\n\n# please select proper payload for your usecase for extraction, evasion or poisoning.\npayload={\n # <>\n}\nheaders = {\n 'Accept': 'application/json',\n 'x-api-key': '########################################',\n 'Org-Id': '####################################################################################################'\n}\n\nresponse = requests.request(\"POST\", url, headers=headers, data=payload)\n\nprint(response.text)","customLabel":""},{"id":"vCV7cMMWnkOdXcZnZkdAz","language":"curl","code":"modelID=\"<< Enter Model ID >>\"\ncurl --location 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/${modelID}' \\\n--header 'x-api-key: ########################################' \\\n--header 'Org-Id: ####################################################################################################' \\\n--header 'Content-Type: application/json' \\\n--data '{\n <>\n}'","customLabel":""},{"id":"eXSnYGLUlaNuxX2kBNo0C","language":"nodejs","code":"var request = require('request');\n\nmodelID = '<>'\nvar options = {\n 'method': 'POST',\n 'url': 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/'+modelID+'',\n 'headers': {\n 'x-api-key': '########################################',\n 'Org-Id': '####################################################################################################',\n 'Content-Type': 'application/json'\n },\n body: JSON.stringify({\n // <>\n })\n\n};\nrequest(options, function (error, response) {\n if (error) throw new Error(error);\n console.log(response.body);\n});\n","customLabel":""},{"id":"z1GlBsBw28gqg4d6hM6ST","language":"javascript","code":"var myHeaders = new Headers();\nmyHeaders.append(\"x-api-key\", \"########################################\");\nmyHeaders.append(\"Org-Id\", \"####################################################################################################\");\nmyHeaders.append(\"Content-Type\", \"application/json\");\n\nvar raw = JSON.stringify({\n // << Enter Payload Details based on Task pair >>\n});\n\nvar modelID = \"<< Enter Model ID >>\"\n\nvar requestOptions = {\n method: 'POST',\n headers: myHeaders,\n body: raw,\n redirect: 'follow'\n};\n\nfetch(\"https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/\"+modelID+\"\", requestOptions)\n .then(response => response.text())\n .then(result => console.log(result))\n .catch(error => console.log('error', error));","customLabel":""}],"selectedLanguageId":"z1GlBsBw28gqg4d6hM6ST"},"description":"","currentNewParameter":{"label":"Path Parameter","value":"pathParameters"}}"}
:::
:::hint{type="info"}
Note: In the response, copy job\_id. This value is required to trigger the GET APIs. See [\ Job Metadata](docId\:S-mZ7r0HNzicDQy6Q-6Hq).
The "job\_id" is used to retrieve model analysis metadata and check the processing status of the request. It is also used for generating reports for the analyzed model. Copy the dashboard link from the response and open it in a new tab. This allows users to monitor the job progress and download reports.
:::
:::hint{type="info"}
For using Nodejs sample code, install npm package request
Given ample code for python is tested for Python version 3.7
Given Sample code for nodejs and javascript is tested for Node V20LTS
:::
[title] Untitled
[path] API Documentation/AISpectra/
[title] Automated RedTeaming for GenAI
[path] Platform guide/AISpectra/Automated RedTeaming for GenAI/
# Automated RedTeaming for LLMs
## Overview
AISpectra's Automated RedTeaming for GenAI performs assessments to evaluate safety, security and privacy for models deployed in diverse **cloud environments** and **LLM Frameworks**.
:::ExpandableHeading
## User Manual
For complete usage instructions, please refer to the LLMRT user manual
:::
The following categories are considered during the assessment:
***
## 1. Safety
### Toxicity
Evaluate whether the model generates toxic, offensive, or harmful content. This includes hate speech, threats, abusive language, and any harmful biases.
### Not-Safe-For-Work (NSFW)
Assess the generation of content that is sexually explicit, graphic, or otherwise inappropriate for professional environments.
### Generic Harm
Review content that could cause harm, either directly or indirectly, through misinformation, self-harm encouragement, violence incitement, or dangerous instructions.
***
## 2. Security
### Jailbreak
Test for potential methods to bypass guardrails, enabling the model to output restricted or harmful content. This includes prompt injection and adversarial prompt testing.
### Sensitive Information Disclosure
Assess if the model can leak confidential, internal, or sensitive information.
***
## 3. Privacy
### PII (Personally Identifiable Information)
Test for accidental or intentional generation of personal data, such as names, addresses, phone numbers, or any information that can identify individuals.
### Sensitive PII
Evaluate for disclosure of sensitive personal data, including medical records, government-issued identifiers (e.g., Social Security Numbers), and other high-risk personal data.
***
## Supported Cloud Environments
- Azure OpenAI
- AWS Bedrock
- Google Cloud Platform
- Databricks LLM Deployment
- On-Prem / Self-hosted LLMs (Example: Models from Hugging Face)
***
## Supported Task Types
- Chatbot
- Instruction
- Question and Answering
- Summarization
- Visual (For multi-modal models)
***
## Reporting
1. **JSON Report**
- Machine-readable format** **optimized for easy ingestion into MLOps pipelines.
- Contains: Risk classifications, Attack Success Rate / Rejection Rate, Example Prompts and Metadata (model version, environment, timestamp)
2. **PDF Report**
- Executive summary** **for enterprise and leadership teams.
- Includes: Overall risk posture, Category-wise risk breakdown, Key observations & insights, Recommendations for remediation
3. **Dashboard **
- Interface** **providing: Consolidated view of all LLM assessments, Per-model risk overview, Category-wise details (Safety, Security, Privacy)
- Compliance and Standards coverage details - OWASP Top 10 for Generative AI/LLM, EU AI Act, MITRE ATLAS, NIST AI Risk Management Framework, ISO/IEC 42001
***
[title] Deployment on Edge Device
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/Threat Informed Defense/
AIShield defends against threats by deploying the Threat-Informed Defense Model on the Edge devices.
::::LinkArray
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/xdniXv-UG8DflTO8suVz__aws-green-grasss.jpg"}
[AWS IoT Greengrass Deployment](docId\:Sp56ahmEaVwzHnyY04w2X)
:::
::::
[title] Audio
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/Analyze your models/
::::LinkArray
:::LinkArrayItem{headerImage headerColor}
[Automatic Speech Recognition](docId\:jzmdhfXEhv4mJlKb6GUsi)
:::
::::
[title] Tabular
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/Analyze your models/
::::LinkArray
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/JkDAdqP3uzEwYlHZMSmuv_ehr-based-5.png"}
[Tabular Classification](docId\:mVtLcTNKaSHPx9MzjvB62)
These parameters enable analysis of different attack types to evaluate your Tabular model.
:::
::::
[title] Automatic Speech Recognition
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/Analyze your models/Audio/
The below input parameters are for different attack types. To start working with the APIs, see [Audio Speech Recognition](docId\:NlGwGbtjTaOqRQO8ITMya).
:::hint{type="warning"}
Audio Speech Recognition is an early access feature with limited functionality. It is not available as part of AIShield pypi package. For early access, kindly contact **AIShield.Contact\@bosch.com**
:::
-
:::hint{type="info"}
**ASR Models Support**:
1. **OpenAI-Whisper****: **All variants in PyTorch and Hugging Face formats are supported. Refer to the OpenAI-Whisper model card for the complete list of available variants. \[Ref: OpenAI-Whisper-ModelCard]
:::
# Common Parameter
The below table parameters are common for Evasion Attack type.
| Parameter | Data type | Description | Remark |
| ------------------------------ | --------- | -------------------------------------------------------------------------------------------------------------- | ------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| model\_Id | String | Model\_id received during model registration.
We need to provide this model ID in query parameter in URL. | You have to do model registration only once for a model to perform model analysis. This will help you track the no of api call made, and it's success metric. |
| **Request Body (Json format)** | | | |
| model\_framework | String | Framework on which model is trained on. | curretly supported framework are: **onnx **for **Evasion **and **pytorch **for **data-poisoning** . |
:::hint{type="info"}
To access all sample artifacts, please visit [Artifacts](docId\:iJNEOCXoStabvvrsq11fa).
- For specific artifact details, refer
- Vulnerability Report : [Vulnerability Report](docId\:hL0uT2MWlCBkt8F97fr-W)
- Sample Attacks : [Sample Attacks](docId:4G1mjM5lQjfm8t5WBVwpr)
:::
::::ExpandableHeading
# Evasion
## File upload format
- **Data**: The processed audio data, ready to be passed to the model for prediction, should be saved in a folder.
Download sample data
- **Label**: A CSV file should be created with two columns: "audio" and "label." The first column should contain the audio file name, and the second column should contain the label(text). Check sample label file attached.
Download sample label
- **Model**: The model should be saved in onnx format. This can be ignored when model is hosted as an API.
Download sample model
:::hint{type="warning"}
**Note**:
1. **Format:** All uploaded files must be in a zipped format.
2. **Dataset:** The provided files are sample audio data from the Librespeech dataset.
3. **Audio File Properties:** Each audio file should not exceed 30 seconds and must have a sampling rate of 16,000 Hz.
4. **Sample Count:** The minimum number of samples required must be between 300 and 500.
5. **Data Sampling Strategy:** Ensure that the uploaded samples are representative of the complete dataset, using techniques such as normal distributive sampling for even distribution.
:::
## Parameter
| Parameter | Data type | Description | Remark |
| ------------------------------ | --------- | -------------------------------------------------------------------------------------- | ----------------------------------------------------------------------------------------------------------------------------------------------- |
| **Request Body (Json format)** | | | |
| model\_api\_details | String | Provide API details of hosted model as encrypted JSON string
| provide this only if use\_model\_api is "yes". |
| use\_model\_api | String | Use model API to use your model endpoint instead of uploading the model as a zip file. | when this parameter is yes, you don't have to upload model as zip. You can pass api url along with other verification credential in json file. |
## Convert pytorch model to ONNX format for ASR
Converting Pytorch model to onnx will create two models (Encoder and Decoder) in onnx format.
- To Load an OpenAI Model:
- load\_model: "tiny.en", "base.en", "small.en", "medium.en", "large.en"
- To Load a Distil-Whisper Model:
- load\_model: model.bin or "distil-whisper/distil-large-v3"
### Loading of Whisper model
```python
import whisper, torch, onnxruntime
# load tiny model trained on whisper dataset
device = torch.device('cpu')
model = whisper.load_model('tiny.en').to(device) #Hugging Face --> Model.bin
tokenizer = whisper.decoding.get_tokenizer(False,language='en',task='transcribe') ##initialoze whisper tokenizer
model.requires_grad_(False)
model.eval()
```
### Convert to Onnx Format
** First load sample audio file to get the feature of audio signal:**
:::CodeblockTabs
python
```python
import librosa
audio = librosa.load(path_of_audio_file,sr=16000)[0] #sample audio file to load audio features
audio = whisper.pad_or_trim(audio)
log_mel = whisper.log_mel_spectrogram(audio).unsqueeze(axis=0)
```
:::
**Prepare the input for decoder model: **
:::CodeblockTabs
python
```python
input = log_mel.to(device)
audio_features = model.encoder(input)
dec_tokens = torch.tensor([tokenizer.sot_sequence_including_notimestamps],dtype=torch.long) ##decoder token
```
:::
**Convert and save model (encoder and decoder) in onnx format:**
:::CodeblockTabs
python
```python
#: ONNX export
##Encoder Export
torch.onnx.export(
model.encoder,
(log_mel,),
"distil_encoder.onnx",
input_names=["input_mel"],
output_names=["out"],
dynamic_axes={
"input_mel": {0: "batch"},
"out": {0: "batch"},
},
)
#Decoder Export
torch.onnx.export(
model.decoder,
(dec_tokens, audio_features),
"distil_decoder.onnx",
input_names=["tokens", "audio"],
output_names=["out"],
dynamic_axes={
"tokens": {0: "batch", 1: "seq"},
"audio": {0: "batch"},
"out": {0: "batch", 1: "seq"},
},
)
```
:::
::::
::::ExpandableHeading
# Data-Poisoning
## File upload format
- **Reference Data**: The processed clean audio data, ready to be passed to the model for prediction, should be saved in a folder.
Download sample data
- **Refernce Label**: A CSV file corresponding to clean data should be created with two columns: "audio" and "label." The first column should contain the audio file name, and the second column should contain the label(text). Check sample label file attached.
Download sample label
- **Model**: The model should be saved in onnx format. This can be ignored when model is hosted as an API.
Download sample model
- **Universal Data**: Audio samples under test (poisoned, clean samples), should be saved in a folder .
Download sample universal data
- **Universal Label**: A CSV files corresponding to universal data hould be created with two columns: "audio" and "label." The first column should contain the audio file name, and the second column should contain the label(text). Check sample label file attached.
Download sample universal label
:::hint{type="warning"}
**Note**:
1. **Format:** All uploaded files must be in a zipped format.
2. **Dataset:** The provided files are sample audio data from the Librespeech dataset.
3. **Audio File Properties:** Each audio file should not exceed 30 seconds and must have a sampling rate of 16,000 Hz.
4. **Sample Count:** The minimum number of samples required must be between 500 to 700.
5. **Data Sampling Strategy:** Ensure that the uploaded samples are representative of the complete dataset, using techniques such as normal distributive sampling for even distribution.
:::
## Conversion of OpenAI-Whisper models to HuggingFace format
::embed[]{url="https://gist.github.com/c4f0feb9fbb5a79d0726fc8baa2cc305.js"}
::::
[title] Untitled
[path] Platform guide/AISpectra/
[title] Supply chain update policy
[path] API Documentation/AISpectra/Model Scanner/
The **Supply Chain Update Policy API ** allows users to **update security policies **related to repository scans. This enables customization of **scan format suppression, file format suppression, vulnerability types, and tool strictness levels **, **GenAI framework detection**, **report generation**, etc. ensuring compliance with security requirements.
:::ApiMethodV2{data="{"name":"update_policy","method":"POST","url":"https://api.aws.boschaishield.com/prod/api/ais/v1.5/developer/update_policy","description":"This API requires a JSON request body containing the policy updates.","tab":"examples","examples":{"languages":[{"id":"frgapb2aD4_u5WQrU_rAS","language":"python","code":"import requests\n\nurl = \"https://api.aws.boschaishield.com/prod/api/ais/v1.5/generate_model_id\"\n\npayload = {}\nheaders = {\n 'x-api-key': 'string',\n 'Org-Id': 'string'\n}\n\nresponse = requests.request(\"POST\", url, headers=headers, data=payload)\n\nprint(response.text)\n","customLabel":""},{"id":"HWvu0IcWyYs9t1z8WWABJ","language":"curl","code":"curl --location --request POST 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/generate_model_id' \\\n--header 'x-api-key: string' \\\n--header 'Org-Id: string'","customLabel":""},{"id":"cgJ5_5dDTBZwDAuJTn5A9","language":"nodejs","code":"var request = require('request');\nvar options = {\n 'method': 'POST',\n 'url': 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/generate_model_id',\n 'headers': {\n 'x-api-key': 'string',\n 'Org-Id': 'string'\n }\n};\nrequest(options, function (error, response) {\n if (error) throw new Error(error);\n console.log(response.body);\n});\n","customLabel":""},{"id":"Zp0KHmgw1W3fWtEQB2FGN","language":"javascript","code":"var myHeaders = new Headers();\nmyHeaders.append(\"x-api-key\", \"string\");\nmyHeaders.append(\"Org-Id\", \"string\");\n\nvar requestOptions = {\n method: 'POST',\n headers: myHeaders,\n redirect: 'follow'\n};\n\nfetch(\"https://api.aws.boschaishield.com/prod/api/ais/v1.5/generate_model_id\", requestOptions)\n .then(response => response.text())\n .then(result => console.log(result))\n .catch(error => console.log('error', error));","customLabel":""},{"id":"Vj8db-_tfEQaZwm4gTamg","language":"ruby","code":"require \"uri\"\nrequire \"net/http\"\n\nurl = URI(\"https://api.aws.boschaishield.com/prod/api/ais/v1.5/generate_model_id\")\n\nhttps = Net::HTTP.new(url.host, url.port)\nhttps.use_ssl = true\n\nrequest = Net::HTTP::Post.new(url)\nrequest[\"x-api-key\"] = \"string\"\nrequest[\"Org-Id\"] = \"string\"\n\nresponse = https.request(request)\nputs response.read_body\n","customLabel":""}],"selectedLanguageId":"frgapb2aD4_u5WQrU_rAS"},"results":{"languages":[{"id":"N1fpC35SZxbcEWxck2pSW","language":"200","customLabel":"","code":"//200: policy updated successfully"},{"id":"HoRypJvdzSbrZlIR1DsHs","language":"401","code":"// 401 Unauthorized: Returns an error message if the provided API key or Org-ID is invalid or expired.","customLabel":""},{"id":"iDVOSM2kLZnuhseONktcg","language":"400","customLabel":"","code":"// 400 Bad request Error: Returns an error message if the application cannot or will not process the request due to something that is perceived to be a client error (for example, malformed request syntax, invalid request message framing, etc.)"},{"id":"FxGZoAFylQRraTE0xU1u7","language":"412","code":"// 412 precondition failed: Returns an error message if access to the target resource has been denied. (For example- if any of the parameter value is incorrect or license has expired)","customLabel":""}],"selectedLanguageId":"N1fpC35SZxbcEWxck2pSW"},"request":{"pathParameters":[],"queryParameters":[],"headerParameters":[{"name":"x-api-key","kind":"required","type":"string","description":"Enter your API key","":"required"},{"name":"Org-Id","kind":"required","type":"string","description":"Enter your organization id","":"Enter your organization id"}],"bodyDataParameters":[{"name":"file_format_suppression","kind":"required","type":"object","description":"The file_format_suppression policy allows users to suppress scanning for specific file extensions. If suppressed is set to True, the specified file types will skipped during the supply chain security analysis.","":"required","children":[{"name":".bin","kind":"required","type":"object","description":"file extension of the file","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"If suppressed is set to True, the policy is active, and the file will be skipped during scanning. If set to False, the policy is inactive, and the file will be considered for analysis."}]},{"name":".ckpt","kind":"required","type":"object","description":"file extension of the file","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"If suppressed is set to True, the policy is active, and the file will be skipped during scanning. If set to False, the policy is inactive, and the file will be considered for analysis."}]},{"name":".gguf","kind":"required","type":"object","description":"file extension of the file","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"If suppressed is set to True, the policy is active, and the file will be skipped during scanning. If set to False, the policy is inactive, and the file will be considered for analysis."}]},{"name":".h5","kind":"required","type":"object","description":"file extension of the file","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"If suppressed is set to True, the policy is active, and the file will be skipped during scanning. If set to False, the policy is inactive, and the file will be considered for analysis."}]},{"name":".keras","kind":"required","type":"object","description":"file extension of the file","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"If suppressed is set to True, the policy is active, and the file will be skipped during scanning. If set to False, the policy is inactive, and the file will be considered for analysis."}]},{"name":".onnx","kind":"required","type":"object","description":"file extension of the file","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"If suppressed is set to True, the policy is active, and the file will be skipped during scanning. If set to False, the policy is inactive, and the file will be considered for analysis."}]},{"name":".pb","kind":"required","type":"object","description":"file extension of the file","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"If suppressed is set to True, the policy is active, and the file will be skipped during scanning. If set to False, the policy is inactive, and the file will be considered for analysis."}]},{"name":".pkl","kind":"required","type":"object","description":"file extension of the file","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"If suppressed is set to True, the policy is active, and the file will be skipped during scanning. If set to False, the policy is inactive, and the file will be considered for analysis."}]},{"name":".pt","kind":"required","type":"object","description":"file extension of the file","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"If suppressed is set to True, the policy is active, and the file will be skipped during scanning. If set to False, the policy is inactive, and the file will be considered for analysis."}]},{"name":".pth","kind":"required","type":"object","description":"file extension of the file","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"If suppressed is set to True, the policy is active, and the file will be skipped during scanning. If set to False, the policy is inactive, and the file will be considered for analysis."}]},{"name":".safetensors","kind":"required","type":"object","description":"file extension of the file","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"If suppressed is set to True, the policy is active, and the file will be skipped during scanning. If set to False, the policy is inactive, and the file will be considered for analysis."}]},{"name":".zip","kind":"required","type":"object","description":"file extension of the file","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"If suppressed is set to True, the policy is active, and the file will be skipped during scanning. If set to False, the policy is inactive, and the file will be considered for analysis."}]}],"schema":[{"name":".bin","kind":"required","type":"object","description":"file extension of the file","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"If suppressed is set to True, the policy is active, and the file will be skipped during scanning. If set to False, the policy is inactive, and the file will be considered for analysis."}]},{"name":".ckpt","kind":"required","type":"object","description":"file extension of the file","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"If suppressed is set to True, the policy is active, and the file will be skipped during scanning. If set to False, the policy is inactive, and the file will be considered for analysis."}]},{"name":".gguf","kind":"required","type":"object","description":"file extension of the file","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"If suppressed is set to True, the policy is active, and the file will be skipped during scanning. If set to False, the policy is inactive, and the file will be considered for analysis."}]},{"name":".h5","kind":"required","type":"object","description":"file extension of the file","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"If suppressed is set to True, the policy is active, and the file will be skipped during scanning. If set to False, the policy is inactive, and the file will be considered for analysis."}]},{"name":".keras","kind":"required","type":"object","description":"file extension of the file","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"If suppressed is set to True, the policy is active, and the file will be skipped during scanning. If set to False, the policy is inactive, and the file will be considered for analysis."}]},{"name":".onnx","kind":"required","type":"object","description":"file extension of the file","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"If suppressed is set to True, the policy is active, and the file will be skipped during scanning. If set to False, the policy is inactive, and the file will be considered for analysis."}]},{"name":".pb","kind":"required","type":"object","description":"file extension of the file","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"If suppressed is set to True, the policy is active, and the file will be skipped during scanning. If set to False, the policy is inactive, and the file will be considered for analysis."}]},{"name":".pkl","kind":"required","type":"object","description":"file extension of the file","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"If suppressed is set to True, the policy is active, and the file will be skipped during scanning. If set to False, the policy is inactive, and the file will be considered for analysis."}]},{"name":".pt","kind":"required","type":"object","description":"file extension of the file","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"If suppressed is set to True, the policy is active, and the file will be skipped during scanning. If set to False, the policy is inactive, and the file will be considered for analysis."}]},{"name":".pth","kind":"required","type":"object","description":"file extension of the file","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"If suppressed is set to True, the policy is active, and the file will be skipped during scanning. If set to False, the policy is inactive, and the file will be considered for analysis."}]},{"name":".safetensors","kind":"required","type":"object","description":"file extension of the file","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"If suppressed is set to True, the policy is active, and the file will be skipped during scanning. If set to False, the policy is inactive, and the file will be considered for analysis."}]},{"name":".zip","kind":"required","type":"object","description":"file extension of the file","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"If suppressed is set to True, the policy is active, and the file will be skipped during scanning. If set to False, the policy is inactive, and the file will be considered for analysis."}]}]},{"name":"genai_framework_detection","kind":"required","type":"object","description":"Enables automatic identification of Generative AI-related libraries (e.g., transformers, openai, langchain) during source or dependency scanning.","":"required","children":[{"name":"enabled","kind":"required","type":"boolean","description":"If enabledis set to True, the policy is active, and the GenAI framework will be detected during scanning. If set to False, it will not be detected as GenAI framework."}],"schema":[{"name":"enabled","kind":"required","type":"boolean","description":"If enabledis set to True, the policy is active, and the GenAI framework will be detected during scanning. If set to False, it will not be detected as GenAI framework."}]},{"name":"report_generation","kind":"required","type":"object","description":"Controls whether a report is generated during the scan process.","":"required","children":[{"name":"pdf","kind":"required","type":"boolean","description":"If pdf=True, a PDF report will be generated after the scan; if pdf=False, no PDF report will be created."}],"schema":[{"name":"pdf","kind":"required","type":"boolean","description":"If pdf=True, a PDF report will be generated after the scan; if pdf=False, no PDF report will be created."}]},{"name":"scan_format_suppression","kind":"required","type":"object","description":"Allows selective suppression of specific scan formats like SAST (Static Application Security Testing) or SBOM/SCA (Software Bill of Materials/Software Composition Analysis).","":"Allows selective suppression of specific scan formats like SAST (Static Application Security Testing) or SBOM/SCA (Software Bill of Materials/Software Composition Analysis).","children":[{"name":"SAST","kind":"required","type":"object","description":"Static Application Security Testing","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"If suppressed is set to True, the policy is active. If set to False, the policy is inactive."}]},{"name":"SBOM/SCA","kind":"required","type":"object","description":"Software Bill of Materials/Software Composition Analysis","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"If suppressed is set to True, the policy is active. If set to False, the policy is inactive."}]}],"schema":[{"name":"SAST","kind":"required","type":"object","description":"Static Application Security Testing","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"If suppressed is set to True, the policy is active. If set to False, the policy is inactive."}]},{"name":"SBOM/SCA","kind":"required","type":"object","description":"Software Bill of Materials/Software Composition Analysis","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"If suppressed is set to True, the policy is active. If set to False, the policy is inactive."}]}]},{"name":"vulnerability_type","kind":"required","type":"object","description":"This section defines a configurable list of AI/ML model-related vulnerabilities, where each vulnerability can be suppressed or actively scanned based on the configuration.","":"required","children":[{"name":"AIS-BM-S-01","kind":"required","type":"object","description":"The AI-BOM indicates presence of packages with CVEs or other reported vulnerabilities.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-CP-D-01","kind":"required","type":"object","description":"A vulnerability in the deserialization of checkpoint files, which could lead to unintended code execution or model manipulation.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-GU-R-01","kind":"required","type":"object","description":"A runtime threat in GGUF files caused by malicious or improperly formatted data.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-GU-R-02","kind":"required","type":"object","description":"A vulnerability in the GGUF format with invalid or unreadable template. This is an indication of a potential file tampering.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-KR-B-01","kind":"required","type":"object","description":"A vulnerability in the keras model files indicating presence of potential backdoor / unsafe operations.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-KR-B-02","kind":"required","type":"object","description":"Non-standard Keras Layers are found in the Model - Potential backdoor.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-KR-D-01","kind":"required","type":"object","description":"A vulnerability in deserializing Keras model files, which might expose systems to malicious code.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-MI-D-01","kind":"required","type":"object","description":"A vulnerability in zip files that can introduce trojans or corrupted data into the system.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-ON-B-01","kind":"required","type":"object","description":"A backdoor vulnerability within ONNX model files, potentially allowing hidden operations to be triggered.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-ON-R-01","kind":"required","type":"object","description":"A runtime vulnerability caused by corrupted or manipulated ONNX files, leading to unexpected behavior.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-PK-D-01","kind":"required","type":"object","description":"A vulnerability in the deserialization of Pickle files, which could lead to arbitrary code execution if files are manipulated.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-PT-D-01","kind":"required","type":"object","description":"A vulnerability in the Pickle serialization of PyTorch models that could lead to code execution when loading malicious files.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-PT-D-02","kind":"required","type":"object","description":"A serialization vulnerability in PyTorch models, which may enable code execution or file manipulation.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-PY-S-01","kind":"required","type":"object","description":"Python scripts contain compromised components, libraries, and user secrets.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-ST-D-01","kind":"required","type":"object","description":"A vulnerability in SafeTensors files caused by improper file formatting, potentially leading to security breaches.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-ST-D-02","kind":"required","type":"object","description":"A vulnerability in SafeTensors file shards that allows malicious actors to exploit path traversal issues.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-TF-B-01","kind":"required","type":"object","description":"A backdoor in TensorFlow Protocol Buffers files, potentially allowing malicious actors to execute arbitrary commands.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-TF-B-02","kind":"required","type":"object","description":"A backdoor vulnerability in TensorFlow or Keras H5 files, introduced via malicious layers in the model.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-TF-B-03","kind":"required","type":"object","description":"Non standards Tensorflow/Keras layer was found - Potential backdoor.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-TF-D-01","kind":"required","type":"object","description":"A vulnerability in the deserialization of Protocol Buffers files, which could lead to code execution or data manipulation.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-TF-D-02","kind":"required","type":"object","description":"A vulnerability in the deserialization of TensorFlow or Keras H5 files, which may lead to malicious code execution or corruption.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-TF-R-01","kind":"required","type":"object","description":"A vulnerability in the Tensorflow/Keras file format - where an invalid magic number is detected in the file.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]}],"schema":[{"name":"AIS-BM-S-01","kind":"required","type":"object","description":"The AI-BOM indicates presence of packages with CVEs or other reported vulnerabilities.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-CP-D-01","kind":"required","type":"object","description":"A vulnerability in the deserialization of checkpoint files, which could lead to unintended code execution or model manipulation.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-GU-R-01","kind":"required","type":"object","description":"A runtime threat in GGUF files caused by malicious or improperly formatted data.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-GU-R-02","kind":"required","type":"object","description":"A vulnerability in the GGUF format with invalid or unreadable template. This is an indication of a potential file tampering.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-KR-B-01","kind":"required","type":"object","description":"A vulnerability in the keras model files indicating presence of potential backdoor / unsafe operations.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-KR-B-02","kind":"required","type":"object","description":"Non-standard Keras Layers are found in the Model - Potential backdoor.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-KR-D-01","kind":"required","type":"object","description":"A vulnerability in deserializing Keras model files, which might expose systems to malicious code.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-MI-D-01","kind":"required","type":"object","description":"A vulnerability in zip files that can introduce trojans or corrupted data into the system.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-ON-B-01","kind":"required","type":"object","description":"A backdoor vulnerability within ONNX model files, potentially allowing hidden operations to be triggered.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-ON-R-01","kind":"required","type":"object","description":"A runtime vulnerability caused by corrupted or manipulated ONNX files, leading to unexpected behavior.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-PK-D-01","kind":"required","type":"object","description":"A vulnerability in the deserialization of Pickle files, which could lead to arbitrary code execution if files are manipulated.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-PT-D-01","kind":"required","type":"object","description":"A vulnerability in the Pickle serialization of PyTorch models that could lead to code execution when loading malicious files.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-PT-D-02","kind":"required","type":"object","description":"A serialization vulnerability in PyTorch models, which may enable code execution or file manipulation.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-PY-S-01","kind":"required","type":"object","description":"Python scripts contain compromised components, libraries, and user secrets.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-ST-D-01","kind":"required","type":"object","description":"A vulnerability in SafeTensors files caused by improper file formatting, potentially leading to security breaches.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-ST-D-02","kind":"required","type":"object","description":"A vulnerability in SafeTensors file shards that allows malicious actors to exploit path traversal issues.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-TF-B-01","kind":"required","type":"object","description":"A backdoor in TensorFlow Protocol Buffers files, potentially allowing malicious actors to execute arbitrary commands.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-TF-B-02","kind":"required","type":"object","description":"A backdoor vulnerability in TensorFlow or Keras H5 files, introduced via malicious layers in the model.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-TF-B-03","kind":"required","type":"object","description":"Non standards Tensorflow/Keras layer was found - Potential backdoor.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-TF-D-01","kind":"required","type":"object","description":"A vulnerability in the deserialization of Protocol Buffers files, which could lead to code execution or data manipulation.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-TF-D-02","kind":"required","type":"object","description":"A vulnerability in the deserialization of TensorFlow or Keras H5 files, which may lead to malicious code execution or corruption.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]},{"name":"AIS-TF-R-01","kind":"required","type":"object","description":"A vulnerability in the Tensorflow/Keras file format - where an invalid magic number is detected in the file.","children":[{"name":"suppressed","kind":"required","type":"boolean","description":"Set to true to disable this vulnerability check, or false to enable it."},{"name":"custom_severity","kind":"optional","type":"string","description":"Allows you to define a custom severity level for the vulnerability id. If not provided, the system will automatically apply the default severity based on internal rules."},{"name":"customized_by_user","kind":"optional","type":"boolean","description":"Indicates whether the severity has been customized by the user. If true, the severity value was manually defined by the user. If false, the system-assigned default severity is used. This is system generated. "},{"name":"customized_severity_allowed","kind":"optional","type":"boolean","description":"Indicates whether custom severity mapping is allowed. If set to true, users can define their own severity levels using the custom_severity field. If false, only the system-defined default severity will be used. This is system generated. "}]}]},{"name":"tool_strictness","kind":"optional","type":"object","description":"The tool_strictness parameter defines the security level applied to different file types during analysis. It specifies how strictly the tool should assess and flag potential security risks based on the file format.","":"The tool_strictness parameter defines the security level applied to different file types during analysis. It specifies how strictly the tool should assess and flag potential security risks based on the file format.","children":[{"name":".pkl","kind":"optional","type":"object","description":"Specifies the security strictness level for Pickle (.pkl) files","children":[{"name":"level","kind":"optional","type":"string","description":"specifies the strictness level for .pkl files. options are 'low', 'medium' and 'high'"}]}],"schema":[{"name":".pkl","kind":"optional","type":"object","description":"Specifies the security strictness level for Pickle (.pkl) files","children":[{"name":"level","kind":"optional","type":"string","description":"specifies the strictness level for .pkl files. options are 'low', 'medium' and 'high'"}]}]}],"formDataParameters":[]},"currentNewParameter":{"label":"Body Parameter","value":"bodyDataParameters"},"hasTryItOut":true}"}
:::
[title] Introduction to AIShield
[path] /
[title] Supply Chain Lineage Check API
[path] API Documentation/AISpectra/Model Scanner/
The **Supply Chain Lineage Check API ** helps users determine whether a given **GitHub, Hugging Face, or S3 bucket repository ** has already been scanned. By providing the repository type and URL, users can verify its scan history, avoiding redundant security assessments and optimizing workflow efficiency.
**The following parameters are used for supply chain Lineage Check API. ** To learn more about different input parameters and how to use the API, refer to [AI/ML Supply Chain](docId\:Xso05kOq-um_Byw47J0UB) documentation.
:::ApiMethodV2{data="{"tab":"examples","url":"https://api.aws.boschaishield.com/prod/api/ais/v1.5/developer/lineage_check","name":"Supply Chain Lineage Check API","method":"POST","request":{"pathParameters":[],"queryParameters":[],"headerParameters":[{"kind":"required","name":"x-api-key","type":"string","children":[],"description":"Enter your API key"},{"kind":"required","name":"Org-Id","type":"string","description":"Enter your organization id","":"Org-Id"}],"bodyDataParameters":[{"name":"repo_type","kind":"required","type":"string","description":"The repository that needs to be scanned, such as github, huggingface and s3_bucket. ","":"The repository that needs to be scanned, such as github, huggingface and s3_bucket. "},{"name":"repo_url","kind":"optional","type":"string","description":"The URL of the repository that needs to be scanned. \n","":"The URL of the repository that needs to be scanned. \n"},{"name":"branch_name","kind":"optional","type":"string","description":"The branch of the repository to be scanned. Default is 'main' branch.","":"The branch of the repository to be scanned. Default is 'main' branch."},{"name":"depth","kind":"optional","type":"integer","description":"The depth of commits to scan from the repository. Default is 1, which clones only the latest commit.","":"integer"},{"name":"aws_access_key_id","kind":"optional","type":"string","description":"When repo_type is set to \"s3_bucket\", this parameter is mandatory.","":"When repo_type is set to \"s3_bucket\", this parameter is mandatory."},{"name":"aws_secret_access_key","kind":"optional","type":"string","description":"When repo_type is set to \"s3_bucket\", this parameter is mandatory.","":"When repo_type is set to \"s3_bucket\", this parameter is mandatory."},{"name":"region","kind":"optional","type":"string","description":"When repo_type is set to \"s3_bucket\", this parameter is mandatory. Povide region where s3_bucket is present. ","":"When repo_type is set to \"s3_bucket\", this parameter is mandatory. Povide region where s3_bucket is present. "},{"name":"bucket_name","kind":"optional","type":"string","description":"When repo_type is set to \"s3_bucket\", this parameter is mandatory. Provid the bucket name which need to be scanned. ","":"When repo_type is set to \"s3_bucket\", this parameter is mandatory. Provid the bucket name which need to be scanned. "}],"formDataParameters":[]},"results":{"languages":[{"id":"DL4HDcclTH6dUtOu-opbD","code":"// 200 OK: retuns dictionar which will contains the details of lineage details if found else empty.\n\n{\n \"BranchName\": \"xxxxx\",\n \"CommitID\": \"xxxxx\",\n \"CreatedTimestamp\": \"xxxxx\",\n \"Depth\": \"xxxxx\",\n \"HashedJobID\": \"xxxxx\",\n \"ModelID\": \"xxxxx\",\n \"OrgID\": \"xxxxx\",\n \"RepoType\": \"huggingface\",\n \"RepoURL\": \"https://huggingface.co/achilles1313/test_gguf\",\n \"SupplyChain_VulDetected\": 1\n} ","language":"200","customLabel":""},{"id":"z5dS_OPIMHsxFEwrtKnkw","language":"401","code":"// 401 Unauthorized: Returns an error message if the provided API key or Org-ID is invalid or expired.","customLabel":""},{"id":"xJHL9zR5wAZ30f4gu2BUz","language":"400","code":"// 400 Bad request Error: Returns an error message if the application cannot or will not process the request due to something that is perceived to be a client error (for example, malformed request syntax, invalid request message framing, etc.)","customLabel":""},{"id":"eXy7xHvpQ-HT16gZp2CNA","language":"412","code":"// 412 precondition failed: Returns an error message if access to the target resource has been denied. (For example- if any of the parameter value is incorrect or license has expired)","customLabel":""}],"selectedLanguageId":"DL4HDcclTH6dUtOu-opbD"},"examples":{"languages":[{"id":"t7-_cakecu--8GrYZbp4x","language":"python","code":"import requests\n\nurl = \"https://api.aws.boschaishield.com/prod/api/ais/v1.5/developer/lineage_check\"\n\npayload = \"{\\\"repo_type\\\":\\\"String\\\",\\\"repo_url\\\":\\\"String\\\",\\\"branch_name\\\":\\\"String\\\",\\\"depth\\\":\\\"Number\\\",\\\"aws_access_key_id\\\":\\\"String\\\",\\\"aws_secret_access_key\\\":\\\"String\\\",\\\"region\\\":\\\"String\\\",\\\"bucket_name\\\":\\\"String\\\"}\"\nheaders = {\n 'x-api-key': 'string',\n 'Org-Id': 'string'\n}\n\nresponse = requests.request(\"POST\", url, headers=headers, data=payload)\n\nprint(response.text)\n","customLabel":""},{"id":"1lTWvexG3MCRC17xAxNYM","language":"curl","code":"curl --location 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/developer/lineage_check' \\\n--header 'x-api-key: string' \\\n--header 'Org-Id: string' \\\n--data '{\"repo_type\":\"String\",\"repo_url\":\"String\",\"branch_name\":\"String\",\"depth\":\"Number\",\"aws_access_key_id\":\"String\",\"aws_secret_access_key\":\"String\",\"region\":\"String\",\"bucket_name\":\"String\"}'","customLabel":""},{"id":"UtN4X5XIV3PSAEnOdxY4X","language":"nodejs","code":"var request = require('request');\nvar options = {\n 'method': 'POST',\n 'url': 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/developer/lineage_check',\n 'headers': {\n 'x-api-key': 'string',\n 'Org-Id': 'string'\n },\n body: '{\"repo_type\":\"String\",\"repo_url\":\"String\",\"branch_name\":\"String\",\"depth\":\"Number\",\"aws_access_key_id\":\"String\",\"aws_secret_access_key\":\"String\",\"region\":\"String\",\"bucket_name\":\"String\"}'\n\n};\nrequest(options, function (error, response) {\n if (error) throw new Error(error);\n console.log(response.body);\n});\n","customLabel":""},{"id":"PxD52o8vC6LwamA5VrWfZ","language":"javascript","code":"var myHeaders = new Headers();\nmyHeaders.append(\"x-api-key\", \"string\");\nmyHeaders.append(\"Org-Id\", \"string\");\n\nvar raw = \"{\\\"repo_type\\\":\\\"String\\\",\\\"repo_url\\\":\\\"String\\\",\\\"branch_name\\\":\\\"String\\\",\\\"depth\\\":\\\"Number\\\",\\\"aws_access_key_id\\\":\\\"String\\\",\\\"aws_secret_access_key\\\":\\\"String\\\",\\\"region\\\":\\\"String\\\",\\\"bucket_name\\\":\\\"String\\\"}\";\n\nvar requestOptions = {\n method: 'POST',\n headers: myHeaders,\n body: raw,\n redirect: 'follow'\n};\n\nfetch(\"https://api.aws.boschaishield.com/prod/api/ais/v1.5/developer/lineage_check\", requestOptions)\n .then(response => response.text())\n .then(result => console.log(result))\n .catch(error => console.log('error', error));","customLabel":""},{"id":"OgFEtuMs8cg-eKHf3iqRa","language":"ruby","code":"require \"uri\"\nrequire \"net/http\"\n\nurl = URI(\"https://api.aws.boschaishield.com/prod/api/ais/v1.5/developer/lineage_check\")\n\nhttps = Net::HTTP.new(url.host, url.port)\nhttps.use_ssl = true\n\nrequest = Net::HTTP::Post.new(url)\nrequest[\"x-api-key\"] = \"string\"\nrequest[\"Org-Id\"] = \"string\"\nrequest.body = \"{\\\"repo_type\\\":\\\"String\\\",\\\"repo_url\\\":\\\"String\\\",\\\"branch_name\\\":\\\"String\\\",\\\"depth\\\":\\\"Number\\\",\\\"aws_access_key_id\\\":\\\"String\\\",\\\"aws_secret_access_key\\\":\\\"String\\\",\\\"region\\\":\\\"String\\\",\\\"bucket_name\\\":\\\"String\\\"}\"\n\nresponse = https.request(request)\nputs response.read_body\n","customLabel":""}],"selectedLanguageId":"t7-_cakecu--8GrYZbp4x"},"description":"The Supply Chain Lineage Check API verifies if a given GitHub, Hugging Face, or S3 repository has already been scanned for security assessment.","currentNewParameter":{"label":"Body Parameter","value":"bodyDataParameters"},"hasTryItOut":true}"}
:::
[title] Chat API
[path] API Documentation/Guardian/
:::ApiMethodV2{data="{"name":"Chat API","method":"POST","url":"{guardian_url}/chat","description":"\nThe Chat API processes user prompts according to the specified execution mode and returns a detailed response, including application metadata, guardrail configurations, token usage, and policy compliance checks.\n","tab":"examples","examples":{"languages":[{"id":"t-SM4oKeMx4zYLNrQASJg","language":"curl","code":"curl --location --globoff '{guardian_url}/chat/{app_name}' \\\n--header 'Accept: application/json' \\\n--header 'Content-Type: application/json' \\\n--data '{\"prompt\":\"String\"}'","customLabel":""},{"id":"z7KQwo0JQzBmzMPABsmUm","language":"python","code":"import requests\nimport json\n\nurl = \"{guardian_url}/chat/{app_name}\"\n\npayload = json.dumps({\n \"prompt\": \"String\"\n})\nheaders = {\n 'Accept': 'application/json',\n 'Content-Type': 'application/json'\n}\n\nresponse = requests.request(\"POST\", url, headers=headers, data=payload)\n\nprint(response.text)\n","customLabel":""},{"id":"kZAJp76oiHxQ7WatEvLr6","language":"java","code":"import java.io.OutputStream;\nimport java.io.InputStreamReader;\nimport java.io.BufferedReader;\nimport java.net.HttpURLConnection;\nimport java.net.URL;\n \npublic class ChatRequest {\n public static void main(String[] args) {\n try {\n \n String urlString = \"{guardian_url}/chat/{app_name}\";\n String jsonInputString = \"{\\\"prompt\\\": \\\"String\\\"}\";\n \n URL url = new URL(urlString);\n\n HttpURLConnection conn = (HttpURLConnection) url.openConnection();\n \n conn.setRequestMethod(\"POST\");\n conn.setRequestProperty(\"Accept\", \"application/json\");\n conn.setRequestProperty(\"Content-Type\", \"application/json\");\n conn.setDoOutput(true);\n \n \n try (OutputStream os = conn.getOutputStream()) {\n byte[] input = jsonInputString.getBytes(\"utf-8\");\n os.write(input, 0, input.length);\n }\n \n int code = conn.getResponseCode();\n try (BufferedReader br = new BufferedReader(new InputStreamReader(\n conn.getInputStream(), \"utf-8\"))) {\n StringBuilder response = new StringBuilder();\n String responseLine;\n while ((responseLine = br.readLine()) != null) {\n response.append(responseLine.trim());\n }\n System.out.println(\"Response Code: \" + code);\n System.out.println(\"Response: \" + response.toString());\n }\n \n conn.disconnect();\n \n } catch (Exception e) {\n e.printStackTrace();\n }\n }\n}","customLabel":""}],"selectedLanguageId":"kZAJp76oiHxQ7WatEvLr6"},"results":{"languages":[{"id":"2jq0G0qIzqScdM0FT1W9p","language":"200","customLabel":"","code":"{\n \"api_status_code\": 200,\n \"api_status_message\": \"Successful\",\n \"app_prompt\": \"user prompt\",\n \"app_prompt_context\": \"\",\n \"input\": {\n \"guardrails_metadata\": {\n \"configuration\": {input configuration dict},\n \"number_of_active_guardrails\": number of input active guardrails,\n \"number_of_inactive_guardrails\": number of input inactive guardrails\n },\n \"num_tokens\": number of input tokens,\n \"violated_policies\": \"comma separated violated policies\",\n \"latency/sec\": 0\n },\n \"llm_response\": \"Generated LLM response based on the user prompt.\",\n \"metadata\": {\n \"api_version\": \"v1.5\",\n \"app_name\": \"application name\",\n \"event_id\": \"unique id for the user prompt\",\n \"execution_mode\": \"Block\",\n \"timestamp\": \"timestamp user has been created\"\n },\n \"output\": {\n \"guardrails_metadata\": {\n \"configuration\": {output configuration dict},\n \"number_of_active_guardrails\": number of output active guardrails,\n \"number_of_inactive_guardrails\": number of output inactive guardrails\n },\n \"num_tokens\": number of output tokens,\n \"violated_policies\": \"comma separated violated policies\",\n \"latency/sec\": 0\n },\n \"redacted_prompt\": \"\",\n \"siem\": {\n \"active_siem\": [list of active siems],\n \"inactive_siem\": [list of inactive siems],\n \"status_code\": 200,\n \"status_message\": \"Successful\"\n },\n \"violation_exist\": false,\n \"violation_on\": \"input or output or empty string\"\n}"},{"id":"CgQLcKmIWE0qggwt3hc6Z","language":"401","code":"{\n \"api_status_code\": 401,\n \"api_status_message\": \"Access denied\",\n \"app_prompt\": \"user prompt\",\n \"app_prompt_context\": \"\",\n \"input\": {\n \"guardrails_metadata\": {\n \"configuration\": {},\n \"number_of_active_guardrails\": 0,\n \"number_of_inactive_guardrails\": 0\n },\n \"num_tokens\": 0,\n \"violated_policies\": \"\",\n \"latency/sec\": 0\n },\n \"llm_response\": \"\",\n \"metadata\": {\n \"api_version\": \"v1.5\",\n \"app_name\": \"application name\",\n \"event_id\": \"unique id for the user prompt\",\n \"execution_mode\": \"Block\",\n \"timestamp\": \"timestamp user has been created\"\n },\n \"output\": {\n \"guardrails_metadata\": {\n \"configuration\": {},\n \"number_of_active_guardrails\": 0,\n \"number_of_inactive_guardrails\": 0\n },\n \"num_tokens\": 0,\n \"violated_policies\": \"\",\n \"latency/sec\": 0\n },\n \"redacted_prompt\": \"\",\n \"siem\": {\n \"active_siem\": [],\n \"inactive_siem\": [],\n \"status_code\": null,\n \"status_message\": \"\"\n },\n \"violation_exist\": false,\n \"violation_on\": \"\"\n}","customLabel":""},{"id":"uE-6RDNKKHMTdT--_CBfJ","language":"429","code":"{\n \"api_status_code\": 429,\n \"api_status_message\": \"LLM Connectivity Issue\",\n \"app_prompt\": \"user prompt\",\n \"app_prompt_context\": \"\",\n \"input\": {\n \"guardrails_metadata\": {\n \"configuration\": {input configuration dict},\n \"number_of_active_guardrails\": number of input active guardrails,\n \"number_of_inactive_guardrails\": number of input inactive guardrails\n },\n \"num_tokens\": number of input tokens,\n \"violated_policies\": \"comma separated violated policies\",\n \"latency/sec\": 0\n },\n \"llm_response\": \"\",\n \"metadata\": {\n \"api_version\": \"v1.5\",\n \"app_name\": \"application name\",\n \"event_id\": \"unique id for the user prompt\",\n \"execution_mode\": \"Block\",\n \"timestamp\": \"timestamp user has been created\"\n },\n \"output\": {\n \"guardrails_metadata\": {\n \"configuration\": {},\n \"number_of_active_guardrails\": 0,\n \"number_of_inactive_guardrails\": 0\n },\n \"num_tokens\": 0,\n \"violated_policies\": \"\",\n \"latency/sec\": 0\n },\n \"redacted_prompt\": \"\",\n \"siem\": {\n \"active_siem\": [],\n \"inactive_siem\": [],\n \"status_code\": null,\n \"status_message\": \"\"\n },\n \"violation_exist\": false,\n \"violation_on\": \"\"\n}","customLabel":""},{"id":"Vpq7x5yrFNFRYClHEVio-","language":"500","code":"{\n \"api_status_code\": 500,\n \"api_status_message\": \"Internal Server Error\",\n \"app_prompt\": \"user prompt\",\n \"app_prompt_context\": \"\",\n \"input\": {\n \"guardrails_metadata\": {\n \"configuration\": {},\n \"number_of_active_guardrails\": 0,\n \"number_of_inactive_guardrails\": 0\n },\n \"num_tokens\": 0,\n \"violated_policies\": \"\",\n \"latency/sec\": 0\n },\n \"llm_response\": \"\",\n \"metadata\": {\n \"api_version\": \"v1.5\",\n \"app_name\": \"\",\n \"event_id\": \"\",\n \"execution_mode\": \"Block\",\n \"timestamp\": \"\"\n },\n \"output\": {\n \"guardrails_metadata\": {\n \"configuration\": {},\n \"number_of_active_guardrails\": 0,\n \"number_of_inactive_guardrails\": 0\n },\n \"num_tokens\": 0,\n \"violated_policies\": \"\",\n \"latency/sec\": 0\n },\n \"redacted_prompt\": \"\",\n \"siem\": {\n \"active_siem\": [],\n \"inactive_siem\": [],\n \"status_code\": null,\n \"status_message\": \"\"\n },\n \"violation_exist\": false,\n \"violation_on\": \"\"\n}","customLabel":""}],"selectedLanguageId":"2jq0G0qIzqScdM0FT1W9p"},"request":{"pathParameters":[{"name":"app_name","kind":"required","type":"String","description":"Specifies the application endpoint for inference. Possible values: app1, app2, app3.\n","children":[]}],"queryParameters":[],"headerParameters":[],"bodyDataParameters":[{"name":"prompt","kind":"required","type":"String","description":"The user's input or query to be processed by the API.\n"}],"formDataParameters":[]},"currentNewParameter":{"label":"Path Parameter","value":"pathParameters"},"response":[],"hasTryItOut":true}"}
:::
## **Response Field Definitions**:
The table below provides a comprehensive breakdown of all the fields included in the API response. It describes each field's purpose, type, and possible values to help you understand how to interpret the API's output effectively.
| **Field ** | **Type ** | **Description ** |
| --------------------- | ---------- | ---------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| `api_status_code` | integer | HTTP status code of the API response. Possible values: `200 `(Success), `401 `(Access Denied), `412 `(Precondition Failed), `500 `(Internal Server Error). |
| `api_status_message ` | string | Message indicating the status of the API call (e.g., "Successful", "LLM Connectivity Issue", "Internal Server Error", "Access Denied").
|
| `app_prompt ` | string | The user's application-specific prompt. |
| `app_prompt_context` | string | Context provided alongside the user's prompt. This field is currently an empty string. |
| `input ` | dictionary | Details about the input, including: |
| | | - `guardrails_metadata`: Input configuration, number of active and inactive guardrails. |
| | | * `num_tokens`: Number of tokens processed in the input. |
| | | - `violated_policies`: Policies violated, if any, or an empty string. |
| | | * `latency/sec`: given user's prompt processing time in sec |
| `output ` | dictionary | Details about the output, including: |
| | | - `guardrails_metadata`: output configuration, number of active and inactive guardrails. |
| | | * `num_tokens`: Number of tokens processed in the input. |
| | | - `violated_policies`: Policies violated, if any, or an empty string. |
| | | * `latency/sec`: llm response processing time in sec |
| `metadata ` | dictionary | Metadata about the API call, including: |
| | | - `api_version`: API version (e.g., v1.5). |
| | | * `app_name`: Application name |
| | | - `event_id`: Unique identifier for the API call. |
| | | * `execution_mode`: Mode of operation (e.g., Block). |
| | | - `timestamp`: Time of the API call in GMT. |
| `redacted_prompt ` | string | Sanitized or redacted version of the user prompt if PII Redaction is enabled, or an empty string otherwise. |
| `siem ` | dictionary | Security Information and Event Management (SIEM) details, including: |
| | | * `active_siem`: List of active SIEM systems. |
| | | - `inactive_siem`: List of inactive SIEM systems. |
| | | * `status_code`: Status code for SIEM processing. Possible values: `200 `(Success) , `500 `(Internal Server Error), `null `or `empty` is not needed to send message to siem |
| | | - `status_message`: Status message for SIEM processing.(e.g., "Successful", "Internal Server Error", empty string ). |
| `violation_exist` | boolean | Indicates if any policy violations occurred (`true `or `false`). |
| `violation_on` | string | Indicates whether the policy violation occurred due to the user's prompt (`input`) or the LLM response(`output`). |
## **Connecting to the Chat API:**
This below Gist provides a detailed example of how to connect to the Chat API, including how to structure the request, handle the response, and customize the API call based on your specific needs.
To get started with integrating the **Chat API**, you can refer to the following GitHub Gist for a step-by-step guide and example code:
::embed[]{url="https://gist.github.com/7fb4cfabca8ed7df3ad33674a9d8b32b.js"}
[title] Sample Attacks
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/Artifacts/
## Sample attack data
You can download the sample attack data used for model analysis, which is a randomly selected set of attack samples that were used during the testing phase to evaluate the performance of the model.
| Input type | Attack Samples |
| ----------------------- | ----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| Image classification | Extraction, Evasion, |
| Object Detection | Evasion |
| Tabular classification | Extraction, Evasion |
| Time series forecasting | Extraction Deep Learning |
| Text classification | Extraction |
| AudioSpeechRecognition | Evasion |
[title] IBM QRadar
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/Threat Informed Defense/Configuration of Connector/
### Prerequisite
- You have to get the AIShield AI Security Monitoring DSM for QRadar from IBM app exchnage to get started with below steps.
### Overview
AIShield is an AI-security product designed to protect AI-powered devices in the face of emerging security threats such as Model Extraction, Evasion, Data Poisoning, and Model Inference attacks. AIShield provides automated hacker-level vulnerability analysis and endpoint protection to harden the systems against emerging AI-security threats. AIShield provided Threat Informed Endpoint Defense (EDR) that integrates with IBM QRadar® SIEM to deliver enhanced real-time monitoring capabilities to security teams for their AI assets, giving them insights into AI security incidents.
IBM QRadar® provides a robust solution for Security Information and Event Management (SIEM), anomaly detection, incident forensics, and vulnerability management. This document provides the information to install and configure the AIShield DSM for QRadar®
App Content:
As of now (Version 1.0.0), the package includes the following items:
| Content Type | Contents |
| --------------------- | --------- |
| Log Source Type | 1 |
| Log Source Extension | 1 |
| QIDMAP | 5 |
| Custom Property Name | 2 |
| Custom Rule Event | 5 |
### Installation
**Pre-requisite for AIShield **
Users will have to leverage AIShield product to scan their AI model for vulnerabilities and generate Threat Informed Endpoint Defense (EDR) capable of integrating with IBM QRadar® SIEM.To complete this step, please get in touch with AIShield.Contact\@bosch.com The application installation requires access to the QRadar® console machine via a web interface.
The web interface can be accessed via https\://\<\>/.
**Pre-requisites for QRadar**
Version : QRadar® Version 7.3.3 or above
The installation processes as follows:
1\. Login to QRadar® console.

2\. Go to Admin → Extension Management.
3\. Download the AIShield AI Security Monitoring App for QRadar® v1.0.0 from IBM app exchange.

4\. Choose the downloaded zip file by clicking on Add.

5\. The QRadar® will prompt a list of changes being made by the app. Click on the install button.

6\. Thereafter, it will show a window that the App is installed successfully along with the DSM Event Mappings list.
7\. Clear cache and refresh the browser window after the app gets installed successfully.
# 3. App Configuration
**3.1 Create Log Source**
To create a log source in QRadar® (through Log Source Management app) for ingesting data from AIShield, perform following steps:
1\. Go to the Log Source Management App via the Admin Panel.

2\. A separate window will pop up. Click on + New Log Source button as shown below:
3\. Select Log Source type as “AIShield”.

4\. For receiving data sent through TCP/UDP protocol from AIShield Threat Informed defense model, select protocol
type as “HTTP Receiver”.

5\. In the section under Configure Log Source parameters, enter the name of the log
source, keep the log source enabled and Coalescing events checkbox disabled.

6\. In the section under Configure the protocol parameters, enter Log Source Identifier for
e.g. ‘AIShield’.
Note:-
i) The value of Log Source Identifier used in this step must also be used in “Log Source
Identifier” field while configuring AIShield QRadar® Plugin. Ensure that the correct value
is entered for the Log Source Identifier field, otherwise ingested events would not be
identified as AIShield events.

7\. Now click on the Skip Test and Finish button.
Now, Go to STEP 3.2 Deploy
**3.2 Deploy**
**Click on Deploy as shown below.**

2\. To collect events in QRadar®, Configure QRadar® http receiver endpoint.
For more information about this protocol, see HTTP Receiver protocol configuration options.
# 4. Configure an AIShield Threat informed defense(EDR) using the HTTP Receiver protocol
Collect events from AIShield Threat Informed Endpoint Defense (EDR) in QRadar® by using the HTTP Receiver protocol. Collect events by using the HTTP Receiver Protocol:
1. Configure your AIShield Threat Informed Endpoint Defense (EDR) to communicate with QRadar®. For more information, contact
2. Update QRadar® http receiver endpoint in defense\_model.py to send attack telemetry to QRadar®.
url = \>
3\. After successful receiving events via created Log source, the status of Log source will be OK.
4\. To confirm logs in QRadar® Go to log activity and see the result.(AIShield DSM will normalized these logs)
5\. We have configured Custome rule events to create offense based on the AI attack telemetry. Go to offense and see the list of Rules.

6\. This Custom event rules will match the criteria and creates offense related to AI security in QRadar®.

AIShield sample event messages
Use these sample event messages as a way of verifying a successful integration with QRadar®.
The following table provides a sample event message when you use the AIShield Threat Informed Endpoint Defense (EDR) for the AIShield DSM:
| **Event name ** | **Low-level category** | **Sample log** |
| ------------------------------------------------------------------------- | ----------------------- | ------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------ |
| AIShield - Image classification model extraction vulnerability detection | AI model extraction | \{
"RawMessage": "Image Classification AI Model Extraction Attack Identified",
"service\_name": "image\_classification\_extraction\_defense\_engine",
"asset\_id": "model-01",
"source\_name": "NA",
"probability": 0.9,
"attack\_name": "model\_attack",
"timestamp": "2021-12-03T00:50:23Z",
} |
| AIShield - Image classification model evasion vulnerability detection | AI model evasion | \{
"RawMessage": "Image Classification AI Model Evasion Attack Identified",
"service\_name": "image\_classification\_evasion\_defense\_engine",
"asset\_id": "model-01",
"source\_name": "NA",
"probability": 0.8,
"attack\_name": "model\_attack",
"timestamp": "2021-12-03T00:50:23Z",
} |
| AIShield - Tabular Classification AI Model Extraction Attack Identified | AI Model Extraction | \{
"RawMessage": "Tabular Classification AI Model Extraction Attack Identified",
"service\_name": "tabular\_classification\_extraction\_defense\_engine ",
"asset\_id": "model-02",
"source\_name": "NA",
"probability": 0.9,
"attack\_name": "model\_attack",
"timestamp": "2021-12-03T00:50:23Z",
} |
| AIShield -TimeSeries Forecasting AI Model Extraction Attack Identified | AI Model Extraction | \{
"RawMessage": "TimeSeries Forecasting AI Model Extraction Attack Identified",
"service\_name": "timeseries\_forecasting\_extraction\_defense\_engine",
"asset\_id": "model-02",
"source\_name": "NA",
"probability": 0.9,
"attack\_name": "model\_attack",
"timestamp": "2021-12-03T00:50:23Z"
} |
# 5. **Troubleshooting**
**Case #1 **– AIShield events are shown up as Unknown events
Problem:
AIShield events shown up as Unknown events.

Troubleshooting Steps:
1\. Go to Log Activity.
2\. Click on Add Filter. Select Parameter → Log Source Type\[Indexed], Operator → Equals
and Log Source → AIShield.
3\. Select ‘Last 7 Days’ in Views filter dropdown.
4\. If any events come as Unknown,
i) Right click on that particular event.
ii) View in DSM editor.
iii) Check the value of Event ID and Event Category under Log activity Preview.
iv) If Event ID and Event Category value come as unknown, Please contact AIShield support contact.(AIShield.contact\@in.bosch.com)
**Case #2 **– AIShield events are not ingesting in QRadar®
Problem:
AIShield events are not being ingested in QRadar®.
Troubleshooting Steps:
Make sure the port used to receive the event is open. Still if you are facing issue contact support.
# 6. Support
For help using the AIShield platform or the AIShield Threat Informed Endpoint Defense (EDR) App for IBM QRadar®, please contact the AIShield support.
You can also send an email to AIShield.contact\@in.bosch.com with questions about this.
[title] Defense Model
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/Artifacts/
You can download the defense model itself. It will include the following files:
> app.py
> app_log.py
> config.yaml
> defense_model.h5
> defense_model.onnx
> deployment.yaml
> docker-compose.yaml
> Dockerfile
> predict.py
> Readme.txt
- **app.py **: The core application logic for the defense model.
- **app\_log.py **: A logging module for effective monitoring.
- **config.yaml **: A configuration file for customizing the defense model settings.
- **defense\_model.h5 **: The defense model itself in HDF5 format.
- **defense\_model.onnx **: An alternative format of the defense model in ONNX.
- **deployment.yaml **: If you plan to deploy on Kubernetes, this configuration file is included.
- **docker-compose.yaml **: For Docker container deployment, this file is provided.
- **Dockerfile **: Required for building the Docker image.
- **predict.py **: A script to make predictions using the defense model.
- **Readme.txt **: Comprehensive documentation with instructions.
:::hint{type="info"}
You can view the sample vulnerbility dashboard to view all the artifacts.
:::
To see sample defense model for respective attack types, refer the below table.
| Input type | Defense model |
| ----------------------- | ------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| Image classification | Extraction, Evasion |
| Object Detection | Evasion |
| Tabular classification | Extraction, Evasion |
| Time series forecasting | Deep Learning Model |
Explore our detailed deployment guide at [Defense deployment](docId\:SW_Dnk8pIKzpfnreXkfPA) for step-by-step instructions on deploying the defense model.
[title] Generate Model ID
[path] API Documentation/AISpectra/Model Scanner/
The **Generate Model ID API** is used to create a **unique model ID** and generate a presigned URL for uploading a file. The model ID acts as an identifier for the Supply Chain Analysis when r**epo\_type is set to "file".**
:::ApiMethodV2{data="{"name":"generate_model_id","method":"POST","url":"https://api.aws.boschaishield.com/prod/api/ais/v1.5/generate_model_id","description":"This API generates a unique model ID and provides a presigned URL for uploading a model file, which is required for Supply Chain Analysis when repo_type=\"file\".","tab":"examples","examples":{"languages":[{"id":"frgapb2aD4_u5WQrU_rAS","language":"python","code":"import requests\n\nurl = \"https://api.aws.boschaishield.com/prod/api/ais/v1.5/generate_model_id\"\n\npayload = {}\nheaders = {\n 'x-api-key': 'string',\n 'Org-Id': 'string'\n}\n\nresponse = requests.request(\"POST\", url, headers=headers, data=payload)\n\nprint(response.text)\n","customLabel":""},{"id":"HWvu0IcWyYs9t1z8WWABJ","language":"curl","code":"curl --location --request POST 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/generate_model_id' \\\n--header 'x-api-key: string' \\\n--header 'Org-Id: string'","customLabel":""},{"id":"cgJ5_5dDTBZwDAuJTn5A9","language":"nodejs","code":"var request = require('request');\nvar options = {\n 'method': 'POST',\n 'url': 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/generate_model_id',\n 'headers': {\n 'x-api-key': 'string',\n 'Org-Id': 'string'\n }\n};\nrequest(options, function (error, response) {\n if (error) throw new Error(error);\n console.log(response.body);\n});\n","customLabel":""},{"id":"Zp0KHmgw1W3fWtEQB2FGN","language":"javascript","code":"var myHeaders = new Headers();\nmyHeaders.append(\"x-api-key\", \"string\");\nmyHeaders.append(\"Org-Id\", \"string\");\n\nvar requestOptions = {\n method: 'POST',\n headers: myHeaders,\n redirect: 'follow'\n};\n\nfetch(\"https://api.aws.boschaishield.com/prod/api/ais/v1.5/generate_model_id\", requestOptions)\n .then(response => response.text())\n .then(result => console.log(result))\n .catch(error => console.log('error', error));","customLabel":""},{"id":"Vj8db-_tfEQaZwm4gTamg","language":"ruby","code":"require \"uri\"\nrequire \"net/http\"\n\nurl = URI(\"https://api.aws.boschaishield.com/prod/api/ais/v1.5/generate_model_id\")\n\nhttps = Net::HTTP.new(url.host, url.port)\nhttps.use_ssl = true\n\nrequest = Net::HTTP::Post.new(url)\nrequest[\"x-api-key\"] = \"string\"\nrequest[\"Org-Id\"] = \"string\"\n\nresponse = https.request(request)\nputs response.read_body\n","customLabel":""}],"selectedLanguageId":"frgapb2aD4_u5WQrU_rAS"},"results":{"languages":[{"id":"N1fpC35SZxbcEWxck2pSW","language":"200","customLabel":"","code":"{\n \"api_version\": \"1.5\",\n \"artifact_path\": {\n \"fields\": {\n \"key\": \"xxxxx\",\n \"policy\": \"xxxxx\",\n \"x-amz-algorithm\": \"xxxxx\",\n \"x-amz-credential\": \"xxxxx\",\n \"x-amz-date\": \"xxxxx\",\n \"x-amz-signature\": \"xxxxx\"\n },\n \"url\": \"xxxxx\"\n },\n \"model_id\": \"xxxxx\"\n}"},{"id":"HoRypJvdzSbrZlIR1DsHs","language":"401","code":"// 401 Unauthorized: Returns an error message if the provided API key or Org-ID is invalid or expired.","customLabel":""},{"id":"iDVOSM2kLZnuhseONktcg","language":"400","customLabel":"","code":"// 400 Bad request Error: Returns an error message if the application cannot or will not process the request due to something that is perceived to be a client error (for example, malformed request syntax, invalid request message framing, etc.)"},{"id":"FxGZoAFylQRraTE0xU1u7","language":"412","code":"// 412 precondition failed: Returns an error message if access to the target resource has been denied. (For example- if any of the parameter value is incorrect or license has expired)","customLabel":""}],"selectedLanguageId":"N1fpC35SZxbcEWxck2pSW"},"request":{"pathParameters":[],"queryParameters":[],"headerParameters":[{"name":"x-api-key","kind":"required","type":"string","description":"Enter your API key","":"Enter your API key"},{"name":"Org-Id","kind":"required","type":"string","description":"Enter your organization id","":"Enter your organization id"}],"bodyDataParameters":[],"formDataParameters":[]},"currentNewParameter":{"label":"Header Parameter","value":"headerParameters"},"hasTryItOut":true}"}
:::
[title] ConfigureApp API
[path] API Documentation/Guardian/
:::hint{type="info"}
The payload below defines the configurable policy that a user can apply to validate the corresponding prompt/ response.
To apply the policy:
- **Copy and replace the appropriate policy** object in the `request JSON payload` as shown below.
- Select the correct policy configuration schema based on execution Mode `"block"` or `"audit"`** **also** **depending on the environment where the container is deployed `"cpu"` or `"gpu"`
- **"Audit Mode**"works **with out LLM Orchestration** and "**Block Mode"** works **with LLM Orchestration** .
Note: This policy is fully customizable and can be modified to reflect the desired behavior of your application or integration.
:::
:::CodeblockTabs
Audit-CPU
```json
{
"config_language": "en",
"config_llm": "",
"image_analysis_type": "",
"input_config": {
"JSON": {
"enabled": false
},
"Block Competitor": {
"comparison": "contains",
"value": ""
},
"Block Substring": {
"comparison": "contains",
"value": ""
},
"Allowed List": {
"comparison": "contains",
"value": ""
},
"Regex": {
"value": ""
},
"URL Detection": {
"enabled": false
},
"Code Detection": {
"enabled": false
},
"Ban Topic": {
"value": "",
"threshold": "high",
"custom_threshold": 0
},
"BCI Detection": {
"enabled": false,
"custom_model_available": false,
"mode": "default",
"threshold": "High",
"custom_threshold": 0
},
"Toxicity": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0.80
},
"Generic Harm": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0
},
"PII Detection": {
"enabled": false,
"redaction": false
},
"Special PII Detection": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0
},
"Prompt Injection / Jailbreaks": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0
},
"Secrets": {
"enabled": false
},
"Not Safe For Work": {
"enabled": false,
"threshold": "low",
"custom_threshold": 0
},
"Gender Sensitive": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0
},
"Token Limit": {
"value": "4096"
},
"Input Rate Limiter": {
"value": "10"
},
"Invisible Text": {
"enabled": false
},
"Medical Safety Detection": {
"enabled": false,
"threshold": "low",
"custom_threshold": 0.85
},
"No LLM Output": {
"enabled": false
},
"Malicious URL Detection": {
"enabled": false
},
"URL Reachability": {
"enabled": false
},
"Sentiment": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0
}
},
"output_config": {}
}
```
Audit-GPU
```json
{
"config_language": "en",
"config_llm": "",
"image_analysis_type": "",
"input_config": {
"JSON": {
"enabled": false
},
"Block Competitor": {
"comparison": "contains",
"value": ""
},
"Block Substring": {
"comparison": "contains",
"value": ""
},
"Allowed List": {
"comparison": "contains",
"value": ""
},
"Regex": {
"value": ""
},
"URL Detection": {
"enabled": false
},
"Code Detection": {
"enabled": false
},
"Ban Topic": {
"value": "",
"threshold": "high",
"custom_threshold": 0
},
"BCI Detection": {
"enabled": false,
"custom_model_available": false,
"mode": "default",
"threshold": "High",
"custom_threshold": 0
},
"Toxicity": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0.80
},
"Generic Harm": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0
},
"PII Detection": {
"enabled": false,
"redaction": false
},
"Special PII Detection": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0
},
"Prompt Injection / Jailbreaks": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0
},
"Secrets": {
"enabled": false
},
"Not Safe For Work": {
"enabled": false,
"threshold": "low",
"custom_threshold": 0
},
"Gender Sensitive": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0
},
"Token Limit": {
"value": "4096"
},
"Input Rate Limiter": {
"value": "10"
},
"Invisible Text": {
"enabled": false
},
"Medical Safety Detection": {
"enabled": false,
"threshold": "low",
"custom_threshold": 0.85
},
"No LLM Output": {
"enabled": false
},
"Malicious URL Detection": {
"enabled": false
},
"URL Reachability": {
"enabled": false
},
"Sentiment": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0
},
"Contextual Groundedness": {"enabled": true},
"Answer Relevance": {"enabled": true}
},
"output_config": {}
}
```
Block-CPU
```json
{
"config_language": "en",
"config_llm": "Mistral",
"image_analysis_type": "",
"input_config": {
"JSON": {
"enabled": false
},
"Block Competitor": {
"comparison": "contains",
"value": ""
},
"Block Substring": {
"comparison": "contains",
"value": ""
},
"Allowed List": {
"comparison": "contains",
"value": ""
},
"Regex": {
"value": ""
},
"URL Detection": {
"enabled": false
},
"Code Detection": {
"enabled": false
},
"Ban Topic": {
"value": "",
"threshold": "high",
"custom_threshold": 0
},
"BCI Detection": {
"enabled": false,
"custom_model_available": false,
"mode": "default",
"threshold": "High",
"custom_threshold": 0
},
"Toxicity": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0.80
},
"Generic Harm": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0
},
"PII Detection": {
"enabled": false,
"redaction": false
},
"Special PII Detection": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0
},
"Prompt Injection / Jailbreaks": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0
},
"Secrets": {
"enabled": false
},
"Not Safe For Work": {
"enabled": false,
"threshold": "low",
"custom_threshold": 0
},
"Gender Sensitive": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0
},
"Token Limit": {
"value": "4096"
},
"Input Rate Limiter": {
"value": "10"
},
"Invisible Text": {
"enabled": false
},
"Medical Safety Detection": {
"enabled": false,
"threshold": "low",
"custom_threshold": 0.85
}
},
"output_config": {
"JSON": {
"enabled": false
},
"Block Competitor": {
"comparison": "contains",
"value": ""
},
"Block Substring": {
"comparison": "contains",
"value": ""
},
"Allowed List": {
"comparison": "contains",
"value": ""
},
"Blocked List": {
"comparison": "contains",
"value": ""
},
"Regex": {
"value": ""
},
"URL Detection": {
"enabled": false
},
"Code Detection": {
"enabled": false
},
"No LLM Output": {
"enabled": false
},
"Malicious URL Detection": {
"enabled": false
},
"URL Reachability": {
"enabled": false
},
"Ban Topic": {
"value": "",
"threshold": "High",
"custom_threshold": 0
},
"BCI Detection": {
"enabled": false,
"custom_model_available": false,
"mode": "default",
"threshold": "High",
"custom_threshold": 0
},
"Toxicity": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0
},
"Generic Harm": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0
},
"Sentiment": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0
},
"PII Detection": {
"enabled": false,
"redaction": false
},
"Special PII Detection": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0
},
"Secrets": {
"enabled": false
},
"Not Safe For Work": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0
},
"Gender Sensitive": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0
},
"Medical Safety Detection": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0
}
}
}
```
Block-GPU
```json
{
"config_language": "en",
"config_llm": "Mistral",
"image_analysis_type": "",
"input_config": {
"JSON": {
"enabled": false
},
"Block Competitor": {
"comparison": "contains",
"value": ""
},
"Block Substring": {
"comparison": "contains",
"value": ""
},
"Allowed List": {
"comparison": "contains",
"value": ""
},
"Regex": {
"value": ""
},
"URL Detection": {
"enabled": false
},
"Code Detection": {
"enabled": false
},
"Ban Topic": {
"value": "",
"threshold": "high",
"custom_threshold": 0
},
"BCI Detection": {
"enabled": false,
"custom_model_available": false,
"mode": "default",
"threshold": "High",
"custom_threshold": 0
},
"Toxicity": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0.80
},
"Generic Harm": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0
},
"PII Detection": {
"enabled": false,
"redaction": false
},
"Special PII Detection": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0
},
"Prompt Injection / Jailbreaks": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0
},
"Secrets": {
"enabled": false
},
"Not Safe For Work": {
"enabled": false,
"threshold": "low",
"custom_threshold": 0
},
"Gender Sensitive": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0
},
"Token Limit": {
"value": "4096"
},
"Input Rate Limiter": {
"value": "10"
},
"Invisible Text": {
"enabled": false
},
"Medical Safety Detection": {
"enabled": false,
"threshold": "low",
"custom_threshold": 0.85
}
},
"output_config": {
"JSON": {
"enabled": false
},
"Block Competitor": {
"comparison": "contains",
"value": ""
},
"Block Substring": {
"comparison": "contains",
"value": ""
},
"Allowed List": {
"comparison": "contains",
"value": ""
},
"Blocked List": {
"comparison": "contains",
"value": ""
},
"Regex": {
"value": ""
},
"URL Detection": {
"enabled": false
},
"Code Detection": {
"enabled": false
},
"No LLM Output": {
"enabled": false
},
"Malicious URL Detection": {
"enabled": false
},
"URL Reachability": {
"enabled": false
},
"Ban Topic": {
"value": "",
"threshold": "High",
"custom_threshold": 0
},
"BCI Detection": {
"enabled": false,
"custom_model_available": false,
"mode": "default",
"threshold": "High",
"custom_threshold": 0
},
"Toxicity": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0
},
"Generic Harm": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0
},
"Sentiment": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0
},
"PII Detection": {
"enabled": false,
"redaction": false
},
"Special PII Detection": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0
},
"Secrets": {
"enabled": false
},
"Not Safe For Work": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0
},
"Gender Sensitive": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0
},
"Medical Safety Detection": {
"enabled": false,
"threshold": "High",
"custom_threshold": 0
},,
"Contextual Groundedness": {"enabled": true},
"Answer Relevance": {"enabled": true}
}
}
```
:::
:::hint{type="info"}
#
# 🛡️ Confidence Thresholds in Guardian :
Guardian uses a confidence thresholds to decide when to flag a user query / model response as potentially unsafe/risk. These thresholds control how cautious or relaxed the system is when making that decision.You can choose between four modes: **High**, **Medium**, **Low**(default), and **Custom **— each offering a different balance between precision and coverage.
### 🔵 ***High Threshold:***
In this mode, **Guardian will only flag **when it is **very confident **that a user query / response **violates a defined boundary**.This results in a **low false positive rate **— meaning very few things will be flagged incorrectly. However, it may miss some actual violation that don’t meet the high confidence level. This setting is ideal when you want to avoid unnecessary disruptions or over-flagging, especially in low-risk.
### 🟡 ***Medium Threshold:***
With the **medium threshold**, Guardian takes a **balanced approach**. It flags content when it's **reasonably confident** that there may be a **potential policy issue or risk**. You may see a **moderate false positive rate**, but it also reduces the chances of missing real violations. This is a good default choice for most general-purpose use cases where you want a balance between accuracy and coverage.
### 🔴 ***Low Threshold :***
The **low threshold **setting is the **most sensitive**. Guardian will flag responses even if it has only a **moderate level of confidence** that something **might violate policy**. This ensures that almost no actual issues go undetected, but it also increases the **false positive rate** — meaning more content might be flagged unnecessarily. It’s best suited for high-sensitivity environments where **missing a potential violation is riskier than flagging extra content**.
### ⚙️ ***Custom Threshold:***
If your use case requires more precise control, you can set a **custom threshold **between 0 and 1. Lower values make Guardian more aggressive in flagging (higher sensitivity), while higher values make it more conservative (flagging less frequently). This mode is ideal when you have specific business rules, risk tolerance levels, or workflows that need fine-tuning.
By adjusting the confidence threshold, you’re effectively choosing how cautious Guardian should be — whether it should only flag highly certain violations or proactively surface anything that might require attention.
:::
:::ApiMethodV2{data="{"name":"configureApp API","method":"POST","url":"{guardian_url}/configureApp","description":"","tab":"examples","examples":{"languages":[{"id":"WAlGLJZwnH0SxzEstoB_5","language":"curl","code":"curl --location --globoff '{guardian_url}/configureApp/{app_name}' \\\n--header 'Accept: application/json' \\\n--header 'Content-Type: application/json' \\\n--data '<>'","customLabel":""},{"id":"KoINKM-as8FbUfKLQhh9Z","language":"python","code":"import requests\nimport json\n\nurl = \"{guardian_url}/configureApp/{app_name}\"\n\n# please copy the request payload according to given mode and device type\npayload = {# <>}\nheaders = {\n 'Accept': 'application/json',\n 'Content-Type': 'application/json'\n}\n\nresponse = requests.request(\"POST\", url, headers=headers, data=json.dumps(payload))\n\nprint(response.text)\n","customLabel":""}],"selectedLanguageId":"KoINKM-as8FbUfKLQhh9Z"},"results":{"languages":[{"id":"PcsA3MK1cJSGUnwvSbN63","language":"200","customLabel":"","code":"{\n \"status\": true,\n \"error_message\": \"\",\n \"validation_status\": {\"input\": {}, \"output\": {}}\n}"},{"id":"5SnpzE5I-TlGzeN3a8gLZ","language":"400","code":"{\n \"status\": true,\n \"error_message\": \"Invalid configuration: Input features cannot be assigned or updated as output features, and vice versa.\",\n \"validation_status\": {\"input\": {features with the output tagging wrongly getting update}, \"output\": {features with the input tagging wrongly getting update}}\n}","customLabel":""},{"id":"F4x1fjQ36O_LgucDXy2SK","language":"500","code":"{\n \"status\": false,\n \"error_message\": \"Internal Server Error\",\n \"validation_status\": {\"input\": {}, \"output\": {}}\n}","customLabel":""}],"selectedLanguageId":"F4x1fjQ36O_LgucDXy2SK"},"request":{"pathParameters":[{"name":"app_name","kind":"required","type":"string","description":"Specifies the application endpoint for updating the configuration. Possible values: app1, app2, app3, app4\n","children":[]}],"queryParameters":[],"headerParameters":[],"bodyDataParameters":[],"formDataParameters":[]},"currentNewParameter":{"label":"Body Parameter","value":"bodyDataParameters"},"hasTryItOut":false}"}
:::
## **Request Body Definitions**
The table below provides a **detailed breakdown** of all fields included in the API request body. It describes each field's **purpose, type, and possible values** to help you configure the API effectively with examples.
| **Field** | **Type** | **Description** |
| ----------------------- | -------- | ----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| `config_language`
| String | Specifies the languages that the system supports for user interaction. Can be English (default value) or English & Korean both.
by default `"en"`, possible values `"en,ko"` |
| `config_llm`
| String | Defines the configured Language Model (LLM) to be used.
* supported LLMs for **app1/aap2/app3** are : `"OpenAI"`,` "Mistral"`, `"Gemini"`,` "ChatGPT"`
* supported LLMs for **app4 **: `"Claude"` |
| `image_analysis_type ` | String | Supported Image Analysis types like OCR or Content Moderation.
* Not required for app1/aap2/app3 , provide empty string e.g: `""`
* required only for **app4 **configuration update. possible values are : `"ocr"`, `"image_content_moderation"`
|
| **Theme** | **Policy** | **Description** | **Key** | **Type** | **Possible Values** |
| ------------------------------------------ | ------------------------------- | -------------------------------------------------------------------------------------------- | ------------------------ | ------------ | --------------------------------------------------------------------------------------------------------------------- |
| Additional Checks | `JSON` | Ensures correctness and validates JSON format | enabled | Boolean | true / false |
| Content Access Control | `Block Competitor` | Blocks mentions of competitors | value | String | comma-separated string |
| | | | comparison | String | "exact\_match" / "contains" |
| Content Access Control | `Block Substring` | Blocks specific strings of text | value | String | comma-separated string |
| | | | comparison | String | "exact\_match" / "contains" |
| Content Access Control | `Ban Topic` | Blocks entire topics of discussion | value | String | comma-separated string |
| | | | threshold | String | "Low" / "Medium" / "High" / "Custom" |
| | | | custom\_threshold | Float | If threshold is set to "custom", provide a custom\_threshold value in the range of Float (0.0 to 1.0), default is 0.0 |
| Content Access Control | `Allowed List` | Permits only approved content | value | String | comma-separated string |
| | | | comparison | String | "exact\_match" / "contains" |
| Content Access Control | `Blocked List` | Prevents output of certain block listed content | value | String | comma-separated string |
| | | | comparison | String | "exact\_match" / "contains" |
| Content Analysis | `Regex` | Uses patterns to match text/alphanumeric for filtering | value | String | single regex pattern |
| Content Safety | `URL Detection` | Identifies URLs in prompt | enabled | Boolean | true/false |
| Security Measures | `Code Detection` | Identifies programming code in text (C, C++, HTML, Bash, JAVA, JavaScript, Python, C#, JSON) | enabled | Boolean | true/false |
| Content Safety | `Toxicity` | Filters toxic and harmful language in input or in prompt's response | enabled | Boolean | true/false |
| | | | threshold | String | "Low" / "Medium" / "High" / "Custom" |
| | | | custom\_threshold | Float | If threshold is set to "custom", provide a custom\_threshold value in the range of Float (0.0 to 1.0), default is 0.0 |
| Content Safety | `Generic Harm` | Blocks swear words and vulgar language (supports English language) | enabled | Boolean | true/false |
| | | | threshold | String | "Low" / "Medium" / "High" / "Custom" |
| | | | custom\_threshold | Float
| If threshold is set to "custom", provide a custom\_threshold value in the range of Float (0.0 to 1.0), default is 0.0 |
| Privacy Protection | `PII Detection` | Detects personal identifiable information (e.g., Full name, email address, phone number) | enabled | Boolean | true/false |
| | | | redaction | Boolean | true/false |
| Content Validation | `No LLM Ouput` | Underlying LLM refuses to provide an answer | enabled | Boolean | true/false |
| Content Validation | `Contextual Groundedness` | Checks if the response aligns with the provided Context | enabled | Boolean | true/false |
| Content Validation | `Answer Relevance` | Checks the relevance between the provided query and response | enabled | Boolean | true/false |
| Security Measures | `Special PII Detection` | Detects specialized personal information | enabled | Boolean | true/false |
| | | | threshold | String | "Low" / "Medium" / "High" / "Custom" |
| | | | custom\_threshold | Float | If threshold is set to "custom", provide a custom\_threshold value in the range of Float (0.0 to 1.0), default is 0.0 |
| Content Safety | `Sentiment` | Analyzes the sentiment of AI responses (positive, negative, or neutral) | enabled | Boolean | true/false |
| | | | threshold | String | "Low" / "Medium" / "High" / "Custom" |
| | | | custom\_threshold | Float | If threshold is set to "custom", provide a custom\_threshold value in the range of Float (0.0 to 1.0), default is 0.0 |
| Security Measures | `Prompt Injection / Jailbreaks` | Detects attempts to manipulate the AI | enabled | Boolean | true/false |
| | | | threshold | String | "Low" / "Medium" / "High" / "Custom" |
| | | | custom\_threshold | Float | If threshold is set to "custom", provide a custom\_threshold value in the range of Float (0.0 to 1.0), default is 0.0 |
| Security Measures | `Secrets` | Detects and redacts sensitive information (AWS Secrets, Git Secrets, DB Secrets) | enabled | Boolean | true/false |
| Security Measures | `Malicious URL Detection` | Scans for harmful URLs in output | enabled | Boolean | true/false |
| Additional Checks | `URL Reachability` | Checks if URLs in output are accessible | enabled | Boolean | true/false |
| Content Safety | `Not Safe For Work` | Filters sexually explicit or inappropriate material | enabled | Boolean | true/false |
| | | | threshold | String | "Low" / "Medium" / "High" / "Custom" |
| | | | custom\_threshold | Float | If threshold is set to "custom", provide a custom\_threshold value in the range of Float (0.0 to 1.0), default is 0.0 |
| Content Safety
| `Medical Safety Detection` | Detects Medically Unsafe information
| enabled | Boolean | true/false |
| | | | threshold | String | "Low" / "Medium" / "High" / "Custom" |
| | | | custom\_threshold | Float | If threshold is set to "custom", provide a custom\_threshold value in the range of Float (0.0 to 1.0), default is 0.0 |
| Content Safety
| `Gender Sensitive` | Identifies Gender discrimination, bias, and stereotype
| enabled | Boolean | true/false |
| | | | threshold | String | "Low" / "Medium" / "High" / "Custom" |
| | | | custom\_threshold | Float | If threshold is set to "custom", provide a custom\_threshold value in the range of Float (0.0 to 1.0), default is 0.0 |
| Security Integrity Checks
| `Invisible Text` | Identifies hidden text within inputs
| enabled | Boolean | true/false |
| Usage Management
| `Input Rate Limiter` | Limits the rate of input to the system
| value | Integer | Integer |
| Usage Management
| `Token Limit` | Sets limits on token usage in requests
| value | Integer | Integer (max 4096) |
| Privacy Protection
| `BCI Detection` | Detects business confidential information
| enabled | Boolean | true/false |
| | | | custom\_model\_available | Boolean | by default false, once custom model will upload then can set as true |
| | | | mode | String | "default" / "custom" |
| | | | threshold | String | "Low" / "Medium" / "High" / "Custom" |
| | | | custom\_threshold | Float | If threshold is set to "custom", provide a custom\_threshold value in the range of Float (0.0 to 1.0), default is 0.0 |
:::hint{type="info"}
# 🧠 **Hallucination Detection:**
- Hallucination detection can be checked by enabling the policies like: **Contextual Groundedness** and **Answer Relevance** . These checks enable precise validation of model responses against a supplied context or prompt, prompt or model's response, helping ensure factual consistency and response integrity.
- This capability is available **only on GPU-enabled environments**.
### Feature Overview:
- **Contextual Groundedness Check**
Verifies that the model’s response is logically and semantically grounded in the provided context (context and response are required fields for audit mode and only context is required field for block mode). It identifies instances where the response introduces unsupported or fabricated information.
- **Answer Relevance Check**
Assesses whether the response meaningfully answers the original user query (response is required fields for audit mode and in block mode response will be taken care by querying the respective llm)and stays within the scope of the provided question.
## ⚙️ *How to Use:*
To activate hallucination checks, structure your payload using the following tags:
***1. Formatting for Context:***
> ``
>
>
> \[Insert source context here]
>
>
> ****
***2. Formatting for LLM/Model response:***
> ****
>
>
> \[Insert LLM/Model response here]
>
>
> ****
***3. Formatting for Prompt:***
🚫 Do **not **include any tags in the prompt. Only the **context** and **response **must be tagged.
## 📘* ****Examples:***
Audit Mode:****
> """Where was Albert Einstein born, and what is he known for?
>
>
>
> ``
>
>
> Albert Einstein was born in Ulm, Germany in 1879. He developed the theory of relativity, one of the two pillars of modern physics.
>
>
> ` `
>
>
> Albert Einstein was born in Vienna in 1881 and is best known for his work on quantum mechanics.
>
>
> `
> """
>
> **
> **
Block Mode:
In Block Mode, only the **context** tag is required.
> """Where was Albert Einstein born, and what is he known for?
>
>
>
> ``
>
>
> Albert Einstein was born in Ulm, Germany in 1879. He developed the theory of relativity, one of the two pillars of modern physics.
>
>
> ``
>
> """
:::
[title] Image Classification
[path] API Documentation/AISpectra/Automated RedTeaming for AI/ML/ Model Analysis/Image/
The below parameters are for various image classification attack types. To know more about the different attack input parameters see [Image Classification](docId:6DEIiMJnkL5D0cdWSTCKb).
:::hint{type="info"}
The values presented below are examples taken from the MNIST model used in the reference implementation. It is important to customize these values to achieve the best performance for your particular model.
:::
:::CodeblockTabs
Extraction
```json
{
"attack_type": "blackbox",
"defense_bestonly": "no",
"encryption_strategy": "0",
"input_dimensions": "28,28,1",
"model_api_details": "na",
"model_framework": "tensorflow",
"normalize_data": "yes",
"number_of_attack_queries": "10000",
"number_of_classes": "10",
"use_model_api": "no",
"vulnerability_threshold": "0.00",
"color_space": "bgr"
}
```
Evasion
```json
{
"defense_bestonly": "no",
"encryption_strategy": "0",
"input_dimensions": "28,28,1",
"model_api_details": "na",
"model_framework": "tensorflow",
"normalize_data": "yes",
"number_of_classes": "10",
"use_model_api": "no",
"color_space": "bgr"
}
```
Poisoning
```json
{
"input_dimensions": "28,28,1",
"model_framework": "tensorflow",
"normalize_data": "yes",
"number_of_classes": "10",
"color_space": "bgr"
}
```
Drift
```json
{
"color_space" : "bgr",
"encryption_strategy": "0",
"input_dimensions": "128,128,3",
"model_api_details": "na",
"model_framework": "tensorflow",
"use_model_api": "no",
"color_space": "bgr"
}
```
Outlier
```json
{
"input_dimensions": "128,128,3"
}
```
:::
:::ApiMethodV2{data="{"tab":"examples","url":"https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse","name":"Model anaylsis","method":"POST","request":{"pathParameters":[{"name":"model_id","kind":"required","type":"string","description":"","children":[]}],"queryParameters":[],"headerParameters":[{"kind":"required","name":"x-api-key","type":"string","children":[],"description":"Enter your API key"},{"kind":"required","name":"Org-id","type":"string","children":[],"description":"Enter your organization id"}],"bodyDataParameters":[],"formDataParameters":[]},"results":{"languages":[{"id":"DL4HDcclTH6dUtOu-opbD","code":"// 200 OK: Returns a JSON object containing unique model ID and urls to upload required files.","language":"200","customLabel":""},{"id":"z5dS_OPIMHsxFEwrtKnkw","language":"401","code":"// 401 Unauthorized: Returns an error message if the provided API key or Org-ID is invalid or expired.","customLabel":""},{"id":"xJHL9zR5wAZ30f4gu2BUz","language":"400","code":"// 400 Bad request Error: Returns an error message if the application cannot or will not process the request due to something that is perceived to be a client error (for example, malformed request syntax, invalid request message framing, etc.)","customLabel":""},{"id":"eXy7xHvpQ-HT16gZp2CNA","language":"412","code":"// 412 precondition failed: Returns an error message if access to the target resource has been denied. (For example- if any of the parameter value is incorrect or license has expired)","customLabel":""}],"selectedLanguageId":"eXy7xHvpQ-HT16gZp2CNA"},"examples":{"languages":[{"id":"_mGBjlMU9k01Z6CEkara5","language":"python","code":"import requests\n\nmodelID=\"<< Enter Model ID >>\"\nurl = \"https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/\"+modelID+\"\"\n\n# please select proper payload for your usecase for extraction, evasion or poisoning.\npayload={\n # <>\n}\nheaders = {\n 'Accept': 'application/json',\n 'x-api-key': '########################################',\n 'Org-Id': '####################################################################################################'\n}\n\nresponse = requests.request(\"POST\", url, headers=headers, data=payload)\n\nprint(response.text)","customLabel":""},{"id":"EZTVIARgk4Cgsi2z3kaoP","language":"curl","code":"modelID=\"<< Enter Model ID >>\"\ncurl --location 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/${modelID}' \\\n--header 'x-api-key: ########################################' \\\n--header 'Org-Id: ####################################################################################################' \\\n--header 'Content-Type: application/json' \\\n--data '{\n <>\n}'","customLabel":""},{"id":"kc6RvtVQgBj0xpcZD7Nak","language":"nodejs","code":"var request = require('request');\n\nmodelID = '<>'\nvar options = {\n 'method': 'POST',\n 'url': 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/'+modelID+'',\n 'headers': {\n 'x-api-key': '########################################',\n 'org_id': '####################################################################################################',\n 'Content-Type': 'application/json'\n },\n body: JSON.stringify({\n // <>\n })\n\n};\nrequest(options, function (error, response) {\n if (error) throw new Error(error);\n console.log(response.body);\n});\n","customLabel":""},{"id":"Nx00RqrLXpofFTyDCguK0","language":"javascript","code":"var myHeaders = new Headers();\nmyHeaders.append(\"x-api-key\", \"########################################\");\nmyHeaders.append(\"org_id\", \"####################################################################################################\");\nmyHeaders.append(\"Content-Type\", \"application/json\");\n\nvar raw = JSON.stringify({\n // << Enter Payload Details based on Task pair >>\n});\n\nvar modelID = \"<< Enter Model ID >>\"\n\nvar requestOptions = {\n method: 'POST',\n headers: myHeaders,\n body: raw,\n redirect: 'follow'\n};\n\nfetch(\"https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/\"+modelID+\"\", requestOptions)\n .then(response => response.text())\n .then(result => console.log(result))\n .catch(error => console.log('error', error));","customLabel":""}],"selectedLanguageId":"EZTVIARgk4Cgsi2z3kaoP"},"description":"","currentNewParameter":{"label":"Path Parameter","value":"pathParameters"}}"}
:::
:::hint{type="info"}
Note: In the response, copy job\_id. This value is required to trigger the GET APIs. See [\ Job Metadata](docId\:S-mZ7r0HNzicDQy6Q-6Hq).
The "job\_id" is used to retrieve model analysis metadata and check the processing status of the request. It is also used for generating reports for the analyzed model. Copy the dashboard link from the response and open it in a new tab. This allows users to monitor the job progress and download reports.
:::
:::hint{type="info"}
For using Nodejs sample code, install npm package request
Given ample code for python is tested for Python version 3.7
Given Sample code for nodejs and javascript is tested for Node V20LTS
:::
[title] Time Series Forecasting
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/Analyze your models/Time Series/
The below input parameters are for different attack types. To start working with the APIs view the [Times Series Forecasting](docId\:EB7FsMB2O-fz1_RLafm9u).
### File upload format
- **Data**: Data should be in a CSV file with a header as all the features (Columns) name and the last column as the target variable.
Downloa sample data
- **Minmax**: Data should be in a CSV file with a header as all the feature (Columns) names and the last column as the target variable. The first row of the CSV file should contain the minimum value for each column (feature), and the second row should contain the max value.
Downloa sample minmax
- **Model**: The model should be saved in either .pkl, .h5 or TensorFlow format with full architecture. Full architecture is needed when loading the model to the platofrm for assessment either in encrypted or unencrypted. This can be ignored when model is hosted as an API.
Download sample model
:::hint{type="warning"}
All files uploaded should be in zipped format. The above files are sample data.
:::
:::ExpandableHeading
## Extraction parameters
| Parameter | Data type | Descrption | Remark |
| ------------------------------ | --------- | ------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------ | ---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| model\_id | String | Model\_id received during model registration. We need to provide
this model\_id in query parameter in URL. | you have to do model registration only once for a model and you can perform many analysis. This will help you to track how many api call has been made, how many has successed. |
| **Request Body (Json format)** | | | |
| attack\_type | String | You can select the attack type either Blackbox or Greybox. | **Blackbox**: for performing model analysis, no information about model or data will be used. **Greybox**: information about data will be leverage for creation of attack data
**Note: **only 2-5 % of data is needed |
| input\_dimensions | String | Input dimension (Example 100,6 for Pump Sensor) | the parameter should be string. |
| number\_of\_attack\_queries | String | Number of attack queries that model will be subjected to. | generally Heigher the number of attack queries, better would be the analysis. And it would take more time to process. (Range: >0
& \<=400000) |
| model\_framework | String | Original model is built with tensorflow framework.(Option :\[tensorflow]) | curretly supported framework are: tensorflow, scikit-learn, keras |
| model\_api\_details | String | If use\_model\_api is Yes, then provide API details of hosted model as
encrypted JSON string is mandatory | provide this only if use\_model\_api is "yes". |
| use\_model\_api | String | Use model API to train your model instead of uploading the model as a zip. | when this parameter is yes, you don't have to upload model as zip. You can pass api url along with other verification credential in json file. |
| defense\_bestonly | String | Highly optimized defense model will be returned. | when selected **"yes"**, it will train N number of model and select best model. Ofcourse this will take longer time. If **"no"**, then once defense model accuracy reached above 95% It will stop |
| encryption\_strategy | Int | Choose a encryption strategy for you model. if model is uploaded directly as a
zip pick 0, 1 if model is encryted as .pyc and
uploaded as a zip. Ignore if use\_model\_api is
Yes | select 0: pass tensorflow model as it is, select 1: pass encrypted model. It could be .pyc file |
| vulnerability\_threshold | String | Threshold percent of stolen model accuracy at which defense model should be generated | parameter value will be between 0 to 1. |
:::
:::hint{type="info"}
To access all sample artifacts, please visit [Artifacts](docId\:iJNEOCXoStabvvrsq11fa).
- For specific artifact details, refer
- Vulnerability Report : [Vulnerability Report](docId\:hL0uT2MWlCBkt8F97fr-W)
- Sample Attacks : [Sample Attacks](docId:4G1mjM5lQjfm8t5WBVwpr)
- Defense Report: [Defense Report](docId\:VtzlTtpja2VSF2j0STLSQ)
- Defense Model: [Defense Model](docId\:xSbxmZXW4vv14-8NmBF8M)
:::
:::hint{type="info"}
**Note**: For Time series forecasting, supported attack types are - Extraction
:::
[title] Vulnerability Report
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/Artifacts/
The vulnerability report provides information about critical vulnerabilities related to model attacks. It includes an overview of the severity of the issue and associated risks, and suggests mitigation measures.
Following are the different parts explaining the model metrics in detail:
**Part 1: Overview
**This section of the report presents metadata information for the job ID, including details such as the attack type, number of attack queries, stolen model accuracy, alert level (low or high), and whether defense measures are recommended or not.
**Part 2: Security**
In this section of the report, we emphasize the relative metrics score achieved by the extracted model.
**Part 3: Performance**
In this section of the report, we examine the critical aspects of inference time and respective metrics for both the original model and the extracted model. We discuss the time required for the models to generate predictions on new data, as well as the performance metrics used to measure their accuracy and overall effectiveness.
**Part 4: Drift**
This section highlights the application of statistical tests for detecting data drift. Data drift refers to changes in the statistical properties of the input data used to train a model. We will introduce this upcoming feature to our product.
**Part 5: Appendix**
The Appendix section of the report serves as a comprehensive resource, offering essential information regarding the architectures of both the Original Model and Model attack type.
To see sample vulnerability report for respective attack types, refer the below table.
| Input type | Vulnerbility report |
| ----------------------- | ----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| Image classification | Extraction, Evasion,model-poisoning, data-poisoning |
| Image segmentation | Extraction |
| Object Detection | Evasion |
| Tabular classification | Extraction, Evasion |
| Time series forecasting | Extraction Machine Learning, Extraction Deep Learning |
| Text classification | Extraction |
| Text Recommendation | Extraction |
| AudioSpeechRecognition | Evasion |
| Supply Chain | Vulnerability Report |
[title] FAQ & Troubleshooting
[path] /
[title] Limitations
[path] FAQ & Troubleshooting/
- Longer wait times (\~6-8 hours) can be expected if multiple earlier jobs are running. Users can keep observing the status of the job by using the GET API or the Dashboard link.
- "Number of attack queries" parameter currently is limited to \<=400000 for all tasks.
- "Number of classes" parameter should be \<200 for all classification task type.
- When executing the reference implementation, it is recommended to install the per-requisite libraries with exact versions.
- The product currently supports Tensorflow version between 2.3.0 and 2.15.0.
- Tabular classification supports scikit-learn models with preferred version 1.4.0 and XGBoost model version 2.0.3.
- Image classification evasion defense might be less effective against very small perturbation.
- Image classification poisoning - Encryption strategy and use model api endpoint not supported. Also it requires two clean model and one test model.
- Tabular classification evasion analysis is only supported with a normalized dataset Between 0-1.
- The image should be in **RGB format**, and the model should be trained with images in this format.
- When the number of attack queries is low, such as 1000 or fewer, the system automatically generates them.
[title] RedTeaming Analysis
[path] API Documentation/AISpectra/Automated RedTeaming for GenAI/
The below parameters are for automated redteaming analysis for GenAI. To know more about the different test parameters, see Automated RedTeaming for GenAI.
:::CodeblockTabs
Start-analysis
```json
{
"cloud_env": "azure",
"model_backbone": "openai",
"api_key": "",
"api_endpoint_url": "https://.com/",
"api_version": "",
"api_endpoint_deployment_name": "",
"test_connection": false,
"test_task": "chatbot",
"test_level": "lite",
"test_sel_parameters": ["toxicity", "jailbreak"]
}
```
Test-Connection
```json
{
"cloud_env": "azure",
"model_backbone": "openai",
"api_key": "",
"api_endpoint_url": "https://.com/",
"api_version": "",
"api_endpoint_deployment_name": "",
"test_connection": True
}
```
:::
:::ExpandableHeading
### Payload parameters
- **test\_task: **"chatbot"
- **test\_level: **"lite", "basic", "intermediate", "advanced", "super-adv"
- **test\_sel\_parameters: **"toxicity", "nsfw", "generic-harm", "jailbreak", "sid", "pii", "spii"
:::
:::ApiMethodV2{data="{"tab":"examples","url":"https://api.aws.boschaishield.com/prod/api/ais/v1.5/genairedteaming","name":"Model anaylsis","method":"POST","request":{"pathParameters":[{"name":"content-type","kind":"required","type":"string","description":"application/json","":"application/json"}],"queryParameters":[],"headerParameters":[{"kind":"required","name":"x-api-key","type":"string","children":[],"description":"Enter your API key"},{"kind":"required","name":"Org-id","type":"string","children":[],"description":"Enter your organization id"}],"bodyDataParameters":[],"formDataParameters":[]},"results":{"languages":[{"id":"DL4HDcclTH6dUtOu-opbD","code":"// 200 OK: Returns a JSON object containing unique model ID and urls to upload required files.","language":"200","customLabel":""},{"id":"z5dS_OPIMHsxFEwrtKnkw","language":"401","code":"// 401 Unauthorized: Returns an error message if the provided API key or Org-ID is invalid or expired.","customLabel":""},{"id":"xJHL9zR5wAZ30f4gu2BUz","language":"400","code":"// 400 Bad request Error: Returns an error message if the application cannot or will not process the request due to something that is perceived to be a client error (for example, malformed request syntax, invalid request message framing, etc.)","customLabel":""},{"id":"eXy7xHvpQ-HT16gZp2CNA","language":"412","code":"// 412 precondition failed: Returns an error message if access to the target resource has been denied. (For example- if any of the parameter value is incorrect or license has expired)","customLabel":""}],"selectedLanguageId":"eXy7xHvpQ-HT16gZp2CNA"},"examples":{"languages":[{"id":"_mGBjlMU9k01Z6CEkara5","language":"python","code":"import requests\n\nurl = \"https://api.aws.boschaishield.com/prod/api/ais/v1.5/genairedteaming\"\n\n# please select proper payload for your usecase for extraction, evasion or poisoning.\npayload={\n # <>\n}\nheaders = {\n 'Accept': 'application/json',\n 'x-api-key': '########################################',\n 'Org-Id': '####################################################################################################'\n}\n\nresponse = requests.request(\"POST\", url, headers=headers, data=payload)\n\nprint(response.text)","customLabel":""},{"id":"EZTVIARgk4Cgsi2z3kaoP","language":"curl","code":"modelID=\"<< Enter Model ID >>\"\ncurl --location 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/${modelID}' \\\n--header 'x-api-key: ########################################' \\\n--header 'Org-Id: ####################################################################################################' \\\n--header 'Content-Type: application/json' \\\n--data '{\n <>\n}'","customLabel":""},{"id":"kc6RvtVQgBj0xpcZD7Nak","language":"nodejs","code":"var request = require('request');\n\nmodelID = '<>'\nvar options = {\n 'method': 'POST',\n 'url': 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/'+modelID+'',\n 'headers': {\n 'x-api-key': '########################################',\n 'org_id': '####################################################################################################',\n 'Content-Type': 'application/json'\n },\n body: JSON.stringify({\n // <>\n })\n\n};\nrequest(options, function (error, response) {\n if (error) throw new Error(error);\n console.log(response.body);\n});\n","customLabel":""},{"id":"Nx00RqrLXpofFTyDCguK0","language":"javascript","code":"var myHeaders = new Headers();\nmyHeaders.append(\"x-api-key\", \"########################################\");\nmyHeaders.append(\"org_id\", \"####################################################################################################\");\nmyHeaders.append(\"Content-Type\", \"application/json\");\n\nvar raw = JSON.stringify({\n // << Enter Payload Details based on Task pair >>\n});\n\nvar modelID = \"<< Enter Model ID >>\"\n\nvar requestOptions = {\n method: 'POST',\n headers: myHeaders,\n body: raw,\n redirect: 'follow'\n};\n\nfetch(\"https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/\"+modelID+\"\", requestOptions)\n .then(response => response.text())\n .then(result => console.log(result))\n .catch(error => console.log('error', error));","customLabel":""}],"selectedLanguageId":"_mGBjlMU9k01Z6CEkara5"},"description":"","currentNewParameter":{"label":"Path Parameter","value":"pathParameters"}}"}
:::
[title] Untitled
[path] Platform guide/
[title] Audio
[path] API Documentation/AISpectra/Automated RedTeaming for AI/ML/ Model Analysis/
::::LinkArray
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/fe7OX1eSJl1WfnX17hHgp_ehr-based-6.png"}
[Automatic Speech Recognition](docId\:jzmdhfXEhv4mJlKb6GUsi)
Seamlessly analyze automatic speech recognization with accuracy and efficiency
:::
::::
[title] Untitled
[path] API Documentation/AISpectra/
[title] AI/ML Supply Chain Risk Mapping
[path] Platform guide/AISpectra/Model Scanner/AI/ML Supply Chain/
## Overview
Supply chain compromise in AI/ML involves adversarial actions targeting the supply chain of AI/ML systems. This includes manipulation of software, data, or model dependencies, leading to vulnerabilities in downstream applications.
## Supply Chain Compromise - Model
AI and machine learning systems often rely on open-source models, which are downloaded and fine-tuned using private datasets. These models require executing saved code during loading, creating risks of compromise through traditional malware or adversarial techniques that manipulate the model’s behavior. This dependency on external sources makes AI/ML systems vulnerable to supply chain attacks.
Supply chain compromise in AI/ML Models are extensively mapped across multiple frameworks, including **MITRE ATLAS** ([AML.T0010](https://atlas.mitre.org/techniques/AML.T0010)) for model-specific risks, **MITRE ATT\&CK** ([T1195.002](https://attack.mitre.org/techniques/T1195/002)) for software supply chain manipulation, and the **OWASP Top 10 for LLMs** ([LLM03:2025](https://genai.owasp.org/llmrisk/llm032025-supply-chain/)) for vulnerabilities in pre-trained models. It also aligns with the **Map** and **Govern** functions of the **NIST AI Risk Management Framework (AI RMF)**, emphasizing the identification, management, and oversight of AI supply chain risks to ensure system trust. For detail refer information below table.
| Framework | File Format | Deserialization | Backdoor | Runtime | Vulnerability ID |
| ----------------- | ------------ | --------------- | -------- | ------- | ------------------------------------------------------------------------------------- |
| Tensorflow | .pb | ✅ | | | AIS-TF-D-01: Protobuf Deserialization |
| Tensorflow | .pb | | ✅ | | AIS-TF-B-01: TensorFlow PB Backdoor |
| Tensorflow | .h5 | ✅ | | | AIS-TF-D-02: TensorFlow/Keras H5 Deserialization |
| Tensorflow | .h5 | | ✅ | | AIS-TF-B-02: TensorFlow/Keras H5 Backdoor with malicious layers |
| Checkpoint(TF,PT) | .ckpt | ✅ | | | AIS-CP-D-01: TensorFlow/PyTorch Checkpoint (saved intermediate model) Deserialization |
| Keras | .keras | ✅ | | | AIS-KR-D-01: Keras Deserialization |
| Keras | .keras | | ✅ | | AIS-TF-B-02: TensorFlow/Keras H5 Backdoor with malicious layers |
| Keras | .h5 | ✅ | | | AIS-TF-D-02: TensorFlow/Keras H5 Deserialization |
| Keras | .h5 | | ✅ | | AIS-TF-B-02: TensorFlow/Keras H5 Backdoor with malicious layers |
| PyTorch | .pt | ✅ | | | AIS-PT-D-01: Pickle Serialization in PyTorch Models |
| PyTorch | .pth | ✅ | | | AIS-PT-D-01: Pickle Serialization in PyTorch Models |
| PyTorch | .bin | ✅ | | | AIS-PT-D-02: Serialization in PyTorch Models |
| ONNX | .onnx | | ✅ | | AIS-ON-B-01: ONNX Architecture Backdoor |
| ONNX | .onnx | | | ✅ | AIS-ON-R-01: Corrupted or Manipulated File Format |
| GGUF | .gguf | | | ✅ | AIS-GU-R-01: GGUF Runtime Threat |
| Scikit-Learn | .pkl | ✅ | | | AIS-PK-D-01: Pickle Serialization |
| Misc | .zip | ✅ | | | AIS-MI-D-01: Zip File Trojan or file corruption |
| SafeTensors | .safetensors | ✅ | | | AIS-ST-D-01: Improper file Format |
| SafeTensors | .safetensors | ✅ | | | AIS-ST-D-02: File shards – path traversal Error |
### MITRE ATLAS Mapping: Model Compromise
The vulnerabilities highlighted in the table above align with the concerns outlined in the **ML Supply Chain Compromise** technique under the MITRE ATLAS framework ([AML.T0010](https://atlas.mitre.org/techniques/AML.T0010)). Specifically, risks associated with compromised models are covered under the sub-technique **ML Supply Chain Compromise: Model** ([AML.T0010.003](https://atlas.mitre.org/techniques/AML.T0010.003)). These compromises typically involve malicious modifications to pre-trained models, unauthorized changes in model weights, or backdoor injections in serialized formats.
### MITRE ATT\&CK Mapping: AI/ML Supply Chain Compromise
The vulnerabilities identified in AI/ML systems align with the **Supply Chain Compromise** technique in the MITRE ATT\&CK framework ([T1195](https://attack.mitre.org/techniques/T1195/)). This technique encompasses risks associated with the manipulation of products or delivery mechanisms prior to their receipt by the final consumer, aiming to compromise data or systems.
Specifically, AI/ML systems are susceptible to:
- **Compromise of Software Supply Chain** ([T1195.002](https://attack.mitre.org/techniques/T1195/002/)): Attackers might tamper with the software supply chain by modifying application source code, manipulating update mechanisms, or replacing legitimate software with malicious versions. In the context of AI/ML, this could involve distributing altered pre-trained models or corrupted datasets.
### OWASP Top 10 for LLM: Supply Chain Vulnerabilities
The vulnerabilities identified in AI/ML systems correspond to the **Supply Chain** risk outlined in the OWASP Top 10 for Large Language Models (LLMs) ([LLM03:2025 Supply Chain](https://genai.owasp.org/llmrisk/llm032025-supply-chain/)). This risk emphasizes the susceptibility of LLM supply chains to various vulnerabilities that can compromise the integrity of training data, models, and deployment platforms. Key concern include:
- **Vulnerable Pre-Trained Models**: Utilizing third-party models that may contain hidden biases, backdoors, or malicious features due to tampering or poisoning attacks.
## Supply Chain Compromise - Software
Supply chain compromise in software occurs when adversaries target software components, including dependencies, configurations, or distribution mechanisms. These compromises aim to inject malicious elements into the development or runtime environment, potentially leading to unauthorized access, data breaches, or system failures.
Supply chain compromise in AI/ML software is extensively mapped across multiple frameworks, including **MITRE ATLAS** ([AML.T0010](https://atlas.mitre.org/techniques/AML.T0010)) for software-specific risks, **MITRE ATT\&CK** ([T1195.001](https://attack.mitre.org/techniques/T1195/001/)) for manipulation of software supply chains, the **OWASP Top 10 for LLMs** ([LLM03:2025](https://genai.owasp.org/llmrisk/llm032025-supply-chain/)) and the **OWASP Top 10** ([A06:2021](https://owasp.org/Top10/A06_2021-Vulnerable_and_Outdated_Components/)) for risks associated with outdated and vulnerable components. Additionally, these risks align with the **Map** and **Govern** functions of the **NIST AI Risk Management Framework (AI RMF)**, which emphasize proactive identification, management, and governance of software supply chain vulnerabilities to maintain trust and security in AI systems.
| Framework | File Format | Security | Vulnerability ID |
| ---------------- | --------------- | -------- | ---------------------------------------------- |
| Jupyter Notebook | .ipynb | ✅ | AIS-PY-S-01: Compromised Components, libraries |
| Python | .py | ✅ | AIS-PY-S-01: Compromised components, libraries |
| Misc | requirement.txt | ✅ | AIS-PY-S-01: Compromised components, libraries |
### MITRE ATLAS Mapping: ML Software Compromise
The vulnerabilities highlighted in the table above align with the concerns outlined in the **ML Supply Chain Compromise** technique under the MITRE ATLAS framework ([AML.T0010](https://atlas.mitre.org/techniques/AML.T0010)). Specifically, risks associated with compromised libraries, components and other artefacts are covered under the sub-technique **ML Supply Chain Compromise: ML Software** ([AML.T0010.001](https://atlas.mitre.org/techniques/AML.T0010.001)). These compromises typically involve usage of malicious, deprecated libraries and components.
### MITRE ATT\&CK Mapping: AI/ML Supply Chain Compromise
The vulnerabilities identified in AI/ML systems align with the **Supply Chain Compromise** technique in the MITRE ATT\&CK framework ([T1195](https://attack.mitre.org/techniques/T1195/)). This technique encompasses risks associated with the manipulation of products or delivery mechanisms prior to their receipt by the final consumer, aiming to compromise data or systems.
Specifically, AI/ML systems are susceptible to:
- **Compromise of Software Dependencies and Development Tools** ([T1195.001](https://attack.mitre.org/techniques/T1195/001/)): Adversaries may inject malicious code into software dependencies or development tools commonly used in AI/ML pipelines. This can lead to the execution of unauthorized code within AI models or data processing workflows.
### OWASP Top 10 for LLM: Supply Chain Vulnerabilities
The vulnerabilities identified in AI/ML systems correspond to the **Supply Chain** risk outlined in the OWASP Top 10 for Large Language Models (LLMs) ([LLM03:2025 Supply Chain](https://genai.owasp.org/llmrisk/llm032025-supply-chain/)). This risk emphasizes the susceptibility of LLM supply chains to various vulnerabilities that can compromise the integrity of training data, models, and deployment platforms. Key concern include:
- **Outdated or Deprecated Components**: Relying on components that are no longer maintained, leading to potential security issues.
- **Manipulated Components**: Relying on components that are no longer maintained, leading to potential security issues.
### OWASP Top 10 Classic: Vulnerable and Outdated Components
The vulnerabilities identified in AI/ML systems correspond to the **Vulnerable and Outdated Components** risk outlined in the OWASP Top 10 ([A06:2021 - Vulnerable and Outdated Components](https://owasp.org/Top10/A06_2021-Vulnerable_and_Outdated_Components/)). This risk highlights the dangers posed by relying on software libraries, frameworks, and components that are outdated, unsupported, or contain known vulnerabilities. Key concerns include:
- **Outdated or Deprecated Components**: Using outdated or deprecated software components that lack security patches or updates, leaving systems exposed to exploitation. This is particularly relevant for machine learning systems, where dependencies often include pre-trained models and data processing libraries that may not be actively maintained.
- **Manipulated Components**: Employing components that have been tampered with, whether through malicious intent or accidental corruption, which can introduce security vulnerabilities and compromise system integrity.
## Vulnerability ID Nomenclature:
| **Format (AIS-XX-Y-NN)** | **Description** |
| ------------------------ | ---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| **AIS** | AIShield AI Spectra SAST Assessment Tag |
| **XX** | Framework Tag:
\- `TF`: TensorFlow
\- `CP`: Checkpoint
\- `KR`: Keras
\- `PT`: PyTorch
\- `ON`: ONNX
\- `GU`: GGUF
\- `MI`: Misc
\- `ST`: SafeTensors
\- `PY`: Python file(.py) or notebook (.ipynb) |
| **Y** | Risk Tag:
\- `D`: Deserialization
\- `B`: Backdoor
\- `R`: Runtime
\- `S`: Security |
| **NN** | Unique Number |
### Risk Overview
### Deserialization Risks:
Occurs when unverified data is used to rebuild objects. Attackers may exploit these to introduce malicious code, compromising system integrity.
### Backdoor Risks:
Hidden pathways allow attackers to manipulate model behavior through specific triggers. These covert exploits remain undetected during normal operations.
### Runtime Risks:
Activated during model inference or task execution, runtime risks involve malicious code execution, leading to unauthorized access or manipulation.
### Security Risks:
Risks due to security related aspects embedded in files or code inadvertently used.
[title] Text
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/Analyze your models/
::::LinkArray
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/QS-X5g14VUd-3tUAI5P3a_machine-learning-nlp-text-classification.png"}
[Text Recommendation](docId\:rp8-2r2fWgPoBf37LmgAb)
Its the process of categorizing text documents into predefined categories based on their content and context.
:::
::::
[title] Deployment Strategies
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/Threat Informed Defense/
AIShield supports two deployment strategies: parallel and series.
::::LinkArray
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/QQcYVxfaQ2axuPFGttxvH_untitled-design-1.png"}
[Parallel Deployment](docId\:tNd5MPJY36CI4lnKEbRCS)
Both Threat-Informed Defense Model and Original Model operate simultaneously, with telemetry data sent to SIEM tools.
:::
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/8Uoeex3cgmooKHnAtxYWv_untitled-design-1.png"}
[Series Deployment](docId\:CYrPdX5arNVKa6WQMHHsh)
Threat-Informed Defense Model is deployed just before the Original Model, with telemetry data sent to SIEM tools.
:::
::::
[title] Tabular
[path] API Documentation/AISpectra/Automated RedTeaming for AI/ML/ Model Analysis/
::::LinkArray
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/rHIQeI08sXI-3UDn5kBv0_ehr-based-5.png"}
[Tabular Classification](docId\:v08LzX7yC3id62W3z63yg)
Seamlessly analyze tabular classification models with accuracy and efficiency.
:::
::::
[title] Image Segmentation
[path] API Documentation/AISpectra/Automated RedTeaming for AI/ML/ Model Analysis/Image/
The below parameters are for various image segmentation attack types. To know more about the different attack input parameters, see [Image Segmentation](docId\:ZGifJwp4yRvB4Uog5-Qvh).
:::hint{type="info"}
The values presented below are examples taken from the MINST model used in the reference implementation. It is important to customize these values to achieve the best performance for your particular model.
:::
:::CodeblockTabs
Extraction
```json
{
"attack_type": "blackbox",
"defense_bestonly": "no",
"encryption_strategy": "0",
"input_dimensions": "128,32,1",
"model_api_details": "na",
"model_framework": "tensorflow",
"normalize_data": "yes",
"number_of_attack_queries": "100",
"number_of_classes": "1",
"use_model_api": "no",
"vulnerability_threshold": "0.00"
}
```
:::
:::ApiMethodV2{data="{"tab":"examples","url":"https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse","name":"Model anaylsis","method":"POST","request":{"pathParameters":[{"name":"model_id","kind":"required","type":"string","description":"Enter your model id","children":[]}],"queryParameters":[],"headerParameters":[{"kind":"required","name":"Org_id","type":"string","children":[],"description":"Enter your organization id"},{"kind":"required","name":"x-api-key","type":"string","children":[],"description":"Enter your API key"}],"bodyDataParameters":[],"formDataParameters":[]},"results":{"languages":[{"id":"DL4HDcclTH6dUtOu-opbD","code":"// 200 OK: Returns a JSON object containing unique model ID and urls to upload required files.","language":"200","customLabel":""},{"id":"z5dS_OPIMHsxFEwrtKnkw","language":"401","code":"// 401 Unauthorized: Returns an error message if the provided API key or Org-ID is invalid or expired.","customLabel":""},{"id":"xJHL9zR5wAZ30f4gu2BUz","language":"400","code":"// 400 Bad request Error: Returns an error message if the application cannot or will not process the request due to something that is perceived to be a client error (for example, malformed request syntax, invalid request message framing, etc.)","customLabel":""},{"id":"eXy7xHvpQ-HT16gZp2CNA","language":"412","code":"// 412 precondition failed: Returns an error message if access to the target resource has been denied. (For example- if any of the parameter value is incorrect or license has expired)","customLabel":""}],"selectedLanguageId":"eXy7xHvpQ-HT16gZp2CNA"},"examples":{"languages":[{"id":"s0yKnzGqfZRmb3w2uVP6Y","language":"python","code":"import requests\n\nmodelID=\"<< Enter Model ID >>\"\nurl = \"https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/\"+modelID+\"\"\n\n# please select proper payload for your usecase for extraction, evasion or poisoning.\npayload={\n # <>\n}\nheaders = {\n 'Accept': 'application/json',\n 'x-api-key': '########################################',\n 'Org-Id': '####################################################################################################'\n}\n\nresponse = requests.request(\"POST\", url, headers=headers, data=payload)\n\nprint(response.text)","customLabel":""},{"id":"SS68HWeWjeirRQgIqTzWl","language":"curl","code":"modelID=\"<< Enter Model ID >>\"\ncurl --location 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/${modelID}' \\\n--header 'x-api-key: ########################################' \\\n--header 'Org-Id: ####################################################################################################' \\\n--header 'Content-Type: application/json' \\\n--data '{\n <>\n}'","customLabel":""},{"id":"QMV9PAwkH3cOX0MU_ihaN","language":"nodejs","code":"var request = require('request');\n\nmodelID = '<>'\nvar options = {\n 'method': 'POST',\n 'url': 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/'+modelID+'',\n 'headers': {\n 'x-api-key': '########################################',\n 'Org-Id': '####################################################################################################',\n 'Content-Type': 'application/json'\n },\n body: JSON.stringify({\n // <>\n })\n\n};\nrequest(options, function (error, response) {\n if (error) throw new Error(error);\n console.log(response.body);\n});\n","customLabel":""},{"id":"yxOmWwSct-_bDglESPASD","language":"javascript","code":"var myHeaders = new Headers();\nmyHeaders.append(\"x-api-key\", \"########################################\");\nmyHeaders.append(\"Org-Id\", \"####################################################################################################\");\nmyHeaders.append(\"Content-Type\", \"application/json\");\n\nvar raw = JSON.stringify({\n // << Enter Payload Details based on Task pair >>\n});\n\nvar modelID = \"<< Enter Model ID >>\"\n\nvar requestOptions = {\n method: 'POST',\n headers: myHeaders,\n body: raw,\n redirect: 'follow'\n};\n\nfetch(\"https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/\"+modelID+\"\", requestOptions)\n .then(response => response.text())\n .then(result => console.log(result))\n .catch(error => console.log('error', error));","customLabel":""}],"selectedLanguageId":"yxOmWwSct-_bDglESPASD"},"description":"","currentNewParameter":{"label":"Path Parameter","value":"pathParameters"}}"}
:::
:::hint{type="info"}
Note: In the response, copy job\_id. This value is required to trigger the GET APIs. See [\ Job Metadata](docId\:S-mZ7r0HNzicDQy6Q-6Hq).
The "job\_id" is used to retrieve model analysis metadata and check the processing status of the request. It is also used for generating reports for the analyzed model. Copy the dashboard link from the response and open it in a new tab. This allows users to monitor the job progress and download reports.
:::
:::hint{type="info"}
For using Nodejs sample code, install npm package request
Given ample code for python is tested for Python version 3.7
Given Sample code for nodejs and javascript is tested for Node V20LTS
:::
5
[title] AIShield overview
[path] Introduction to AIShield/
AIShield integrates into your MLOps pipeline to enhance your model's security. After training your model, you can use AIShield to identify vulnerabilities and receive threat-informed EDR (Endpoint Defense and Response) to fortify your model.
Once your model is deployed, AIShield can monitor it in real-time against attacks and provide integrations such as SIEM and SOAR. You can see the [Attack types](docId:02d3w0EDgV16u4hUlehlP) we support.

[title] Sagemaker
[path] Integration Partners/MLOps/
Amazon SageMaker is a fully-managed service that provides developers and data scientists with the ability to build, train, and deploy machine learning models at scale. With SageMaker, you can quickly and easily create machine learning models using popular frameworks like TensorFlow and PyTorch, and then deploy them to production environments with just a few clicks.
To use SageMaker, you will need an AWS subscription. Once you have an AWS subscription, follow these steps to get started:
1. Create a SageMaker notebook instance with the desired configuration.
2. Import and open the provided notebook and code folder in the SageMaker environment.
3. Follow the steps outlined in the notebook.
4. Make sure to change variable/parameter values as per your run configuration.
5. Note that there are two requirements files: one at the notebook level for installing required packages and one inside the code folder for deployment-related requirements.
You can find the required files in the reference implement on GitHub.
[title] AWS IoT Greengrass Deployment
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/Threat Informed Defense/Deployment on Edge Device/
# **AIShield for Secure AI at Edge (AIShield.Edge)**
In the rapidly evolving landscape of AI, securing models from threats has become paramount. **AIShield for Secure AI at Edge (AIShield.Edge)** is your answer to this challenge, seamlessly integrating with the AWS Greengrass ecosystem.
One of its standout features is the ability to retrieve the latest defense model directly from an Amazon S3 bucket, ensuring that your AI models are always protected with the most updated defenses. But that's just the beginning. The **AIShield.Edge **further strengthens its communication lines by employing the TokenExchangeService, ensuring that every interaction with AWS clients is secure and reliable.
Where it truly shines, however, is in its real-time threat detection capabilities. This component is always vigilant, continuously monitoring AI/ML models for any signs of breaches or attacks. Upon detecting any irregularity, it springs into action, instantly relaying telemetry data to the AWS IoT Core. This not only ensures swift incident response but also fortifies the model's security parameters.
Using inter-process communication (IPC), it adeptly receives input in the bytes format. Once the data is gathered, it engages in meticulous real-time analysis leveraging the defense model. Any critical findings are then promptly relayed to the AWS IoT Core via the MQTT protocol.
To summarize, **AIShield.Edge **isn't just a component; it's a comprehensive AI security solution. With its advanced threat detection, real-time data analysis, and seamless AWS integration, it serves as a formidable shield for your AI/ML models.
You can get the defense model from AIShield Vulnerability analysis. contact [AIShield.Contact@bosch.com](https://boschaishield.com/#) to know more.
# Component Deployment
### List Component
You should be able to locate the **AIShield.Edge** component in the AWS console under the **AWS IoT->Greengrass->component** section.

From there, you can include it in a Greengrass deployment and push it to your device.
:::hint{type="info"}
**Note:** For the component to run successfully, you'll need to update the default configuration during the deployment process, as detailed in the next sect**
**
:::
### Configuration
This component provide the following configuration parameters when it is deployed:
> "TOPIC": "*"
> "S3_URI": "S3 URI of defense model"

**TOPIC**: Topic to publish and subscribe message from IPC and MQTT. Same topic will be used.
**S3\_URI**: s3 uri of defese model stored in s3 bucket. The uri should contain **.tflite model**, a **.json** file containing metadata.
:::hint{type="info"}
**Note**: 1. json should contain :** **
\{
"task": "image\_classification",
"attack": "Extraction",
"input\_shape": "(28,28,1)"
}
where input shape change according to model input shape
2\. The Component should have permission to download object from s3 bucket.
3\. The S3 URI should belong to S3 bucket for which permission is given.
:::
# Local log file
This component uses the following local log file:
> /greengrass/v2/logs/AIShield.Edge.log
# Limitation
1. The component currently has support exclusively for the Linux operating system.
2. Its functionality is limited to supporting image classification tasks.
3. It exclusively supports TensorFlow Lite models only.
# Frequently asked questions (FAQ)
1. **Exception: defense configuration file not found**
- s3 uri of zip file should contain tensorflow light defense model and a .json file containing "task", "attack","input\_shape".
- here .json file is missing for the s3 uri
2. **Exception: \_\_\_\_ is not s3 uri. expect s3 uri of the object to download**
- Given path is not s3 uri. please check
3. **ValueError: cannot reshape array**
- Data sent via IPC and input shape configured in configuration file doesn't match. Please check the data sent and input shape provided
4. **Error-model loading failed.**
- Expecting tensorflow\.tflite model. please check model.
5. **How to deploy component ?**
- Refer **Component deployment** and follow the steps
6. **Where to get defense model?**
- you can get defense artifact after performing vulnerability analysis. contact : [AIShield.Contact@bosch.com](https://boschaishield.com/#) to know more.
7. **Component is running but not able to send of receive message**
- Check the topic provided. ensure publisher and subscriber is using same topic.
# Contact us
Bosch Global Software Technologies Private Limited
123, Industrial Layout, Hosur Road, Koramangala, Bengaluru - 560095, India
E-mail: [AIShield.Contact@bosch.com](https://boschaishield.com/#)
[title] Analyze your models
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/
You can analyze your model for vulnerabilities by using the model analysis API. To test your model, refer to the table below to see the different attack types you can try. Use these attacks to generate vulnerability reports, sample attack vectors, and a threat-informed defense model based on input parameters, data, and model files.
You can use the suggested input parameter configuration or experiment with specific parameters to see how vulnerability reports and threat-informed defense models are generated.
:::hint{type="info"}
You have to first register your model using [\ Model Registration](docId\:Qknp3vmRQaWJeZAeoChlH) API to get started with model analysis. After that there are other APIs which you can use to get [\ Job Metadata](docId\:S-mZ7r0HNzicDQy6Q-6Hq) and [\ Retrieve Artifacts](docId\:WPaP09t55LT3Z8rwY-Uz9) and more.
:::
| Supported data input | Task type | Inputs parameters | Model analysis APIs | Usecase | Reference-implementation |
| -------------------- | ---------------------- | ------------------------------------------------------- | ------------------------------------------------------------------- | -------------------------------------------------------------------------------------------------------------------- | -------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| Images | Image classification | [Image Classification](docId:6DEIiMJnkL5D0cdWSTCKb) | [Image Classification](docId:7pfTV3D26cUJsz6vMQloO) | Recognizing handwritten digits for digit recognition in postal services. | Reference |
| | Image segmentation | [Image Segmentation](docId\:BixNeMI0eUuJfUMau7eBx) | [Image Segmentation](docId\:ZGifJwp4yRvB4Uog5-Qvh) | In medical imaging, segmenting tumor regions from brain MRI scans to assist in diagnosing and treating brain tumors. | |
| Tabular | Tabular classification | [Tabular Classification](docId\:mVtLcTNKaSHPx9MzjvB62) | [Tabular Classification](docId\:v08LzX7yC3id62W3z63yg) | Predicting customer churn in a telecommunications company based on historical usage data. | Reference |
| Time series | Forecasting | [Time Series Forecasting](docId\:KDsa2HzsaXO0WcQIcDDc4) | [Times Series Forecasting](docId\:EB7FsMB2O-fz1_RLafm9u) | Predicting stock prices using time series forecasting | Reference |
| Text | Text classification | [Text Recommendation](docId\:rp8-2r2fWgPoBf37LmgAb) | [Text Recommendation (Alpha-release)](docId\:pF0-V4Ug62-akwbXCLkoZ) | Categorizing emails as "spam" or "not spam" based on their content. | |
| Static Assessment | Supply chain | [Supply Chain Attacks](docId\:J4ucahO6hlJPP6kfpVUVw) | [Supply Chain Analysis](docId\:XJ37o9KMfmRai84Bslqwx) | Scan for serialisation threats, backdoor attacks and any PII, keys leak in Notebook files | |
[title] Supply chain get policy
[path] API Documentation/AISpectra/Model Scanner/
The **Supply Chain Get Policy API **allows users to **fetch the currently configured security policies **for a specified repository type. This includes policies related to **scan format suppression, file format suppression, vulnerability types, and tool strictness levels**.
:::ApiMethodV2{data="{"name":"get_policy","method":"GET","url":"https://api.aws.boschaishield.com/prod/api/ais/v1.5/developer/get_policy","description":"This API fetches the configured policy.","tab":"examples","examples":{"languages":[{"id":"vVyrl_LmBXHzL6cfcELKP","language":"python","code":"import requests\n\nurl = \"https://api.aws.boschaishield.com/prod/api/ais/v1.5/developer/get_policy\"\n\npayload = {}\nheaders = {\n 'x-api-key': 'string',\n 'Org-Id': 'string'\n}\n\nresponse = requests.request(\"GET\", url, headers=headers, data=payload)\n\nprint(response.text)\n","customLabel":""},{"id":"vg0UyN2AhYcNJeUwa9pO1","language":"curl","code":"curl --location 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/developer/get_policy' \\\n--header 'x-api-key: string' \\\n--header 'Org-Id: string'","customLabel":""},{"id":"tlRURddoUt3pXqkHZ4W-o","language":"nodejs","code":"var request = require('request');\nvar options = {\n 'method': 'GET',\n 'url': 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/developer/get_policy',\n 'headers': {\n 'x-api-key': 'string',\n 'Org-Id': 'string'\n }\n};\nrequest(options, function (error, response) {\n if (error) throw new Error(error);\n console.log(response.body);\n});\n","customLabel":""},{"id":"V2F3tpnbCiFhPpgoTx0NB","language":"javascript","code":"var myHeaders = new Headers();\nmyHeaders.append(\"x-api-key\", \"string\");\nmyHeaders.append(\"Org-Id\", \"string\");\n\nvar requestOptions = {\n method: 'GET',\n headers: myHeaders,\n redirect: 'follow'\n};\n\nfetch(\"https://api.aws.boschaishield.com/prod/api/ais/v1.5/developer/get_policy\", requestOptions)\n .then(response => response.text())\n .then(result => console.log(result))\n .catch(error => console.log('error', error));","customLabel":""},{"id":"uUOAg6uIoUTXW8AwSRVrr","language":"ruby","code":"require \"uri\"\nrequire \"net/http\"\n\nurl = URI(\"https://api.aws.boschaishield.com/prod/api/ais/v1.5/developer/get_policy\")\n\nhttps = Net::HTTP.new(url.host, url.port)\nhttps.use_ssl = true\n\nrequest = Net::HTTP::Get.new(url)\nrequest[\"x-api-key\"] = \"string\"\nrequest[\"Org-Id\"] = \"string\"\n\nresponse = https.request(request)\nputs response.read_body\n","customLabel":""}],"selectedLanguageId":"vVyrl_LmBXHzL6cfcELKP"},"results":{"languages":[{"id":"N1fpC35SZxbcEWxck2pSW","language":"200","customLabel":"","code":"//200: policy response as json"},{"id":"HoRypJvdzSbrZlIR1DsHs","language":"401","code":"// 401 Unauthorized: Returns an error message if the provided API key or Org-ID is invalid or expired.","customLabel":""},{"id":"iDVOSM2kLZnuhseONktcg","language":"400","customLabel":"","code":"// 400 Bad request Error: Returns an error message if the application cannot or will not process the request due to something that is perceived to be a client error (for example, malformed request syntax, invalid request message framing, etc.)"},{"id":"FxGZoAFylQRraTE0xU1u7","language":"412","code":"// 412 precondition failed: Returns an error message if access to the target resource has been denied. (For example- if any of the parameter value is incorrect or license has expired)","customLabel":""}],"selectedLanguageId":"N1fpC35SZxbcEWxck2pSW"},"request":{"pathParameters":[],"queryParameters":[],"headerParameters":[{"name":"x-api-key","kind":"required","type":"string","description":"Enter your API key","":"required"},{"name":"Org-Id","kind":"required","type":"string","description":"Enter your organization id","":"Enter your organization id"}],"bodyDataParameters":[],"formDataParameters":[]},"currentNewParameter":{"label":"Body Parameter","value":"bodyDataParameters"},"hasTryItOut":true}"}
:::
[title] Time Series
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/Analyze your models/
::::LinkArray
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/-BTED7xrCygVjXIQSr2RO_ehr-based-7.png"}
[Time Series Forecasting](docId\:KDsa2HzsaXO0WcQIcDDc4)
These parameters enable analysis of different attack types to evaluate your time series model.
:::
::::
[title] Model Analysis
[path] API Documentation/AISpectra/Automated RedTeaming for AI/ML/
Get post model analysis API for different data input types.
::::LinkArray
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/OjBE0Mw5ME8aJunFPAqw2_ehr-based-6.png"}
[Image Classification](docId:7pfTV3D26cUJsz6vMQloO)
:::
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/NY63l-pNeHh99xnlzqHCL_ehr-based-5.png"}
[Tabular Classification](docId\:v08LzX7yC3id62W3z63yg)
:::
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/vD1QZlTpXaBxi6A3pE8zN_ehr-based-7.png"}
[Times Series Forecasting](docId\:EB7FsMB2O-fz1_RLafm9u)
:::
::::
[title] Text Recommendation (Alpha-release)
[path] API Documentation/AISpectra/Automated RedTeaming for AI/ML/ Model Analysis/Text/
The below parameters are for text recommendation attack types. To know more about the different attack input parameters see [Text Recommendation](docId\:rp8-2r2fWgPoBf37LmgAb).
:::hint{type="info"}
The values presented below are examples used in the reference implementation. It is important to customize these values to achieve the best performance for your particular model.
:::
:::CodeblockTabs
Extraction
```json
{
"use_model_api": "no",
"model_api_details": "no",
"model_framework": "tensorflow",
"encryption_strategy": "0",
"title": ""
}
```
:::
:::ApiMethodV2{data="{"tab":"examples","url":"https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse","name":"Model anaylsis","method":"POST","request":{"pathParameters":[{"name":"model id","kind":"required","type":"string","description":"Enter your model","children":[]}],"queryParameters":[],"headerParameters":[{"kind":"required","name":"Org_id","type":"string","children":[],"description":"Enter your organization id"},{"kind":"required","name":"x-api-key","type":"string","children":[],"description":"Enter your API key"}],"bodyDataParameters":[],"formDataParameters":[]},"results":{"languages":[{"id":"DL4HDcclTH6dUtOu-opbD","code":"// 200 OK: Returns a JSON object containing unique model ID and urls to upload required files.","language":"200","customLabel":""},{"id":"z5dS_OPIMHsxFEwrtKnkw","language":"401","code":"// 401 Unauthorized: Returns an error message if the provided API key or Org-ID is invalid or expired.","customLabel":""},{"id":"xJHL9zR5wAZ30f4gu2BUz","language":"400","code":"// 400 Bad request Error: Returns an error message if the application cannot or will not process the request due to something that is perceived to be a client error (for example, malformed request syntax, invalid request message framing, etc.)","customLabel":""},{"id":"eXy7xHvpQ-HT16gZp2CNA","language":"412","code":"// 412 precondition failed: Returns an error message if access to the target resource has been denied. (For example- if any of the parameter value is incorrect or license has expired)","customLabel":""}],"selectedLanguageId":"eXy7xHvpQ-HT16gZp2CNA"},"examples":{"languages":[{"id":"uvpR8QRnC1HHhN9QUoXG7","language":"python","code":"import requests\n\nmodelID=\"<< Enter Model ID >>\"\nurl = \"https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/\"+modelID+\"\"\n\n# please select proper payload for your usecase for extraction, evasion or poisoning.\npayload={\n # <>\n}\nheaders = {\n 'Accept': 'application/json',\n 'x-api-key': '########################################',\n 'Org-Id': '####################################################################################################'\n}\n\nresponse = requests.request(\"POST\", url, headers=headers, data=payload)\n\nprint(response.text)","customLabel":""},{"id":"vCV7cMMWnkOdXcZnZkdAz","language":"curl","code":"modelID=\"<< Enter Model ID >>\"\ncurl --location 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/${modelID}' \\\n--header 'x-api-key: ########################################' \\\n--header 'Org-Id: ####################################################################################################' \\\n--header 'Content-Type: application/json' \\\n--data '{\n <>\n}'","customLabel":""},{"id":"eXSnYGLUlaNuxX2kBNo0C","language":"nodejs","code":"var request = require('request');\n\nmodelID = '<>'\nvar options = {\n 'method': 'POST',\n 'url': 'https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/'+modelID+'',\n 'headers': {\n 'x-api-key': '########################################',\n 'Org-Id': '####################################################################################################',\n 'Content-Type': 'application/json'\n },\n body: JSON.stringify({\n // <>\n })\n\n};\nrequest(options, function (error, response) {\n if (error) throw new Error(error);\n console.log(response.body);\n});\n","customLabel":""},{"id":"z1GlBsBw28gqg4d6hM6ST","language":"javascript","code":"var myHeaders = new Headers();\nmyHeaders.append(\"x-api-key\", \"########################################\");\nmyHeaders.append(\"Org-Id\", \"####################################################################################################\");\nmyHeaders.append(\"Content-Type\", \"application/json\");\n\nvar raw = JSON.stringify({\n // << Enter Payload Details based on Task pair >>\n});\n\nvar modelID = \"<< Enter Model ID >>\"\n\nvar requestOptions = {\n method: 'POST',\n headers: myHeaders,\n body: raw,\n redirect: 'follow'\n};\n\nfetch(\"https://api.aws.boschaishield.com/prod/api/ais/v1.5/model_analyse/\"+modelID+\"\", requestOptions)\n .then(response => response.text())\n .then(result => console.log(result))\n .catch(error => console.log('error', error));","customLabel":""}],"selectedLanguageId":"uvpR8QRnC1HHhN9QUoXG7"},"description":"","currentNewParameter":{"label":"Path Parameter","value":"pathParameters"}}"}
:::
:::hint{type="info"}
Note: In the response, copy job\_id. This value is required to trigger the GET APIs. See [\ Job Metadata](docId\:S-mZ7r0HNzicDQy6Q-6Hq).
The "job\_id" is used to retrieve model analysis metadata and check the processing status of the request. It is also used for generating reports for the analyzed model. Copy the dashboard link from the response and open it in a new tab. This allows users to monitor the job progress and download reports.
:::
:::hint{type="info"}
For using Nodejs sample code, install npm package request
Given ample code for python is tested for Python version 3.7
Given Sample code for nodejs and javascript is tested for Node V20LTS
:::
[title] Time Series
[path] API Documentation/AISpectra/Automated RedTeaming for AI/ML/ Model Analysis/
::::LinkArray
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/33rkz7bKzjXOhHsFsTyAv_ehr-based-7.png"}
[Times Series Forecasting](docId\:EB7FsMB2O-fz1_RLafm9u)
Seamlessly analyze time series forecasting with accuracy and efficiency.
:::
::::
[title] Dashboard
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/
The dashboard provides a visual representation of your model information and vulnerabilities. It allows multiple team members to view both overall model insights and individual models for potential attacks. The dashboard presents various reports generated during model analysis, aiding in assessing model security.
The dashboard offers two distinct views:
1. ** **[Model Security](docId:9OO2m7pwETID4pL7vwyg7)** (**Developer View**)**: This view focuses on individual models, enabling users to access specific reports and check the model status regarding potential attacks.
2. [Overview](docId\:AsBqliw6rRXSoeg_P43Je)** (**Organization Level View**)**: This view provides a high-level overview of all models within the organization, presenting consolidated information about each model.
:::hint{type="info"}
To access the dashboard, you will need your Organization ID once the dashboard link is generated.
:::
[title] Databricks
[path] Integration Partners/MLOps/
Databricks is a cloud-based data engineering platform that helps organizations process and analyze large amounts of data. It is built on top of Apache Spark and offers tools for building and deploying machine learning models and processing streaming data. You can integrate AI Shield with Databricks to enhance model security.
Follow this reference implementation notebook to integrate AIShield to Databricks.
[title] Series Deployment
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/Threat Informed Defense/Deployment strategies/
In the Defense Deployment series, the Threat-Informed Defense Model is deployed sequentially just before the Original Model. When a user sends a request, it passes through the API gateway and load balancer before reaching the Pre-processor.
The processed data is then sent to the Defense Model. Based on the control signal received from the Defense Model, a decision is made whether to forward the request to the Original Model, block it, or take other necessary actions.
Telemetry data is sent to SIEM tools through a connector, similar to parallel deployment. However, due to the series deployment and control at the defense level, there may be a decrease in the accuracy of the Original Model.

[title] Azure ML
[path] Integration Partners/MLOps/
Azure ML is a cloud-based machine learning platform that allows organizations to build, train, and deploy machine learning models at scale. With its powerful tools and features, Azure ML simplifies the machine learning process, making it easier for developers and data scientists to create and deploy models quickly and efficiently. AIShield can seamlessly integrate with Azure ML, enhancing your model's security and helping you protect against malicious attacks.
Follow the reference implementation on GitHub to integrate AIShield with Azure ML.
### Requirenments:
1. Needed config.json file for the azure ml workspace. (You can download it under subscritpion)
2. Required traning python script file.
3. Required entry script also for deploying and querying the model.
4. provision a compute instance and delete after it .
5. needed azureml sdk version 1.41.0
[title] Clear ML
[path] Integration Partners/MLOps/
ClearML is an open source platform that simplifies the development and management of machine learning solutions for data science teams worldwide. It is an end-to-end MLOps suite that enables developers to focus on ML code and automation while ensuring reproducibility and scalability. To learn more, see Clear ML docs.
You can integrate AIShield with Clear ML. Follow the reference implementation on GitHub to integrate AIShield with Azure ML.
[title] Text
[path] API Documentation/AISpectra/Automated RedTeaming for AI/ML/ Model Analysis/
::::LinkArray
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/AW_nho6Fktjy4WJYAUVo6_machine-learning-nlp-text-classification.png"}
[Text Recommendation (Alpha-release)](docId\:pF0-V4Ug62-akwbXCLkoZ)
Its the process of categorizing text documents into predefined categories based on their content and context.
:::
::::
[title] Image
[path] API Documentation/AISpectra/Automated RedTeaming for AI/ML/ Model Analysis/
::::LinkArray
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/fe7OX1eSJl1WfnX17hHgp_ehr-based-6.png"}
[Image Classification](docId:7pfTV3D26cUJsz6vMQloO)
Seamlessly analyze image classification models with accuracy and efficiency
:::
::::
[title] Threat Informed Defense
[path] Platform guide/AISpectra/Automated RedTeaming for AI/ML/
AIShield defends against threats by deploying the Threat-Informed Defense Model in parallel or series to the Original Model, with telemetry data sent to SIEM tools.
::::LinkArray
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/UqumVTYbhTuHCPvQxRNGh_mourizal-zativa-gnmvpape3pe-unsplash.jpg"}
[Configuration of Connector](docId:1PrT1h1LSi-VzayWn1xjI)
:::
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/iEtwHwsZ-HiBZdy2S7TWt_amelie-mourichon-hclsa1miu3a-unsplash.jpg"}
[Deployment Strategies](docId\:bre9I0aeZkGxSL5AU-PY0)
:::
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/Xt5neLHuMrAE5CU4FMjtP_edgedevice.png"}
[Deployment on Edge Device](docId:_kZJJs4tSqMN3RO3nwm2W)
:::
:::LinkArrayItem{headerType="IMAGE" headerImage="https://archbee-image-uploads.s3.amazonaws.com/9GPi9YtROlYnoq5fgmmJ8/zvQDD7B1OIgXKscz4sCwN_ai-shield-image.png"}
[Defense deployment](docId\:SW_Dnk8pIKzpfnreXkfPA)
:::
::::